SC-500 Microsoft Certified: Cloud and AI Security Engineer Associate Questions and Answers
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You create a user-assigned managed identity, assign the identity to each virtual machine, and then add each managed identity to a role on storage1.
Does this meet the goal?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You add each virtual machine to a role on storage1.
Does this meet the goal?
You need to delegate a user to implement the planned change for Defender for Cloud. The solution must follow the principle of least privilege.
Which user should you choose?
You need to implement the planned change for storage2 The solution must meet the technical requirements for storage encryption.
What should you do?
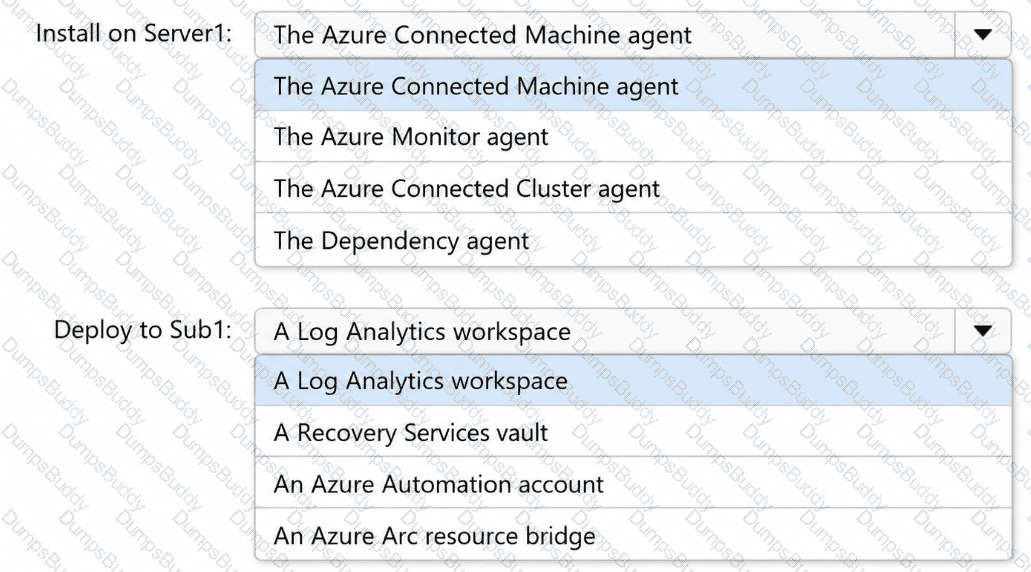
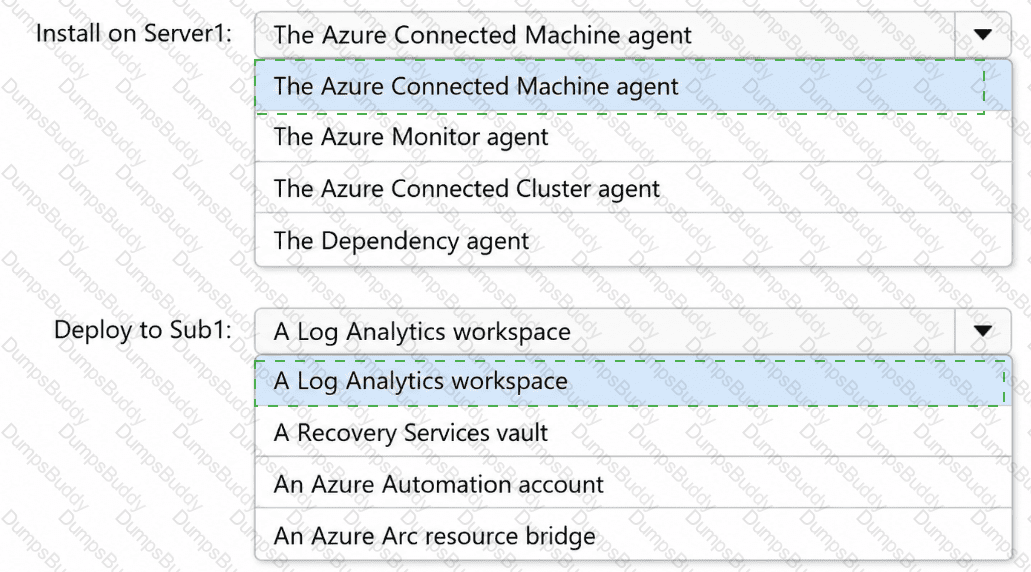
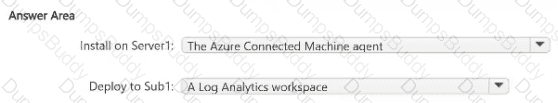
You need to configure Server1 to meet the technical requirements.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
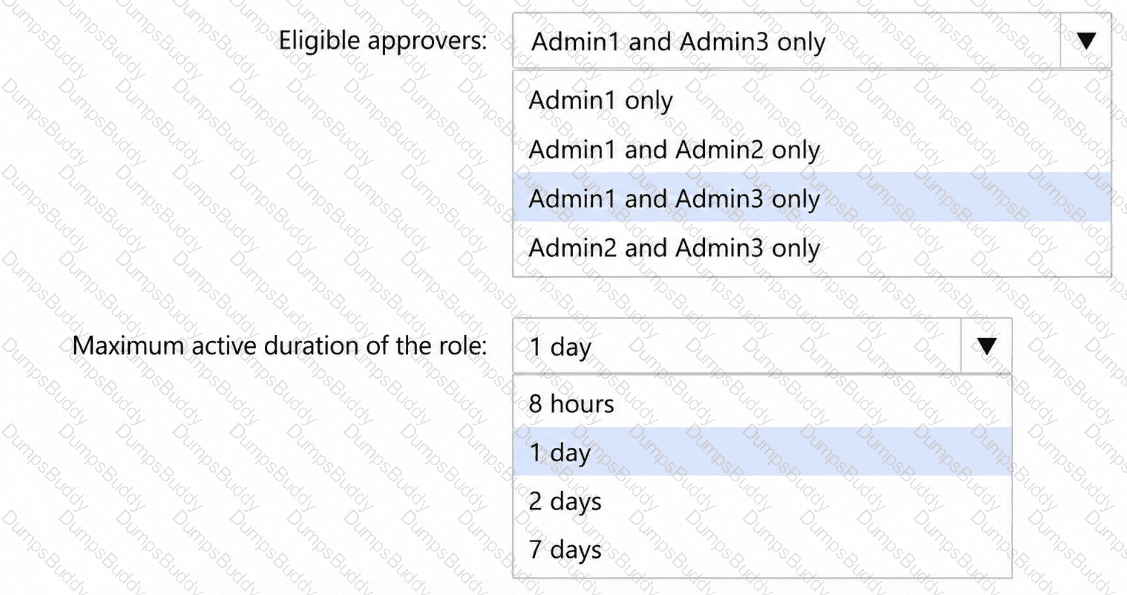
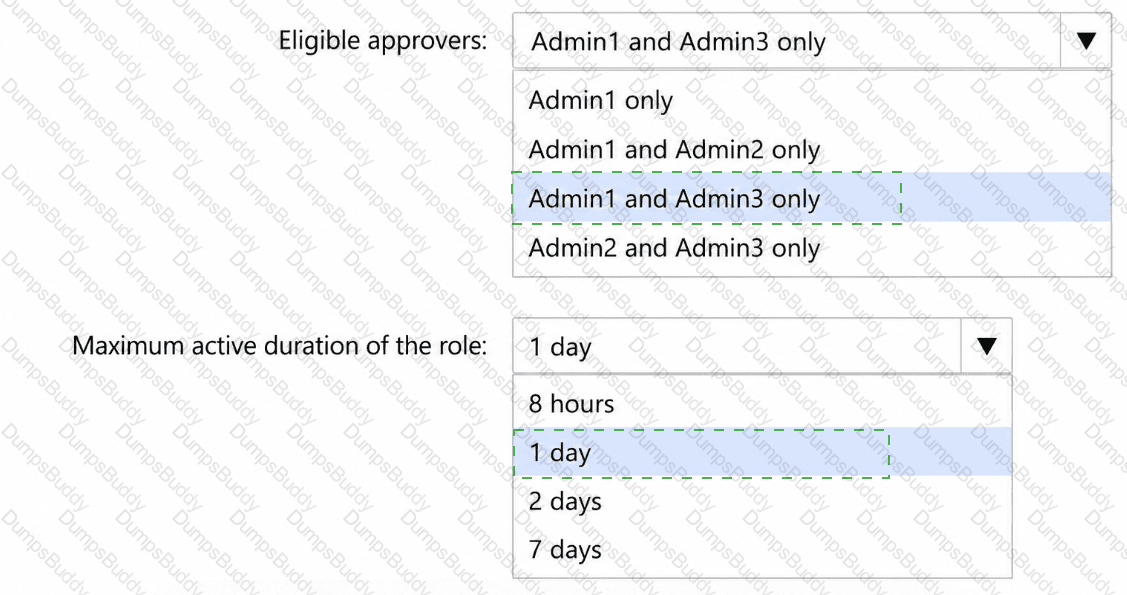
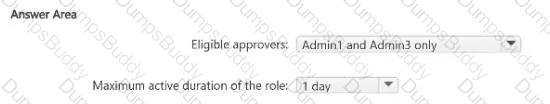
User1 has requested to use the AI Administrator role.
Which approvers can approve the request, and how long will User1 be an AI administrator after the role is approved? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You create a private endpoint on storage1.
Does this meet the goal?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create a playbook
Does this meet the goal?
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create an analytics rule.
Does this meet the goal?
You need to implement the function apps to meet the technical requirements.
Which apps should you include in the implementation?
You plan to deploy Microsoft 365 Copilot.
You discover that Copilot can access sensitive information in your Microsoft SharePoint Online libraries.
You need to automatically identify which SharePoint Online content has been shared between all internal users.
What should you create?
You have an Azure Subscription that contains the storage accounts shown in the following table.
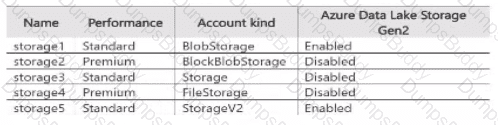
You enable Microsoft Defender for Storage.
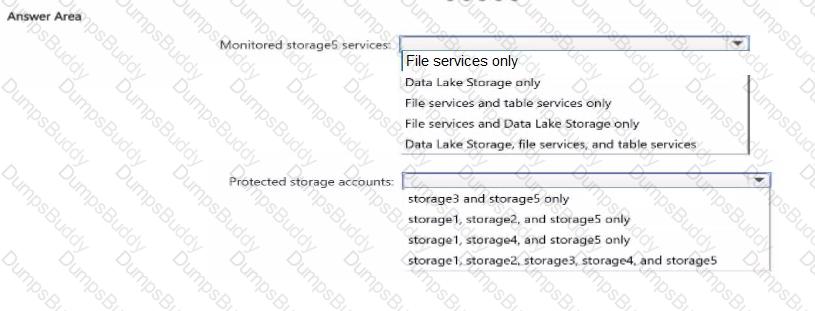
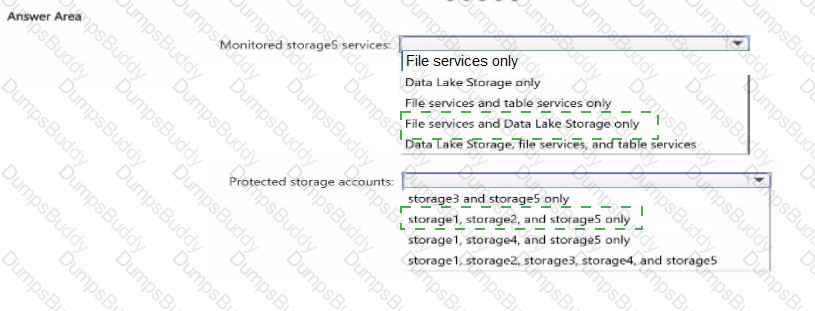
Which storage services of storage5 are monitored by Microsoft for Storage which storage accounts are protected by.
You have an Azure API Management instance named APIM1 that publishes an API named OrdersAPI. Applications call OrdersAPI by using Microsoft Entra access tokens.
A security review finds that requests that do NOT contain a valid access token can still be forwarded to OrdersAPI.
You need to ensure that APIM1 rejects requests that do NOT contain a valid Microsoft Entra token before the requests reach OrdersAPI.
What should you configure?
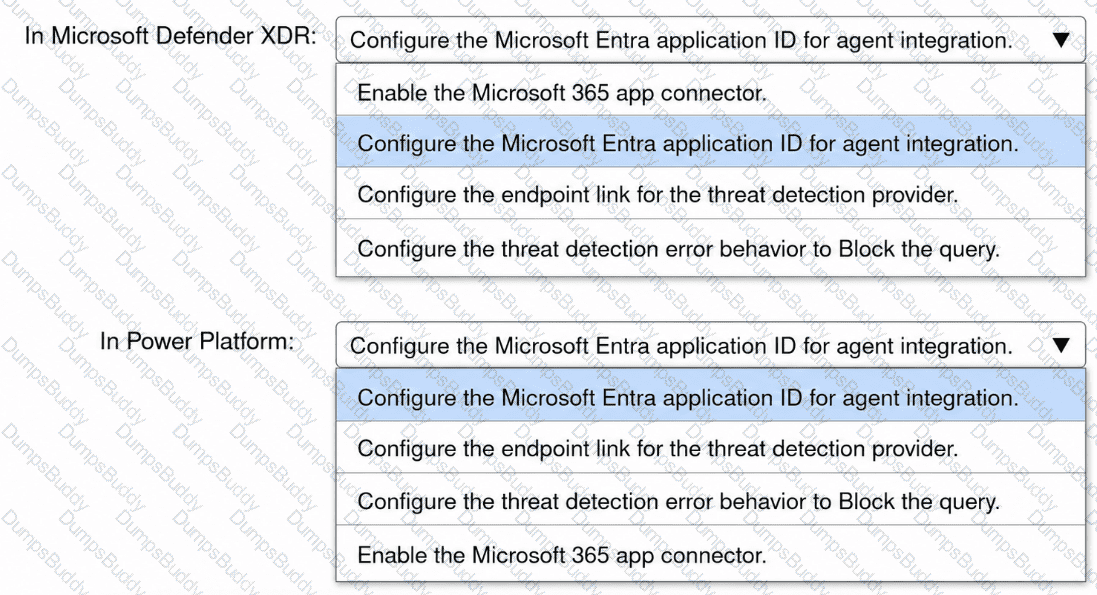
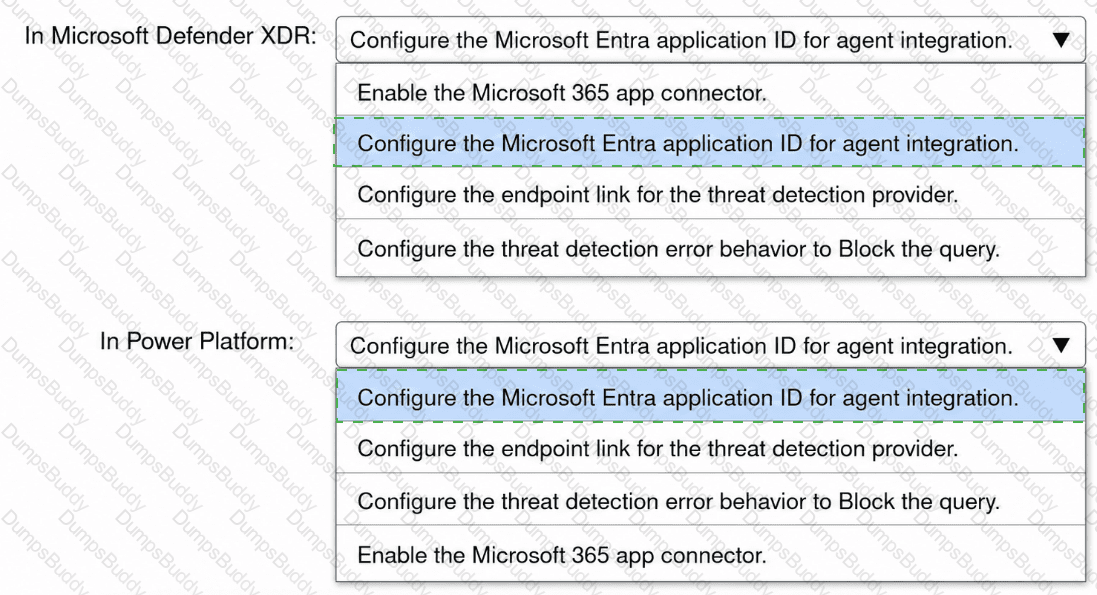
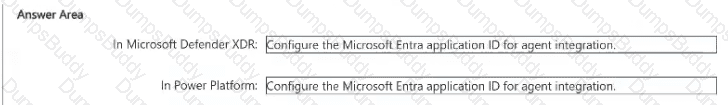
You have a Microsoft Defender XDR environment.
You have a Microsoft Power Platform environment where makers publish custom Microsoft Copilot Studio agents.
You need to enable real-time protection so that suspicious tool invocations are blocked before an agent runs actions, and related alerts appear in the Microsoft Defender portal.
What should you do? To answer, drag the appropriate actions to the correct services. Each action may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You have an Amazon Web Services (AWS) account connected to Defender for Cloud that has the Defender Cloud Security Posture Management (CSPM) plan enabled.
You need to identify the potential impact of security incidents that exploit multiple risks reported by Defender CSPM.
What should you use?
You use Azure Virtual Network Manager to manage multiple virtual networks in a network group named Group1
You discover that the virtual machines in Group1 are accessible from the internet by using TCP port 3389.
You need to block inbound TCP 3389 from the internet across all the virtual networks in Group1 The solution must minimize administrative effort.
What should you use?
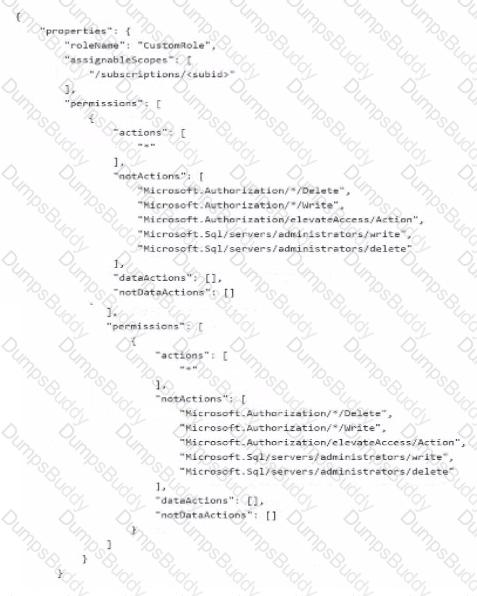
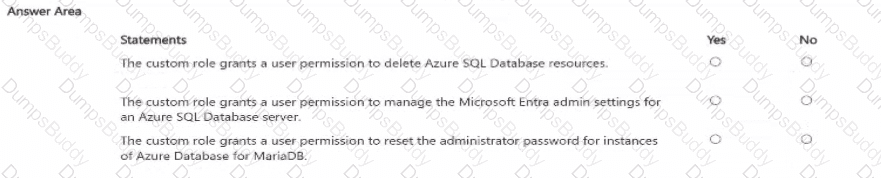
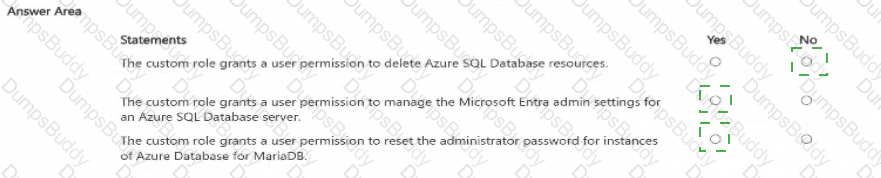
You have an Azure subscription.
You have the following custom role-based access control (RBAC) role definition
You have a Microsoft Security Copilot workspace named Workspace1 that is used by Security Operations Center (SOC) analysts and security administrators.
The SOC analysts use only the Security Copilot standalone experience, and the security administrators access Security Copilot from the Microsoft Defender portal.
A new Security Copilot workspace named Workspace2 is created for the security administrators. Workspace2 is assigned a capacity of five security compute units.
You need to ensure that Security Copilot usage for the SOC analysts is allocated to Workspace1 and Security Copilot usage for the security administrators is allocated to Workspace2.
What should you do?
Note. This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem
After you answer a question in this section, you will NOT be able to return. As a result these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution You create a hunting query.
Does this meet the goal’
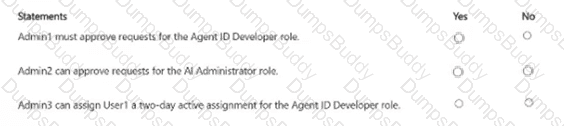
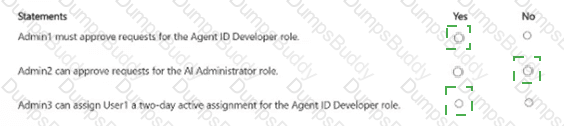
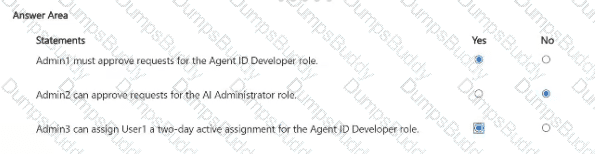
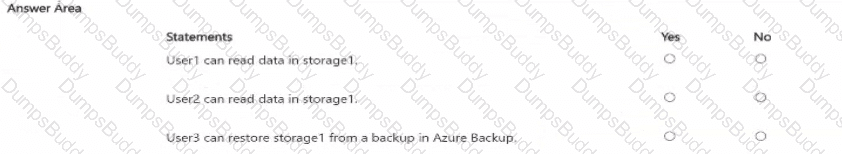
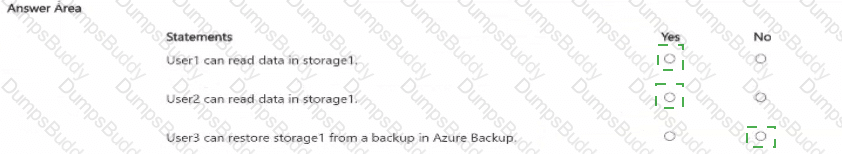
For each of the following statements, select Yes if the statement is true Otherwise, select No.
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft Sentinel workspace
You have a multi-tier Security Operations Center (SOC) team.
You need to ensure that all new security incidents are assigned immediately to the Tier 1 analysts group and flagged for triage.
Solution: You create an automation rule.
Does this meet the goal?
You need to implement the planned change for the AKS1 integration.
What should you configure for AKS1?
You need to configure Microsoft Sentinel to meet the technical requirements.
To what should you set Analytics retention for DnsEvents?
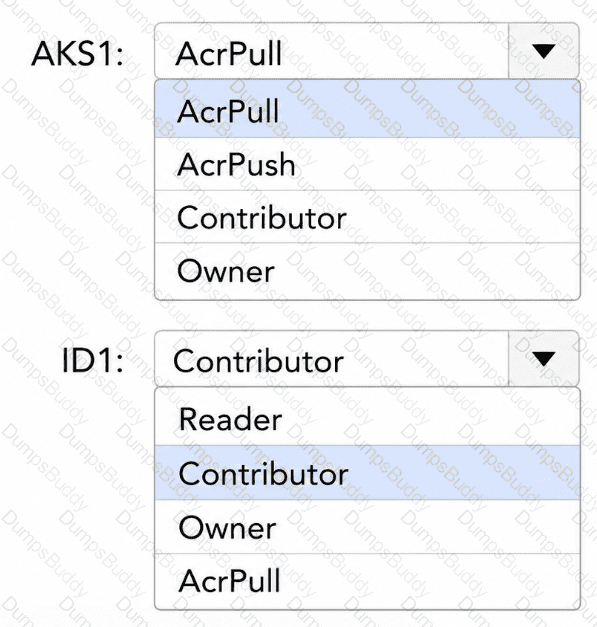
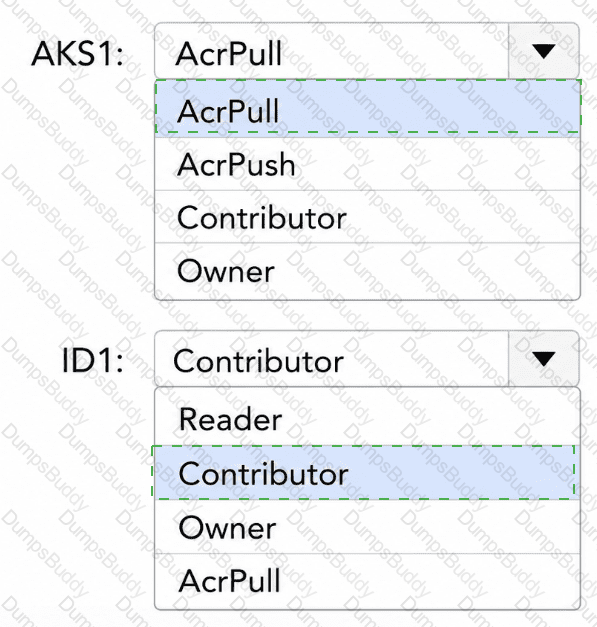
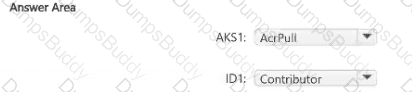
You need to configure the AKS1 and ID 1 managed identities to meet the technical requirements. The solution must follow the principle of least privilege.
Which role should you assign to each identity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You need to implement the planned change for SQLdb1
Which two actions should you perform? Each correct answer presents part of the solution.
NOTE: Each correct selection is worth one point
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have an Azure subscription that contains two virtual machines named VM1 and VM2. Each virtual machine has system-assigned managed identity enabled.
You have an Azure Storage account named storage1. Public access from all networks is enabled for storage1.
You need to ensure that VM1 and VM2 can access storage1.
Solution: You add each virtual machine to a security group, and then add the security group to a role on storage1.
Does this meet the goal?
You have an Azure subscription named Sub1 that contains a storage account named storage1. Sub1 has Microsoft Defender for Storage enabled. Defender for Storage has malware scanning enabled.
You need to configure a solution that automates the remediation of malware detected in storage1.
What should you include in the solution?
You have an Azure subscription named Sub1 that contains an Azure Database for PostgreSQL instance Sub1 has Microsoft Defender for Cloud enabled.
You need to configure Microsoft Defender for Databases to minimize costs.
Which Defender plan should you enable?
You have an Azure subscription that contains a resource group named RG1. RG1 contains a storage account named storage1. You have two custom Azure roles named Role1 and Role2 that are scoped to RG1. The permissions for Role1 are shown in the following JSON code.

You have a Microsoft Sentinel workspace named Workspace1.
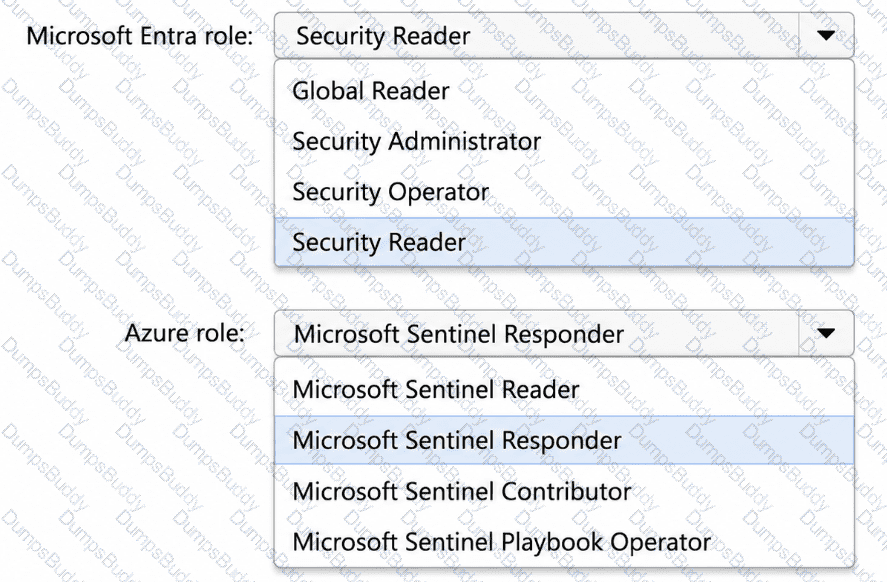
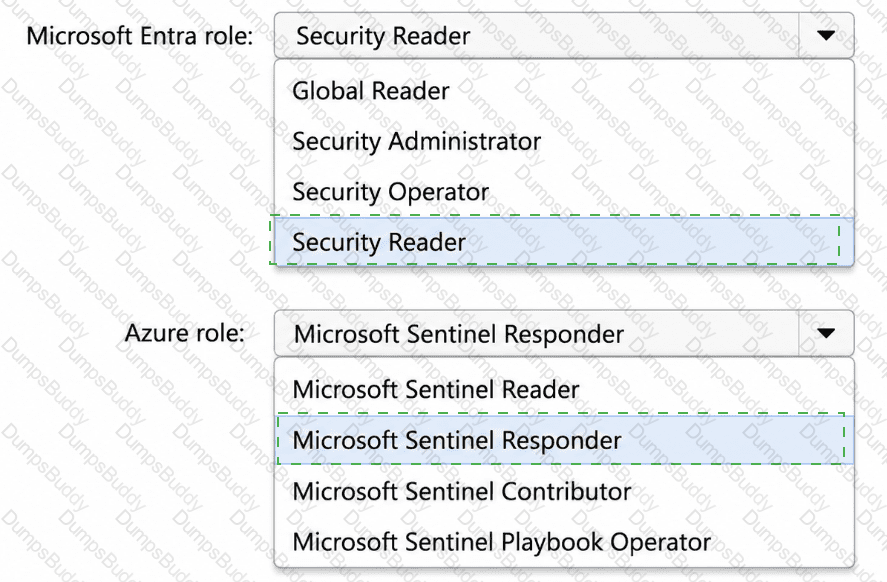
You hire a security consultant. You provide the consultant with a guest account named User1 in your Microsoft Entra tenant
You need to enable User1 to assign incidents in Workspace1.
Which roles should you assign to User1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
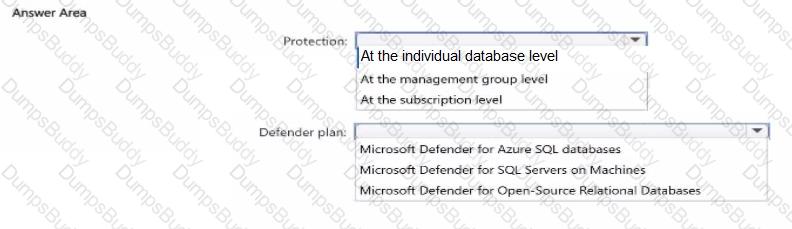
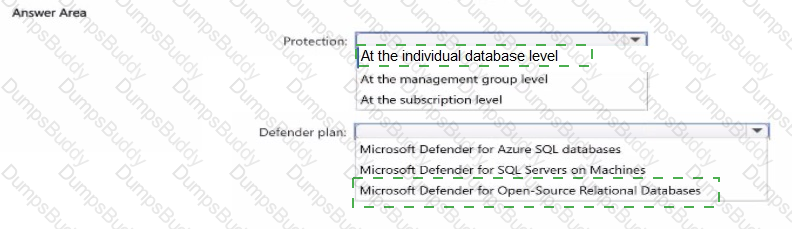
You have an Azure subscription that contains an Azure Database for PostgreSQL instance named 081.
You plan to protect OBI by using Microsoft Defender for Cloud.
You need to configure Defender for Cloud to detect anomalous activities and database exploitations for 061. The solution must NOT affect any other databases.
What should you enable? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
You have an Azure management group named MG1 that contains two subscriptions named Sub1 and Sub? Both subscriptions are linked to a Microsoft Entra tenant that contains a security group named Group!
You need to ensure that the members of Group1 can assign roles to the resources in Sub1 and Sub2. The solution must follow the principle of least privilege.
Which role should you assign to Group1?
You have two management groups named MG1 and MG2 that contain multiple Azure subscriptions. The subscriptions are linked to a Microsoft Entra tenant.
You have a user named User1 and a global administrator named Admin 1
You are informed that User1 created an Azure subscription named Sub1 under the MG2 management group and is the only owner of the subscription.
You need to ensure that Admin1 can remove the Owner role from User1 for Sub1.
What should you do first?
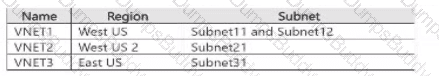
The subscription contains the virtual machines shown in the following table.
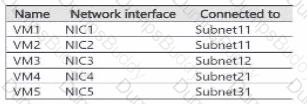
On Nl1I, you configure an application security group named ASG1.
On which other network interfaces can you configure ASG1?
You have an Azure API Management instance named APIM1.
You have a partner company that accesses an API in APIM1 by using subscription keys.
A backend API key is stored in a named value in APIM1.
Microsoft Defender for Cloud generates the following recommendation: “API Management secret named values should be stored in Azure Key Vault.”
You need to address the recommendation.
What should you do first?
You have a Microsoft 365 tenant that uses Microsoft Security Copilot and Microsoft Defender XDR.
Access to Microsoft Defender XDR is managed by using Microsoft entra global roles.
The Phishing triage Agent is available in Microsoft Defender. The required agent prerequisites and approvals are complete
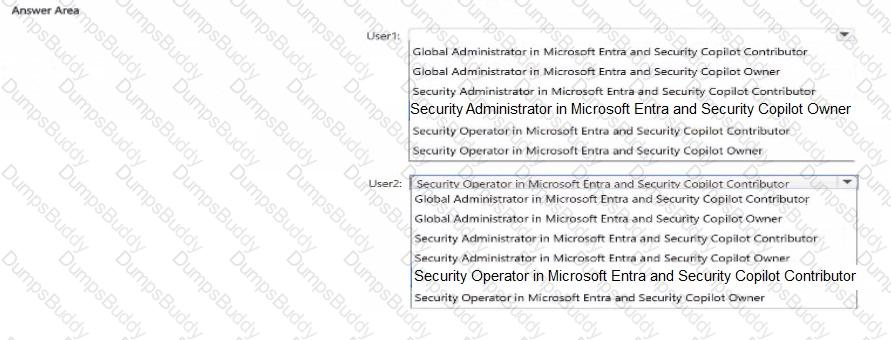
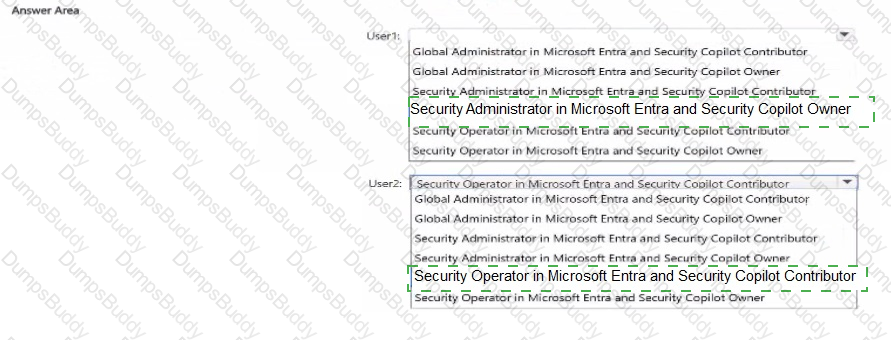
Two users will perform the following tasks:
• User1 will enable and manage the Phishing Triage Agent settings.
• User2 will use Security Copilot in Microsoft Defender XDR to manage phishing incidents identified by the agent.
You need to assign the least-privileged built in Microsoft Entra role and Security Copilot role combination to each us Which roles should you assign to each user? To answer, select the appropriate options in the answer area.
PDF + Testing Engine
Testing Engine
PDF (Q&A)