Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: best70

NSE5_FSW_AD-7.6 Fortinet NSE 5 - FortiSwitch 7.6 Administrator Questions and Answers

Questions 4

Which two statements about 802.1X authentication on FortiSwitch ports are true? (Choose two.)

Options:

A.

All hosts behind an authenticated port are allowed access after a successful authentication.

B.

A security policy is used to apply 802.1 authentication on a port.

C.

A local user database must be used to authenticate devices using the 802.1X authentication protocol.

D.

All devices connecting to FortiSwitch must support 802.1X authentication.

Buy Now
Questions 5

Refer to the exhibits.

NSE5_FSW_AD-7.6 Question 5

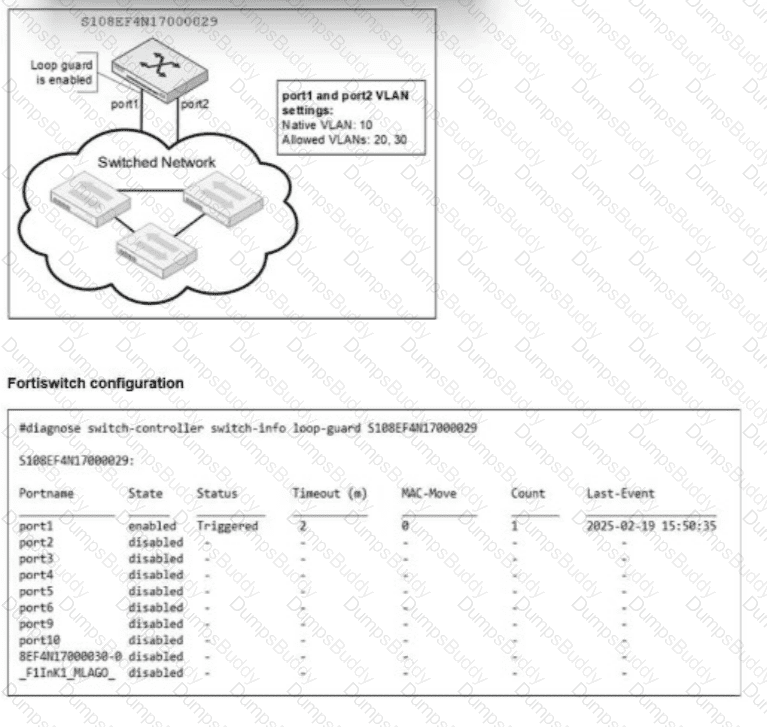
You are reviewing a FortiSwitch configuration where port1 and port2 are connected to a switched network. Loop guard is enabled on port1.

The CLI output shows that the port1 status is triggered due to loop guard. Which two conditions could have caused this shutdown? (Choose two.)

Options:

A.

A loop guard frame sent from port1 is received on port2.

B.

A loop guard frame sent from port1 is received back on port1.

C.

Loop guard is triggered because port2 did not send any bridge protocol data units (BPDU).

D.

Loop guard is triggered because the port detected excessive traffic.

Buy Now
Questions 6

Which statement about the IGMP snooping querier when enabled on a VLAN is true?

Options:

A.

Active multicast receiver entries are aging on each IGMP query sent on the VLAN

B.

IGMP reports on the VLAN are forwarded to all switch ports.

C.

The setting can only be enabled using the FortiSwitch CLI.

D.

All other indirectly connected switches will be unable to get IGMP multicast traffic.

Buy Now
Questions 7

What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?

Options:

A.

Use a migration tool based on python script to convert the configuration

B.

Enable the Forti-link setting on FortiSwitch before the authorization process

C.

FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.

D.

Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.

Buy Now
Questions 8

What does the switchauto-networksetting control on FortiSwitch? (Choose one answer)

Options:

A.

The automatic VLAN assignment based on connected devices

B.

The automatic discovery of the FortiGate- > FortiLink interface

C.

The root bridge priority for Multiple Spanning Tree Protocol (MSTP)

D.

Whether the FortiSwitch can be managed by FortiManager

Buy Now
Questions 9

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 9

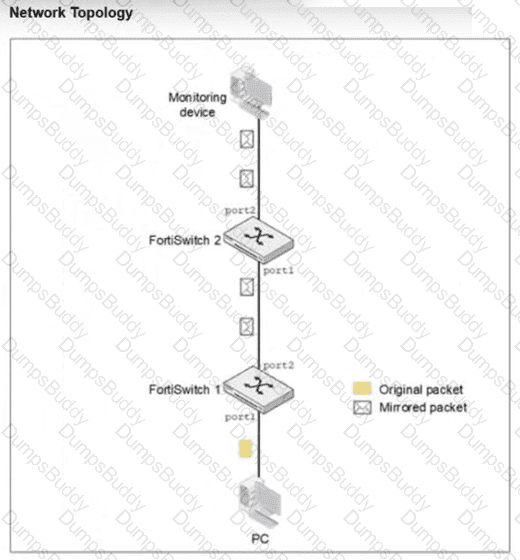
You configured Switched Port Analyzer (SPAN) to monitor traffic from a source port on FortiSwitch 1, but the monitoring device is connected to FortiSwitch 2. After port mirroring configuration on FortiSwitch 1, the monitoring device is not receiving any mirrored traffic.

What is the most likely reason the mirrored traffic is not reaching the monitoring device? (Choose one answer)

Options:

A.

SPAN does not support forwarding mirrored traffic across multiple switches.

B.

SPAN traffic must be filtered with an access control list (ACL).

C.

The SPAN session must be restarted after configuration.

D.

The monitoring device must use a management IP in the same subnet.

Buy Now
Questions 10

You are deploying a new FortiSwitch device in a branch office and you want it to be automatically detected and managed by FortiGate. Which FortiSwitch feature enables automatic detection during deployment? (Choose one answer)

Options:

A.

Zero-touch deployment

B.

Auto-discovery

C.

Link Layer Discovery Protocol (LLDP)

D.

FortiLink heartbeat

Buy Now
Questions 11

What are two reasons why time synchronization between FortiGate and its managed FortiSwitch is critical in switch management? (Choose two.)

Options:

A.

FortiSwitch does not retain its time after a reboot, which gets reset after each reboot.

B.

FortiSwitch will not be able to become an NTP server for downstream devices.

C.

FortiSwitch cannot complete the DTLS handshake used in the CAPWAP tunnel.

D.

FortiSwitch will not allow other FortiSwitch devices in the chain be discovered by FortiGate.

Buy Now
Questions 12

Refer to the exhibits

NSE5_FSW_AD-7.6 Question 12

NSE5_FSW_AD-7.6 Question 12

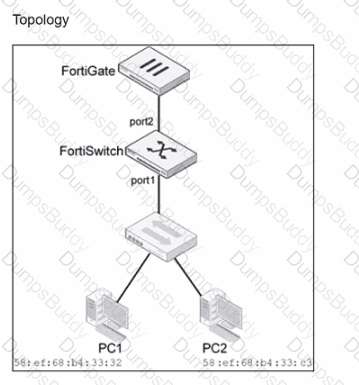
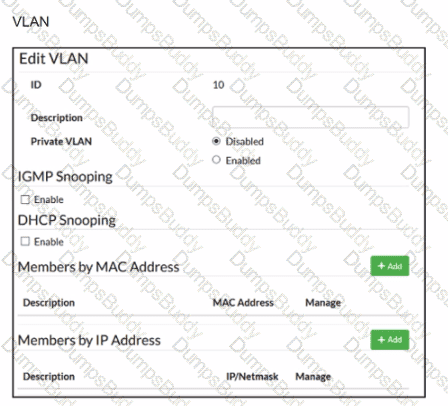
Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch. Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)

Options:

A.

Add the MAC address of PC1 as a member of VLAN 10.

B.

Add VLAN ID 10 as a member of the untagged VLANs on port1.

C.

Remove VLAN 10 from the allowed VLANs and add it to untagged VLANs on port1.

D.

Enable Private VLAN on VLAN 10 and add VLAN 20 as an isolated VLAN.

Buy Now
Questions 13

In which two ways can you assign a FortiSwitch port to a VDOM using a multi-tenancy setup? (Choose two answers)

Options:

A.

Assign the switch port to a VLAN on FortiGate and perform VDOM mapping.

B.

Create a virtual port pool on the FortiGate CLI.

C.

Assign a port to a VDOM directly on the managed FortiSwitch.

D.

Switch the FortiLink interface to the target VDOM.

Buy Now
Questions 14

(Full question statement start from here)

What is an advantage of using a FortiSwitch stack in managed switch mode with FortiGate when deploying VLANs? (Choose one answer)

Options:

A.

FortiGate executing the routing and FortiSwitch managing its configuration.

B.

Ensuring VLAN traffic can pass between connected switches in the stack.

C.

FortiGate no longer needing to manage any VLAN configuration.

D.

FortiGate provides visibility and control for inter-vlan traffic.

Buy Now
Questions 15

Exhibit.

NSE5_FSW_AD-7.6 Question 15

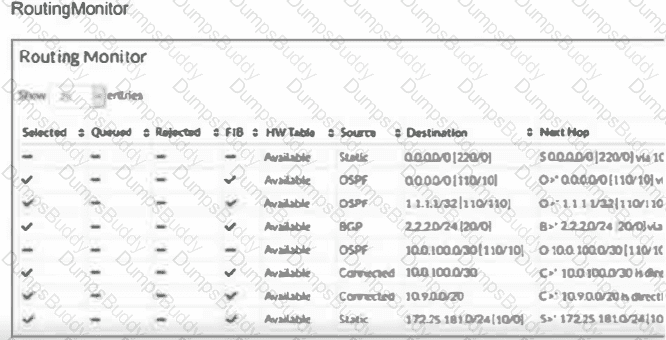
Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)

Options:

A.

These two routes have a higher administrative distance value available to the destination networks.

B.

These two routes will become primary, if the best routes are removed.

C.

These two routes will be used as load-balancing routes.

D.

These two routes are available in the hardware routing table.

Buy Now
Questions 16

Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)

Options:

A.

A FortiLink interface must be enabled on FortiGate.

B.

The switch controller feature must be enabled on FortiGate.

C.

Only a hardware-based FortiGate can manage a FortiSwitch stack.

D.

FortiSwitch must be operating in standalone mode before authorization.

Buy Now
Questions 17

In which two ways can you assign a FortiSwitch port to a VDOM using multi-tenancy setup? (Choose two.)

Options:

A.

Switch the FortiLink interface to the target VDOM.

B.

Remove the managed FortiSwitch and allocate ports directly on FortiSwitch.

C.

Create a virtual port pool on the FortiGate CLI.

D.

Assign a port to a VDOM directly on the managed FortiSwitch.

Buy Now
Questions 18

Exhibit.

port1 and port2 are the only ports configured with the same native VLAN 10.

What are two reasons that can trigger port1 to shut down? (Choose two.)

Options:

A.

port1 was shut down by loop guard protection.

B.

STP triggered a loop and applied loop guard protection on port1.

C.

An endpoint sent a BPDU on port1 that it received from another interface.

D.

Loop guard frame sourced from port1 was received on port1.

Buy Now
Questions 19

Refer to the exhibit.

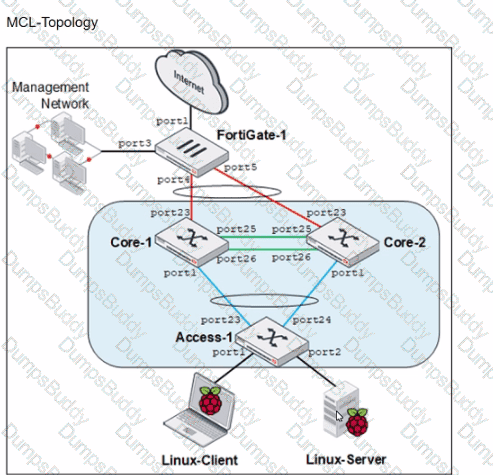
NSE5_FSW_AD-7.6 Question 19

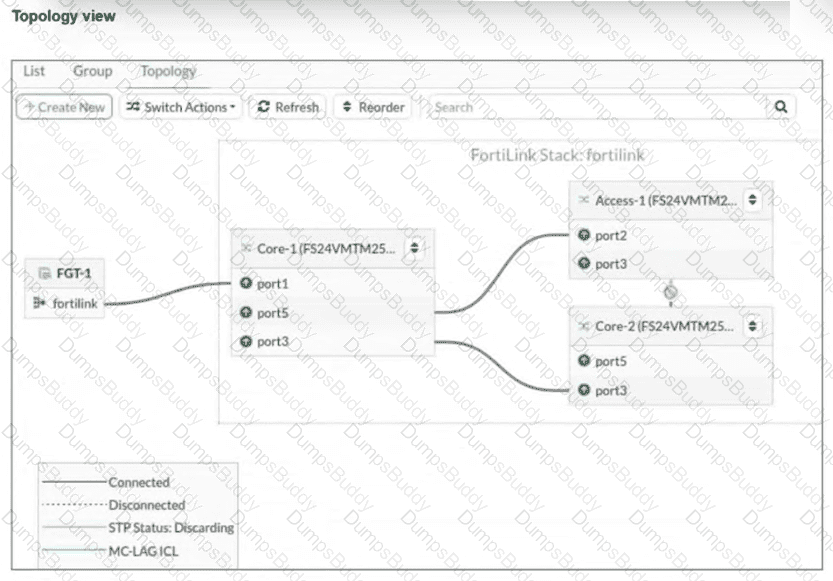
You just connected three FortiSwitch devices:Core-1,Core-2, andAccess-1. Core-1 and Core-2 both connect to Access-1 for redundancy. All switches are managed by FortiGate, which uses port4 as the FortiLink interface. After you enable the uplink ports on Core-2, you notice that port3 on Access-1 enters the Discarding STP state. What is the most likely cause of this behavior? (Choose one answer)

Options:

A.

Bridge Protocol Data Unit (BPDU) Guard is enabled, which shuts down the port after it receives BPDUs.

B.

Access-1 is not authorized by FortiGate.

C.

Core-2 has the lowest bridge priority.

D.

FortiGate is not running Spanning Tree Protocol (STP) on the FortiLink interface.

Buy Now
Questions 20

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 20

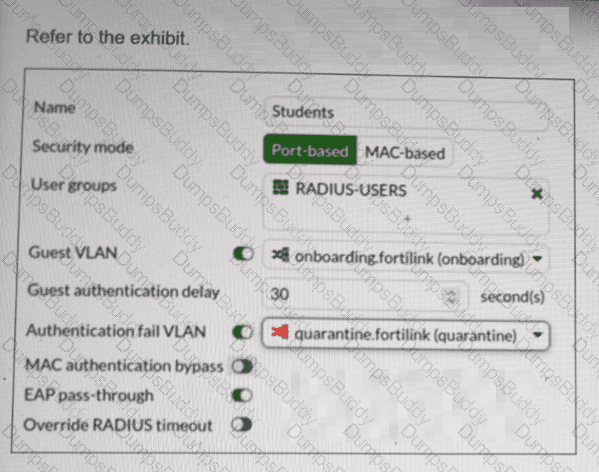
FortiSwitch 802.1X port security configuration is shown. A user connects their laptop to the port and attempts to authenticate using 802.1X, but enters the wrong credentials multiple times. What will the result to the device be? (Choose one answer)

Options:

A.

The device will be placed into the VLAN quarantine.

B.

The port will shut down for security reasons.

C.

The device will be placed into the VLAN onboarding.

D.

The device will be assigned to the default management VLAN.

Buy Now
Questions 21

What happens when a routed VLAN interface (RVI) is configured on a FortiSwitch port or trunk? (Choose one answer)

Options:

A.

VLAN 1 is automatically assigned for management.

B.

The port becomes a layer 3 interface with VLAN 4095 assigned automatically.1

C.

All VLANs on the port are terminated in a trunk by default.

D.

The port becomes a layer 3 interface and assigned to VLAN 1.

Buy Now
Questions 22

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 22

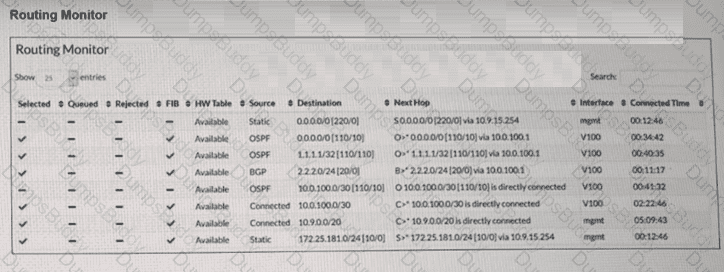
Two routes in the routing monitor are marked as available but are not installed in the forwarding information base (FIB). Which statement correctly explains why the routes have this status? (Choose one answer)

Options:

A.

They are excluded from the FIB because a more preferred route exists for the same destination.

B.

They are unavailable due to invalid next-hop addresses.

C.

They are not included in the FIB due to route-policy filtering.

D.

They are installed in the FIB but cannot be offloaded to hardware.

Buy Now
Questions 23

(Full question statement start from here)

How does enabling an IGMP snooping proxy on FortiSwitch help reduce the number of IGMP reports processed by the IGMP querier? (Choose one answer)

Options:

A.

By converting IGMP reports into broadcast packets to reach all VLAN members

B.

By converting IGMP traffic to unicast

C.

By suppressing duplicate IGMP reports within the VLAN

D.

By forwarding IGMP reports only when the first member joins and the last member leaves

Buy Now
Questions 24

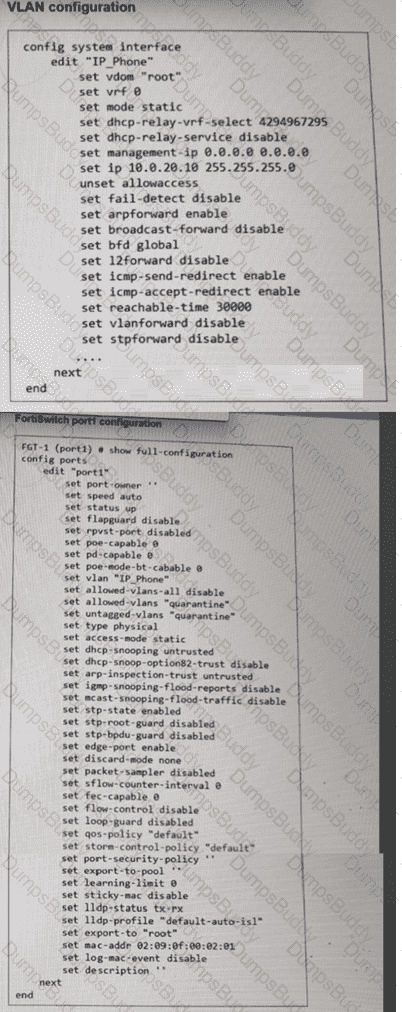
You are managing FortiSwitch ports from a FortiGate device with multiple VDOMs. Which two methods can you use to assign FortiSwitch ports to VDOMs? (Choose two answers)
Options:

A.

Assigning the port directly to a specific VDOM for dedicated physical isolation

B.

Use FortiGate policies to control inter-VDOM traffic for FortiSwitch ports

C.

Use interface role mapping to dynamically assign FortiSwitch ports to VDOMs based on Dynamic Host Configuration Protocol (DHCP) scope

D.

Using a virtual port pool (VPP) to create virtualized ports that can be assigned to different VDOMs

Buy Now
Questions 25

FortiGate is unable to establish a tunnel with the FortiSwitch device it is supposed to manage Based on the debug output shown in the exhibit, what is the reason for the failure?

Options:

A.

The handshake process timed out before FortiSwitch responded.

B.

DTLS client hello had the incorrect pre-shared key.

C.

The CAPWAP tunnel failed to come up due to a mismatch in time.

D.

FortiSwitch has disabled FortiLink and is only managed as a standalone.

Buy Now
Questions 26

Which statement about using MAC, IP, and protocol-based VLANs on FortiSwitch is true?

Options:

A.

lt is a scalable and secure solution in comparison to other Layer 2 security measures.

B.

FortiSwitch uses only the Ethernet type to assign traffic to VLANs.

C.

It provides benefits that can be obtained when using 802.1X authentication.

D.

Endpoints are required to use the same FortiSwitch port to remain members of the VLAN.

Buy Now
Questions 27

Refer to the configuration:

Which two conditions does FortiSwitch need to meet to successfully configure the options shown in the exhibit above? (Choose two.)

Options:

A.

The FortiSwitch model is equipped with a maximum of 54 interfaces

B.

FortiSwitch would need to be rebooted.

C.

The split port can be assigned to a native VLAN.

D.

The Dort full speed prior to the split was 100G QSFP+.

Buy Now
Questions 28

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 28

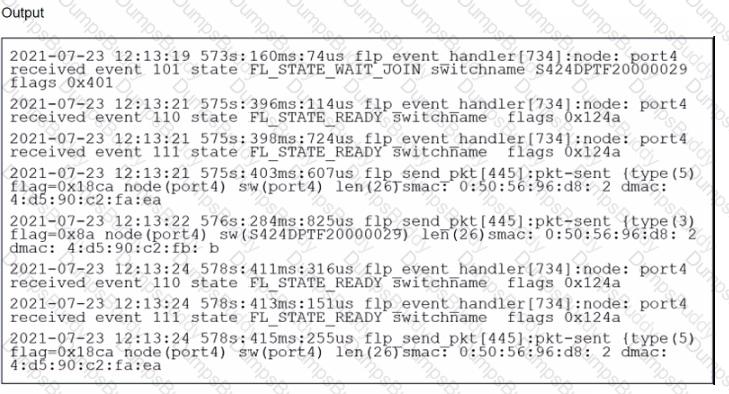
Which two statements best describe what is displayed in the FortiLink debug output shown in the exhibit? (Choose two.)

Options:

A.

FortiSwitch is sending FortiLink heartbeats to FortiGate.

B.

FortiSwitch is discovered and authorized by FortiGate.

C.

FortiSwitch is in a waiting state to join the stack group on FortiGate.

D.

FortiSwitch is ready to push its new hostname to FortiGate.

Buy Now
Questions 29

Refer to the exhibit.

NSE5_FSW_AD-7.6 Question 29

Core-1 and Access-1 are managed and authorized by FortiGate-1. which uses port4 as the FortiLink interface. After FortiGate authorizes and manages Core-2. Port1 status becomes STP discarding.

Why is port1 in the discarding state?

Options:

A.

port1 on Core-2 is discarding only management traffic.

B.

Core-1 and Core-2 do not have MCLAG configuration.

C.

Access-1 is the root bridge and can only have one root port.

D.

Core-2 has the lowest bridge priority.

Buy Now
Questions 30

Which QoS mechanism maps packets with specific class of service (COS) or Differentiated Services Code Point (DSCP) markings to an egress queue? (Choose one answer)

Options:

A.

Classification for ingress traffic

B.

Queuing for egress traffic

C.

Policing for ingress traffic

D.

Shaping for egress traffic

Buy Now
Questions 31

An administrator must deploy managed FortiSwitch devices in a remote location where multiple VLANs must be used to segment devices. No layer 3 switch or router is present at the site, and the only WAN connectivity is an ISP-provided router connected to the public internet. Which two components are required to enable VLAN segmentation across this remote site? (Choose two answers)

Options:

A.

FortiGate and FortiSwitch configured with VXLAN to tunnel VLANs over the WAN

B.

A layer 3 router at the remote location to handle inter-VLAN routing

C.

A FortiSwitch model that supports VXLAN hardware acceleration

D.

FortiSwitch and FortiGate devices configured with IPsec interfaces

E.

FortiGate with a layer 3 interface to terminate the VXLAN overlay

Buy Now
Questions 32

Which two rules used by MSTP are similar to rules used by other STP methods? (Choose two.)

Options:

A.

MSTP uses port role election, similar to rapid STP on the instances.

B.

MSTP uses alternate path and primary path, similar to regular STP.

C.

MSTP uses root bridge selection, similar to rapid STP

D.

MSTP uses timers for transitioning the ports, similar to regular STP.

Buy Now
Questions 33

Which statement about the configuration of VLANs on a managed FortiSwitch port is true?

Options:

A.

Untagged VLANs must be part of the allowed VLANs: ingress and egress.

B.

FortiSwitch VLAN interfaces are created only when FortiSwitch is managed by Forti-Gate.

C.

The native VLAN is implicitly part of the allowed VLAN on the port.

D.

Allowed VLANS expand the collision domain to the port.

Buy Now
Questions 34

Which statement best describes a benefit of using MAC, IP address, or protocol-based VLAN assignments on FortiSwitch? (Choose one answer)

Options:

A.

It disables 802.1X authentication while preserving user access control.1

B.

It requires devices to authenticate through a RADIUS server before VLAN tagging.

C.

It assigns ports to VLANs regardless of device type or traffic.

D.

It offers dynamic segmentation benefits similar to 802.1X authentication.2

Buy Now
Exam Code: NSE5_FSW_AD-7.6
Exam Name: Fortinet NSE 5 - FortiSwitch 7.6 Administrator
Last Update: Sep 17, 2026
Questions: 114

PDF + Testing Engine

$134.99

Testing Engine

$99.99

PDF (Q&A)

$84.99