Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: best70

SPLK-5002 Splunk Certified Cybersecurity Defense Engineer Questions and Answers

Questions 4

Which of the following should an engineer do as they evaluate their Threat Detection and Incident Response lifecycle?

Options:

A.

Focus efforts on the least impactful threat vectors.

B.

Use the MITRE ATT & CK Framework to evaluate the organization ' s risk appetite.

C.

Evaluate the threat process lifecycle solely from predefined technical profiles.

D.

Evaluate the threat process lifecycle based on contextual business and industry knowledge.

Buy Now
Questions 5

Which REST call will show a list of alerts with their specific commands, app, and title?

Options:

A.

| rest /servicesNS/admin/-/alerts/alert_actions

| table title, eai:acl.app, label, payload_format, command

B.

| rest /servicesNS/user/-/alerts/alert_actions

| table title, eai:acl.app, label, payload_format, command

C.

| rest /servicesNs/admin/-/actions/alert_actions

| table title, eai:acl.app, label, payload_format, command

D.

| rest /servicesNS/user/-/actions/alert_actions

| table title, eai:acl.app, label, payload_format, command

Buy Now
Questions 6

An engineer needs to create a new report capturing the vendors and products that detect a particular CVE in their environment. How can they ensure that the search associated with the report only includes accelerated data?

Options:

A.

Search vendor_product within the Vulnerabilities data model using a standard search.

B.

Search the Updates data model for vendor/product information.

C.

Search for the CVE within the Vulnerabilities data model using tstats, grouped by vendor_product.

D.

Search vendor_product within the Updates data model using tstats.

Buy Now
Questions 7

If a correlation search cannot be run at the configured time, which scheduling option should an engineer use to ensure there are no backfill gaps in data?

Options:

A.

Default

B.

Continuous

C.

Real-time

D.

Auto

Buy Now
Questions 8

An engineer adds a custom event status of ' Testing ' and accidentally makes it the new default status. Their SOC calculates some metrics based on Notable status change sequences, starting from the old default status of ' New ' . Which metrics can be affected by this mistake?

Options:

A.

Mean Time to Respond, Mean Time to Resolve

B.

No metrics are impacted

C.

Mean Time to Triage, Dwell Time

D.

Mean Time to Resolve, Dwell Time

Buy Now
Questions 9

An engineer has been working on building a new automation for the SOC. What Scope should be selected in the SOAR Playbook Debugger during the playbook development to ensure consistency?

Options:

A.

New Events

B.

All Artifacts

C.

New Artifacts

D.

All Events

Buy Now
Questions 10

Which of the following is not a type of metadata that can be returned by the metadata command?

Options:

A.

hosts

B.

sources

C.

assets

D.

sourcetypes

Buy Now
Questions 11

When creating detections, which of the following sequences would result in the most performant SPL query?

Options:

A.

Define base query, combine/summarize data, minimize data, execute calculations, format the data

B.

Define base query, minimize data, combine/summarize data, execute calculations, format the data

C.

Define base query, minimize data, combine/summarize data, format the data, execute calculations

D.

Define base query, minimize data, format the data, combine/summarize data, execute calculations

Buy Now
Questions 12

The Director of Security would like to understand the operational efficiency of the SOC analysts at a high level. What is a metric that can be used to determine their efficiency?

Options:

A.

MTTI

B.

MTBR

C.

MTTR

D.

MTTD

Buy Now
Questions 13

In the context of Splunk ' s Common Information Model (CIM), which construct ensures that events from different data sources appear in the applicable data model?

Options:

A.

Hosts

B.

Tags

C.

Assets

D.

Field names

Buy Now
Questions 14

A detection engineer is using a threat defense informed strategy to define use cases. Which Splunk app would best facilitate their use case development process by cross referencing detections with the MITRE ATT & CK Framework?

Options:

A.

Enterprise Security Content Update App

B.

Splunk Security Essentials App

C.

Enterprise Security

D.

Supporting add-on for MITRE ATT & CK

Buy Now
Questions 15

The SOC manager has a desire to measure mean time to acknowledge finding (notable event) in order to meet a desired service-level objective. Which two fields can be used to measure the difference?

Options:

A.

Status, Owner

B.

Urgency, Status

C.

Severity, Owner

D.

User, Status

Buy Now
Questions 16

Which of the following macro values will exclude all of the company networks if it is called from the following search?

index=firewall sourcetype=pan\:traffic NOT " company_networks "

Options:

A.

(src_ip IN (151.157.30.0/24, 26.06.18.0/24))

B.

NOT (src_ip IN (151.157.30.0/24, 26.06.18.0/24))

C.

NOT (src_ip=151.157.30.0/24 AND src_ip=26.06.18.0/24)

D.

(src_ip=151.157.30.0/24 AND src_ip=26.06.18.0/24)

Buy Now
Questions 17

When setting Common Information Model (CIM) accelerations, which parameter should be defined to set how far back in time (specified as a relative time string) the Splunk platform creates its column stores?

Options:

A.

Max summarization search time

B.

Backfill range

C.

Accelerate until maximum time

D.

Summary range

Buy Now
Questions 18

Based on a recent red team exercise, an organization is highly concerned about pass the hash attacks especially including tools like Empire. Which EventCode associated to PowerShell Script Block Logging would be used to detect this activity?

Options:

A.

EventCode=4126

B.

EventCode=4168

C.

EventCode=4624

D.

EventCode=4104

Buy Now
Questions 19

A Detection Engineer works closely with SOC leads to define expected analyst workflow, often documented as a Standard Operating Procedure (SOP). Which capability can be used to document expected analyst actions in an investigation?

Options:

A.

Response templates

B.

Correlation Search Editor

C.

Adaptive response actions

D.

Investigation notes

Buy Now
Questions 20

What is a key feature of effective security reports for stakeholders?

Options:

A.

High-level summaries with actionable insights

B.

Detailed event logs for every incident

C.

Exclusively technical details for IT teams

D.

Excluding compliance-related metrics

Buy Now
Questions 21

A new playbook needs to be developed for automated phishing analysis and response. Configured in SOAR are integrations with Splunk Enterprise Security and actions from assets that pull in user-reported emails, perform automated threat analysis, add blocks on the proxy, and an EDR vendor to take various actions. Which would be the best workflow for the new playbook?

Options:

A.

Ingest the email from the mail vendor

Detonate email in the automated threat analysis system and collect verdict, looking for malicious indicators

Search the mail system for all users that received the email

Block any malicious URLs and processes with the proxy and EDR solutions

B.

Submit the user reported email from Splunk Enterprise Security

Search the mail system for all users that received the email

Review results from the automated threat analysis

Block any malicious URLs and processes with the proxy and EDR solutions

C.

Submit the email from Splunk Enterprise Security

Search the mail system for all users that received the email

Review results from the automated threat analysis

Block any malicious URLs and processes with the proxy and EDR solutions

D.

Ingest the email from the mail vendor

Detonate email in the automated threat analysis system and collect verdict, looking for malicious indicators

Search the mail system for all users that received the email

Block all URLs and processes with the proxy and EDR solutions

Buy Now
Questions 22

What does the following search do?

source=WinEventLog:security* sourcetype= " WinEventLog* " EventCode=4688

| stats count, values(process) as process by parent_process_name

Options:

A.

Displays a count of processes created by the same user.

B.

Displays a list of newly created processes and the user that created them.

C.

Displays a count of processes created by the same child process.

D.

Displays a list of processes and their parent processes.

Buy Now
Questions 23

What external support consideration should an engineer account for if they plan to automate the disabling of a system or user?

Options:

A.

Communicate the actions to the IT Help Desk.

B.

Enable logging on the playbook.

C.

Validate that the system or user is not already disabled.

D.

Add the " support " tag to the playbook.

Buy Now
Questions 24

What must be configured as a setting in a correlation search for a notable to be generated?

Options:

A.

A SOAR playbook must execute against the notable.

B.

Nothing; the correlation search will generate a notable automatically as an outcome.

C.

An Adaptive Response Action must be configured to enable the notable generation.

D.

The search must end with a | notable SPL command.

Buy Now
Questions 25

Which stats event field created by an adaptive response action allows for troubleshooting the correlation search that created the notable event?

Options:

A.

orig_sid

B.

risk_sid

C.

search_sid

D.

result_sid

Buy Now
Questions 26

In a contextualization playbook, a URL is transmitted to a sandbox for examination and disposition recommendation. What underlying HTTP method is used to transmit this data to the sandbox?

Options:

A.

GET

B.

POST

C.

STOR

D.

PUT

Buy Now
Questions 27

Which fields are used to determine asset priority, when priority is assigned through an asset and identity lookup?

Options:

A.

dest, src, or dvc

B.

dest, src, or tag

C.

user or src_user

D.

dest_user or src_user

Buy Now
Questions 28

A SOC ' s Incident Response Standard Operating Procedure (SOP) calls for any phishing emails containing files to be detonated in Splunk Attack Analyzer for evaluation. Which of the following can an engineer implement to gain efficiency through automation?

Options:

A.

Automatically assign phishing-tagged findings to analysts to begin manual collection.

B.

Automatically send an email notification for all findings containing the phishing tag.

C.

Use a SOAR playbook to handle the Splunk Attack Analyzer submission and data-collection steps and make the information available to an assigned analyst.

D.

Use a SOAR playbook to submit the email to PhishTank and have it perform the Splunk Attack Analyzer submission.

Buy Now
Questions 29

What is the primary purpose of data indexing in Splunk?

Options:

A.

To ensure data normalization

B.

To store raw data and enable fast search capabilities

C.

To secure data from unauthorized access

D.

To visualize data using dashboards

Buy Now
Questions 30

Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
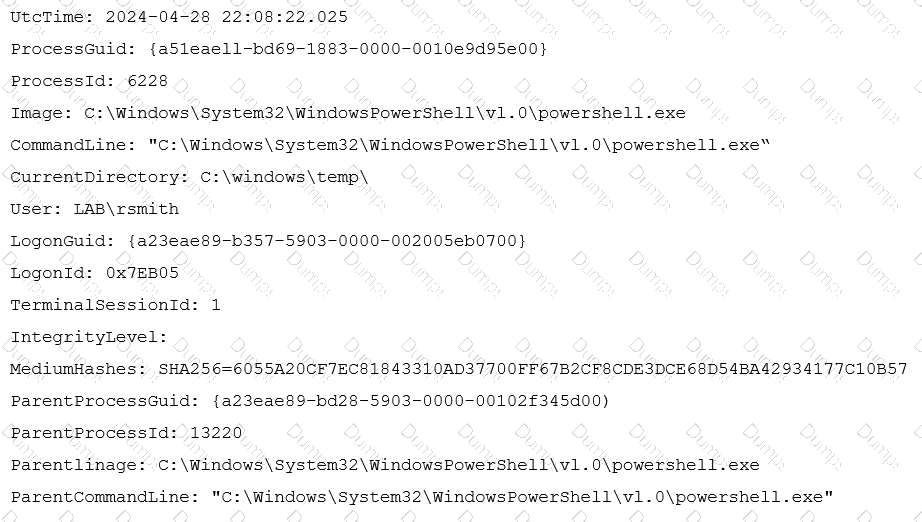
SPLK-5002 Question 30

Options:

A.

EventCode=1

B.

EventCode=4

C.

EventCode=3

D.

EventCode=2

Buy Now
Questions 31

When should a detection be reviewed or retuned after deployment?

Options:

A.

Every 30 days.

B.

Only if it has generated a large amount of false positives.

C.

As defined by the established detection lifecycle.

D.

Only if it hasn ' t generated a finding after several weeks.

Buy Now
Exam Code: SPLK-5002
Exam Name: Splunk Certified Cybersecurity Defense Engineer
Last Update: Oct 8, 2026
Questions: 105

PDF + Testing Engine

$134.99

Testing Engine

$99.99

PDF (Q&A)

$84.99