Terraform-Associate-004 HashiCorp Certified: Terraform Associate (004) (HCTA0-004) Questions and Answers
A module block used in your configuration is shown in the exhibit. You have been asked to update the version of this module from 4.2.1 to 5.0.0.
Exhibit:
module " compute " {
source = " Azure/compute/azurerm "
version = " 4.2.1 "
}
Which two steps must you take to accomplish this?
You are writing a child Terraform module that provisions an AWS instance. You want to reference the IP address returned by the child module in the root configuration. You name the instance resource " main ' .
Which of these is the correct way to define the output value?
If you update the version constraint in your Terraform configuration, Terraform will update your lock file the next time you run terraform Init.
Which type of block fetches or computes information for use elsewhere in a Terraform configuration?
What kind of configuration block will manage an infrastructure object with settings specified within the block?
Which of these ate secure options for storing secrets for connecting to a Terraform remote backend? Choose two correct answers.
Your team uses HCP Terraform to manage infrastructure. You need to make a change to an infrastructure stack running in a public cloud. Which pattern follows Infrastructure as Code best practices for making the change?
Setting the TF_LOG environment variable to DEBUG causes debug messages to be logged into stdout.
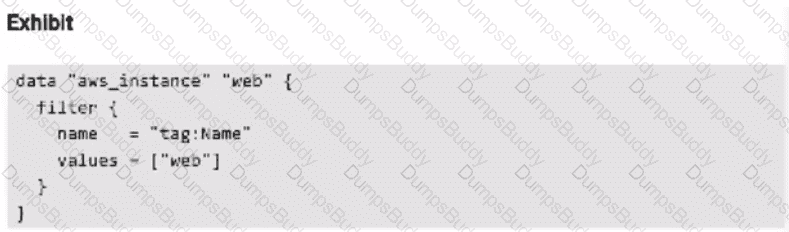
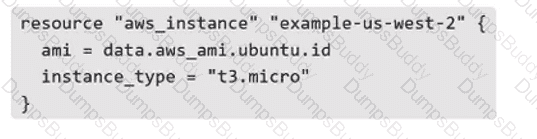
The Terraform configuration shown in the Exhibit space on this page v/ill create a new AWS instance.
Which parameters does the import block require? (Pick the 2 correct responses below.)
When using multiple configuration of the same Terraform provider, what meta-argument must you include in any non-default provider configurations?
You have a simple Terraform configuration containing one virtual machine (VM) in a cloud provider. You run terraform apply and the VM is created successfully.
What will happen if you delete the VM using the cloud provider console, then run terraform apply again without changing any Terraform code?
When you run terraform apply -refresh-only, which of the following is not consulted by Terraform to update the state file?
You just scaled your VM infrastructure and realize you set the count variable to the wrong value. You correct the value and save your change. What must you do next to make your infrastructure match your configuration?
Exhibit:
Error: Saved plan is stale
The given plan file can no longer be applied because the state was changed by another operation after the plan was created.
You have a saved execution plan containing desired changes for infrastructure managed by Terraform. After running terraform apply my.tfplan, you receive the error shown. How can you apply the desired changes? (Pick the 2 correct responses below.)
Changing the Terraform backend from the default " local " backend to a different one after performing your first terrafom apply is:
A module block is shown in the Exhibit space of this page. When you use a module block to reference a module from the Terraform Registry such as the one in the example, how do you specify version 1.0.0 of the module?
What Terraform command always causes a state file to be updated with changes that might have been made outside of Terraform?
What feature stops multiple users from operating on the Terraform state at the same time?
Running terraform fmt without any flags in a directory with Terraform configuration files will check the formatting of those files, but will never change their contents.
What value does the Terraform Cloud private registry provide over the public Terraform Module Registry?
A resource block is shown in the Exhibit space of this page. How would you reference the name value of the second instance of this resource?
Which option cannot be used to keep secrets out of Terraform configuration files?
Exhibit:
resource " aws_instance " " example " {
ami = " ami-0a123456789abcdef "
instance_type = " t3.micro "
}
You are updating a child module with the resource block shown in the exhibit. The public_ip attribute of the resource needs to be accessible to the parent module. How do you meet this requirement?
You can access state stored with the local backend by using terraform_remote_state data source.
You are responsible for a set of infrastructure that is managed by two workspaces: example-network and example-compute. The example-compute workspace uses data from output values configured in the example-network workspace and must be deployed afterward. Currently, this is a manual process:
An operator deploys changes to the example-network workspace.
They manually copy the output values from the example-network workspace to input variables configured for the example-compute workspace.
They deploy the example-compute workspace.
Which HCP Terraform features can you use to automate this process?
Pick the two correct responses below.
Your Terraform configuration declares a variable. You want to enforce that its value meets your specific requirements, and you want to block the Terraform operation if it does not. What should you add to your configuration?
Your DevOps team is currently using the local backend for your Terraform configuration. You would like to move to a remote backend to store the state file in a central location. Which of the following backends would not work?
You want to use API tokens and other secrets within your team ' s Terraform workspaces. Where does HashiCorp recommend you store these sensitive values?
(Pick 3 correct responses)
You have just developed a new Terraform configuration for two virtual machines with a cloud provider. You would like to create the infrastructure for the first time.
Which Terraform command should you runfirst?
Which of the following isnotan advantage of using Infrastructure as Code (IaC) operations?
When a check block’s assertion fails, Terraform blocks the current operation from executing.
Which of the following does terraform apply change after you approve the execution plan? (Choose two.)
Which of the following can you do with terraform plan?
Pick the two correct responses below.
You ' re writing a Terraform configuration that needs to read input from a local file called id_rsa.pub. Which built-in Terraform function can you use to import the file ' s contents as a string?
terraform apply will fail if you have not run terraform plan first to update the plan output.
Why is it considered an anti-pattern to store your Terraform state in version control?
Exhibit:
provider " aws " { region = " us-east-1 " }
provider " aws " { region = " us-west-2 " }
You need to deploy resources into two different AWS regions in the same Terraform configuration using the provider blocks shown in the exhibit. What do you need to add to the provider configuration to deploy a resource to the us-west-2 AWS region?
What is the Terraform style convention for indenting a nesting level compared to the one above it?
Exhibit:
Root module configuration:
output " vnet_id " {
value = module.my_network.vnet_id
}
Error:
Error: Reference to undeclared output value
on main.tf line 12, in output " vnet_id " :
12: value = module.my_network.vnet_id
You are using a networking module in your Terraform configuration with the name my_network. Your root module includes the configuration shown. When you run terraform validate, you get the error shown. Which option would successfully retrieve this value from your networking module?
Exhibit:
resource " azurerm_linux_web_app " " app " {
name = " example-app "
resource_group_name = azurerm_resource_group.rg.name
location = azurerm_resource_group.rg.location
service_plan_id = azurerm_service_plan.plan.id
identity {
type = " UserAssigned "
identity_ids = [azurerm_user_assigned_identity.app.id]
}
}
resource " azurerm_role_assignment " " kv_access " {
scope = azurerm_key_vault.kv.id
role_definition_name = " Key Vault Secrets User "
principal_id = azurerm_user_assigned_identity.app.principal_id
}
Two resource blocks are shown: azurerm_linux_web_app and azurerm_role_assignment. When provisioned, the web app will use the role assignment during creation, so the role assignment must be created first. How do you ensure the azurerm_role_assignment resource is created first?
You are tasked with making a change to an infrastructure stack running in a public cloud using HCP Terraform/Terraform Cloud. Which pattern follows IaC best practices?
You want to create a string that is a combination of a generated random_id and a variable, and reuse that string several times in your configuration.
What is the simplest correct way to implement this without repeating the random_id and variable?
You can reference a resource created with for_each using a Splat ( *) expression.
Where does HashiCorp recommend you store API tokens and other secrets within your team’s Terraform workspaces?
Pick the three correct responses below.
It is __________ to change the Terraform backend from the default local backend to a different backend after performing your first terraform apply.
Which of these actions will prevent two Terraform runs from changing the same state file at the same time?
terraform validate confirms that your infrastructure matches the Terraform state file.
How can a ticket-based system slow down infrastructure provisioning and limit the ability to scale? Choose two correct answers.
While attempting to deploy resources into your cloud provider using Terraform, you begin to see some odd behavior and experience slow responses. In order to troubleshoot you decide to turn on Terraform debugging. Which environment variables must be configured to make Terraform ' s logging more verbose?
You can configure Terraform to log to a file using the TF_LOG environment variable.
What kind of configuration block will create an infrastructure object with settings specified within the block?
terraform apply is failing with the following error. What next step should you take to determine the root cause of the problem?
Error:
yaml
CopyEdit
Error loading state: AccessDenied: Access Denied
status code: 403, request id: 288766CE5CCA24A0, host id: web.example.com
Which method for sharing Terraform configurations fulfills the following criteria:
1. Keeps the configurations confidential within your organization
2. Support Terraform’s semantic version constrains
3. Provides a browsable directory
You have never used Terraform before and would like to test it out using a shared team account for a cloud provider. The shared team account already contains 15 virtual machines (VM). You develop a Terraform configuration containing one VM. perform terraform apply, and see that your VM was created successfully. What should you do to delete the newly-created VM with Terraform?
Which of the following locations can Terraform use as aprivate sourcefor modules?(Pick 2 correct responses)
Which of the following is true about terraform apply?(Pick 2 correct responses)
A resource block is shown in the Exhibit section of this page. How would you reference the attribute name of this resource in HCL?
Your team is using version 3.1.4 of a module from the public Terraform Registry, and they are worried about possible breaking changes in future versions of the module. Which version argument should you add to the module block to prevent newer versions from being used?
What functionality do providers offer in Terraform? (Pick the 3 correct responses below.)
Multiple team members are collaborating on infrastructure using Terraform and want to format the* Terraform code following standard Terraform-style convention.
How should they ensure the code satisfies conventions?
When you use a remote backend that needs authentication, HashiCorp recommends that you:
Which of the following can you do with terraform plan? (Pick 2 correct responses)
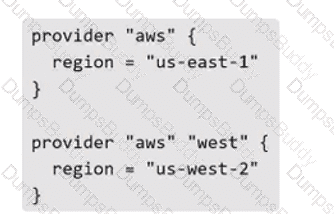
Exhibit.
You need to deploy resources into two different regions in the same Terraform configuration. To do this, you declare multiple provider configurations as shown in the Exhibit space on this page.
What meta-argument do you need to configure in a resource block to deploy the resource to the us-west-2 AWS region?
You have a list of numbers that represents the number of free CPU cores on each virtual cluster:
numcpus = [ 18, 3, 7, 11, 2 ]
What Terraform function could you use to select the largest number from the list?
You have set the TF_LOG_PATH environment variable for Terraform, and you would like to ensure the logs contain all debug-level messages and verbose process logs.
Which action should you take?
You need to deploy resources into two different regions in the same Terraform configuration using the block shown in the exhibit below.
What do you need to add to the provider configuration to deploy the resource to the us-west-2 AWS region?
Options:
Which of these statements about HCP Terraform/Terraform Cloud workspaces is false?
Which type of information does the Terraform Registry provide about the modules it hosts?
What information does the public Terraform Module Registry automatically expose about published modules?
A data source is shown in the exhibit below.
How do you reference the id attribute of this data source?
}
}
PDF + Testing Engine
Testing Engine
PDF (Q&A)