NSE7_SOC_AR-7.6 Fortinet NSE 7 - Security Operations 7.6 Architect Questions and Answers
You are using FortiSIEM analytics to reference the configuration management database (CMDB) event type categories with the following requirements:
Attribute: Event Type
Value: Group: Logon Success
Which operator must you use for the analytics search? Choose one answer.
Which two statements accurately describe the process to create a new rule from a search using FortiSIEM analytics? Choose two answers.
You suspect your organization has been a victim of numerous incidents carried out by the same threat actor. Which option allows you to group the incidents and track them? Choose one answer.
Refer to the exhibits.
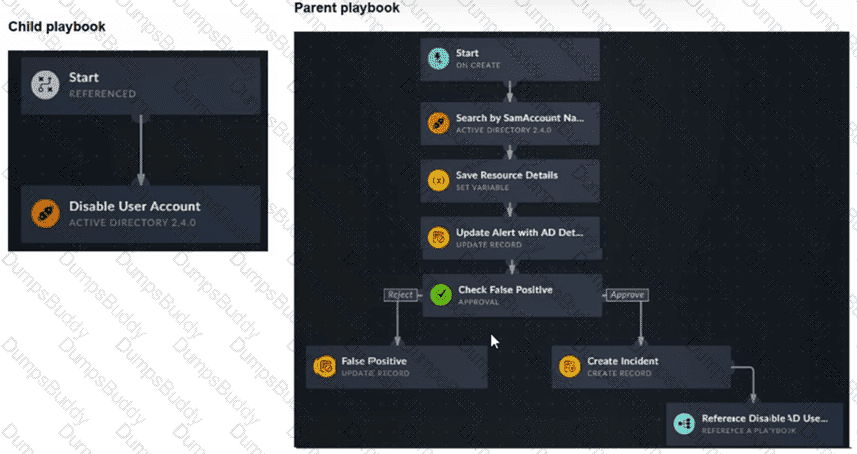
You have a playbook that, depending on whether an analyst deems the alert to be a true positive, could reference a child playbook. You need to pass variables from the parent playbook to the child playbook.
Place the steps needed to accomplish this in the correct order.
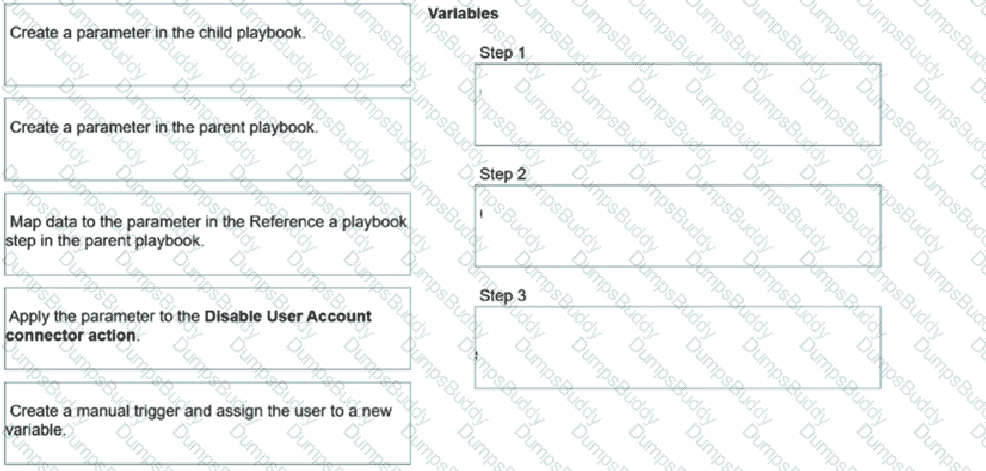
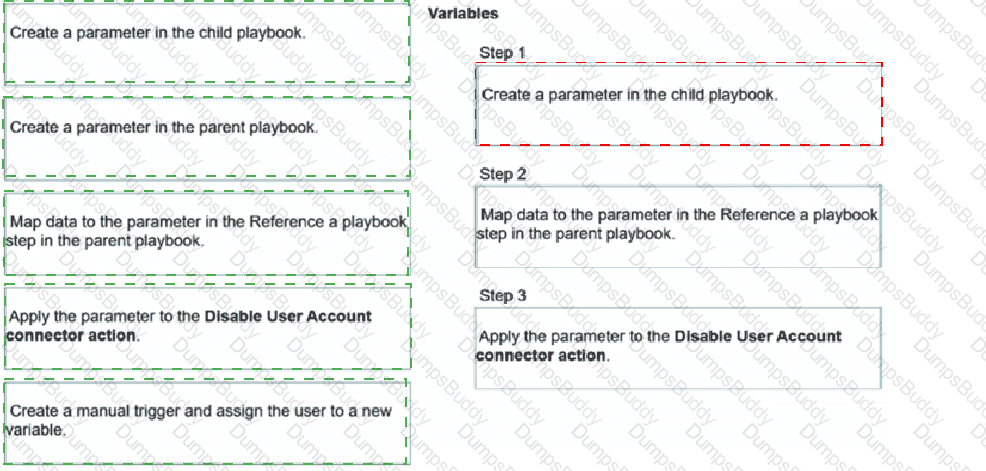
Refer to the exhibit.
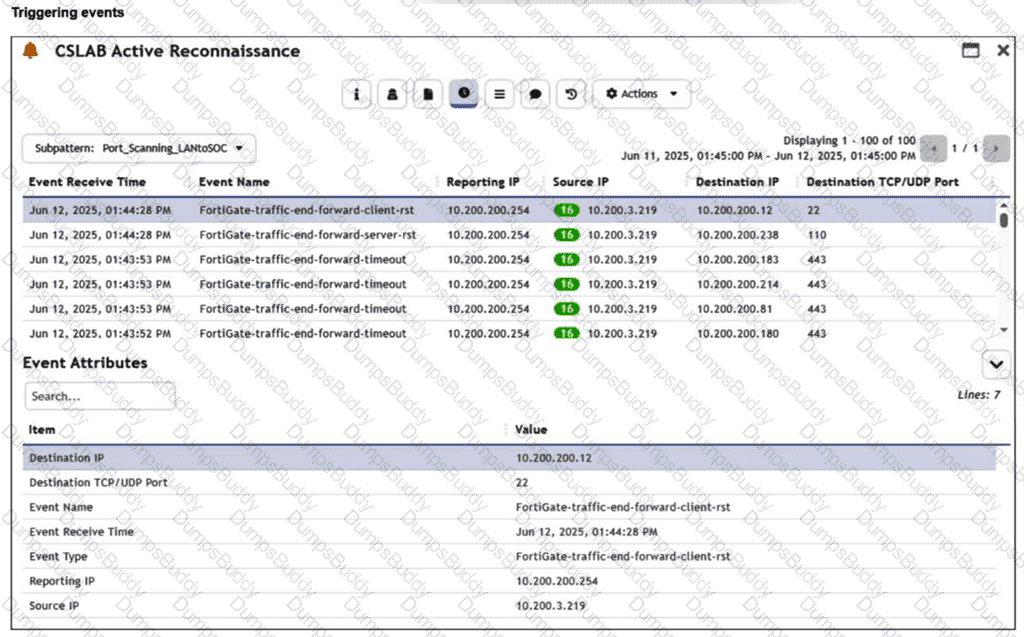
You are reviewing the Triggering Events page for a FortiSIEM incident. You want to remove the Reporting IP column because you have only one firewall in the topology. How do you accomplish this? (Choose one answer)
Which three factors does the FortiSIEM rules engine use to determine the count when it evaluates the aggregate condition COUNT (Matched Events) on a specific subpattern? (Choose three answers)
You want to trigger an incident when multiple failed logins from the same host are followed by a successful login on that same host within 15 minutes. The rule must correlate all events by source IP address and user to ensure they belong to the same login sequence. Which three configurations achieve this goal? Choose three answers.
You configured a new module named Users. Next, you want to configure a playbook that creates users from ingested data. When new records are created, you want to ensure that duplicate users do not overwrite existing user records and their fields. However, you also want the playbook to continue running even if duplicates are encountered so that any non-duplicate records are still created. Which two actions fulfill the requirements? Choose two answers.
Refer to the exhibits.
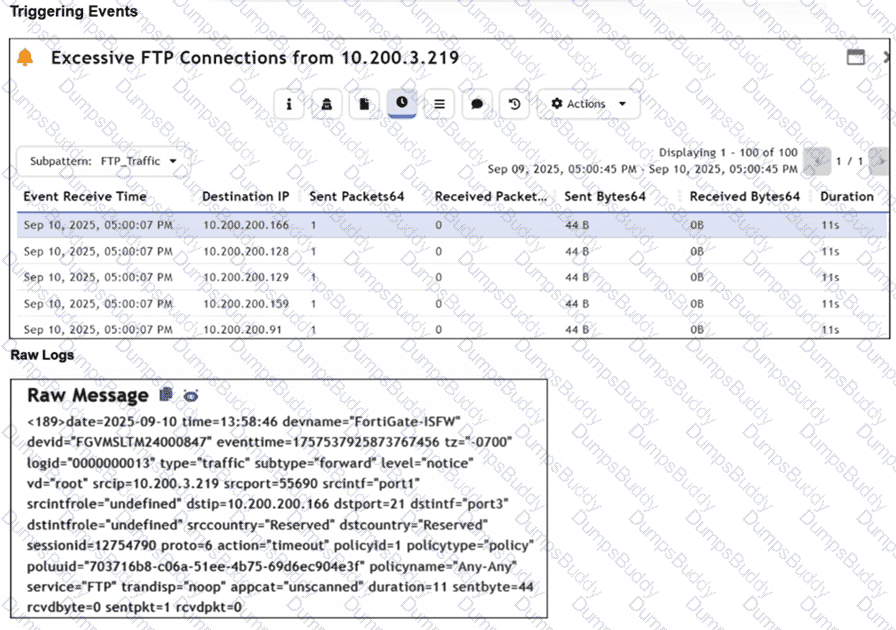
Assume that the traffic flows are identical, except for the destination IP address. There is only one FortiGate in network address translation (NAT) mode in this environment.
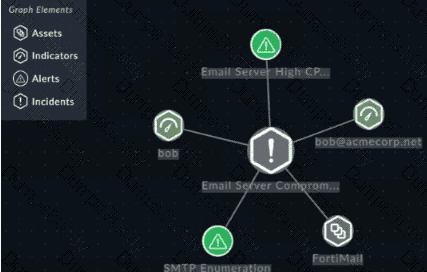
Based on the exhibits, which two conclusions can you make about this FortiSIEM incident? (Choose two answers)
Refer to the exhibits.
What can you conclude from analyzing the data using the threat hunting module?
You created a war room and want to run a connector action to look up the reputation of a domain. Then, you need to save the output for your team to review. However, there is a lot of output, and you want to limit the amount of information attached to the war room. How do you accomplish this? Choose one answer.
Refer to the exhibit.
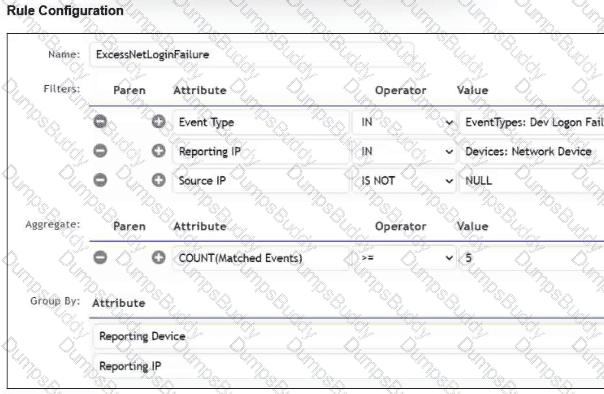
You created a subpattern to detect at least five failed login attempts from any single user and source IP address to the same network device. However, it is creating more incidents than you had anticipated.
What are the two mistakes in the incident subpattern rule configuration? (Choose two.)
Exhibit: FortiSIEM Rule Configuration
FortiSIEM failed login rule configuration
You are investigating an open incident and want to add records from the Tickets module, a custom module, to the visual correlation widget. Assume there are already linked ticket records to the incident.
How do you accomplish this? Choose one answer.
Exhibit:
Which observation about this FortiAnalyzer Fabric deployment architecture is true?
A very long FortiSOAR playbook failed at step 30 because of an intermittent networking issue, which has now been resolved. You want to finish executing the playbook without repeating earlier steps or losing prior context. Which action should you take? Choose one answer.
When configuring a FortiAnalyzer to act as a collector device, which two steps must you perform? (Choose two.)
Which two ways can you create an incident on FortiAnalyzer? (Choose two answers)
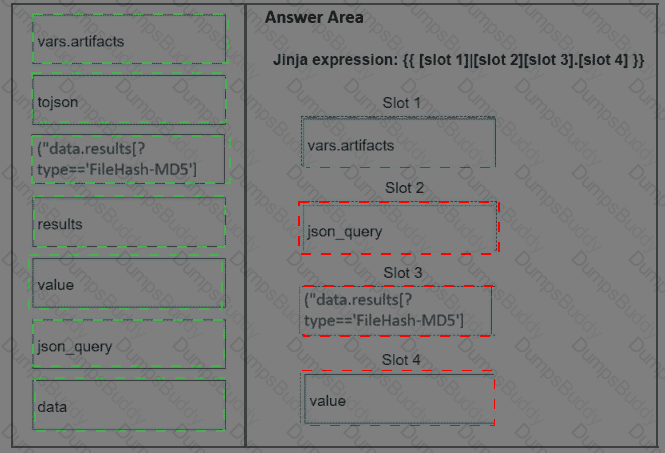
Refer to the exhibit.
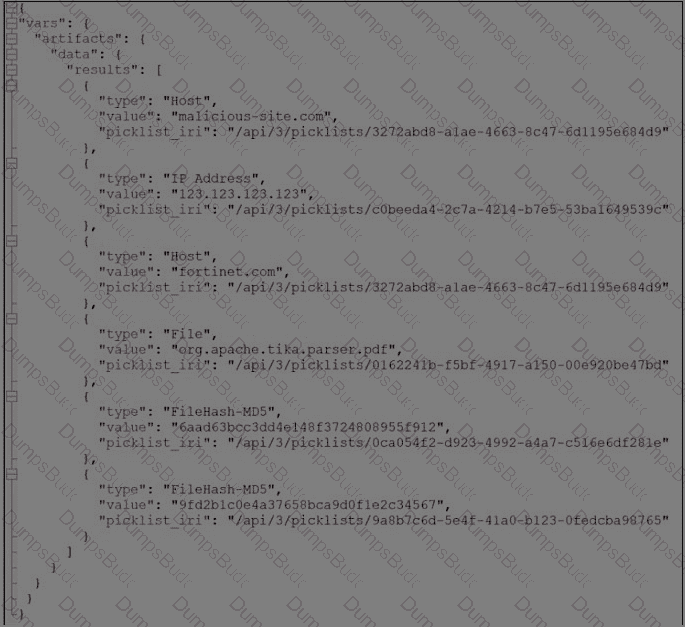
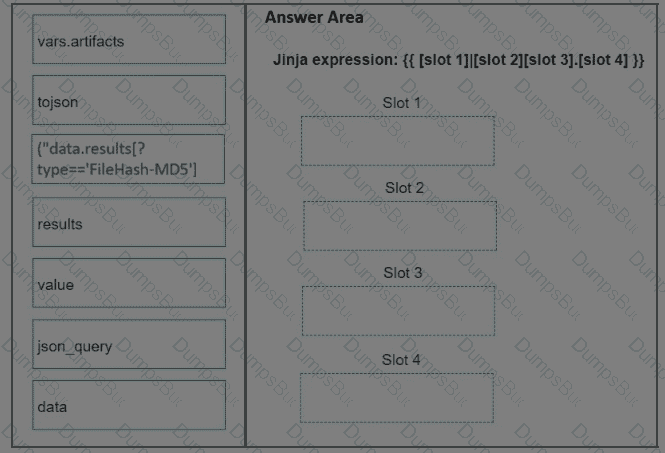
What is the correct Jinja expression to filter the results to show only the MD5 hash values?
{{ [slot 1]|[slot 2] [slot 3].[slot 4] }}
Select the jinja expression in the left column, hold and drag it to a blank position on the right. Place the four correct steps in order, placing the first
step in the first slot. Once you place an expression, you can move it again if you want to change your answer before moving to the next question. You
need to drop four jinja expressions in the work area.
Select and drag the screen divider to change the viewable area of the source and work areas.
You are trying to create a playbook that uses source data from ingestion to populate the description field of a task. You successfully saved the source data to a variable called ingestion_data. Now, you must parse the results and extract a list of indicators. Which Jinja expression can accomplish this task? Choose one answer.
You want to automate a workflow on FortiSOAR so that whenever an incident is moved to the Aftermath phase, it is automatically set to status Resolved and assigned to a purple team specialist as incident lead to write an incident report. In addition, a manual task, assigned to the same specialist, will be created so they are aware of the pending work. Which three steps will accomplish this task? Choose three answers.
Which of the following are critical when analyzing and managing events and incidents in a SOC? (Choose two answers)
Refer to the exhibit.
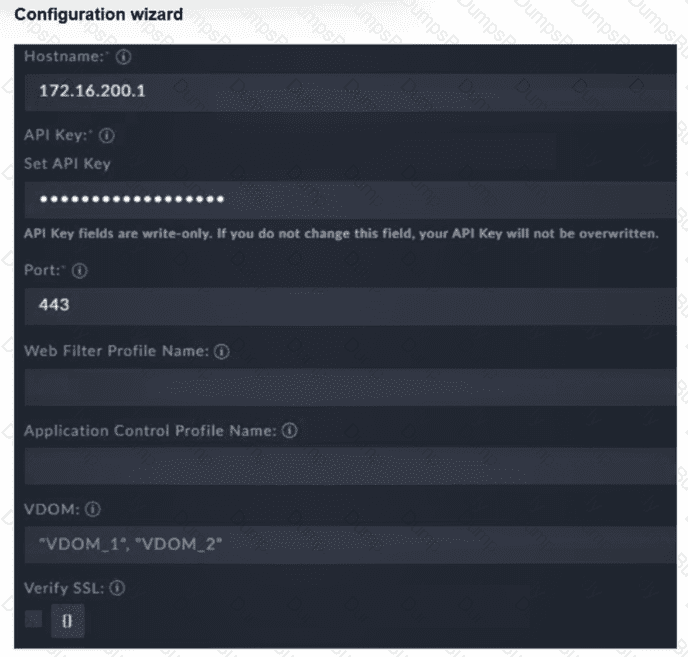
You must configure the FortiGate connector to allow FortiSOAR to perform actions on a firewall. However, the connection fails. Which two configurations are required? (Choose two answers)
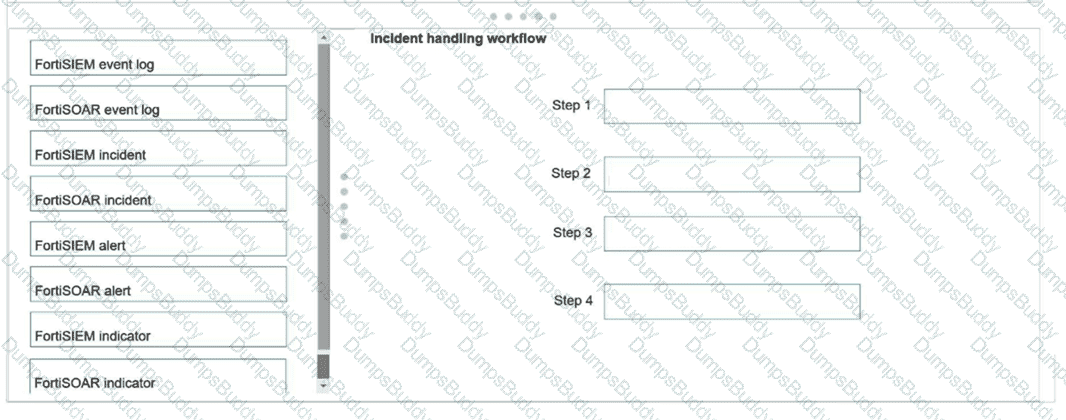
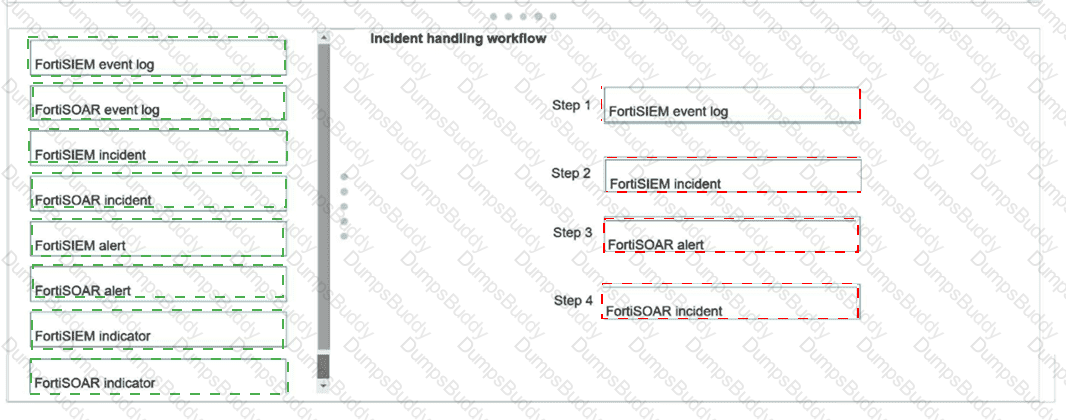
Using the default data ingestion wizard in FortiSOAR, place the incident handling workflow from FortiSIEM to FortiSOAR in the correct sequence. Select each workflow component in the left column, hold and drag it to a blank position in the column on the right. Place the four correct workflow components in order, placing the first step in the first position at the top of the column.
A large enterprise FortiSIEM deployment is experiencing delays in log correlation and analytics. Which architectural adjustment is most appropriate? Choose one answer.
PDF + Testing Engine
Testing Engine
PDF (Q&A)