NSE6_FSM_AN-7.4 Fortinet NSE 6 - FortiSIEM 7.4 Analyst Questions and Answers
Which two settings must you configure to allow FortiSIEM to apply tags to devices in FortiClient EMS? (Choose two.)
Refer to the exhibit.

An analyst is trying to identify an issue using an expression based on the Expression Builder settings shown in the exhibit; however, the error message shown in the exhibit indicates that the expression is invalid.
What is the correct syntax to create an expression that generates a total count of matched events?
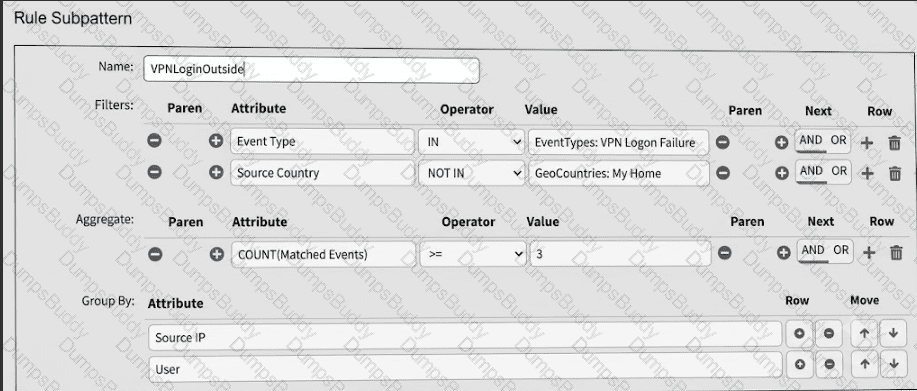
Refer to the exhibit.
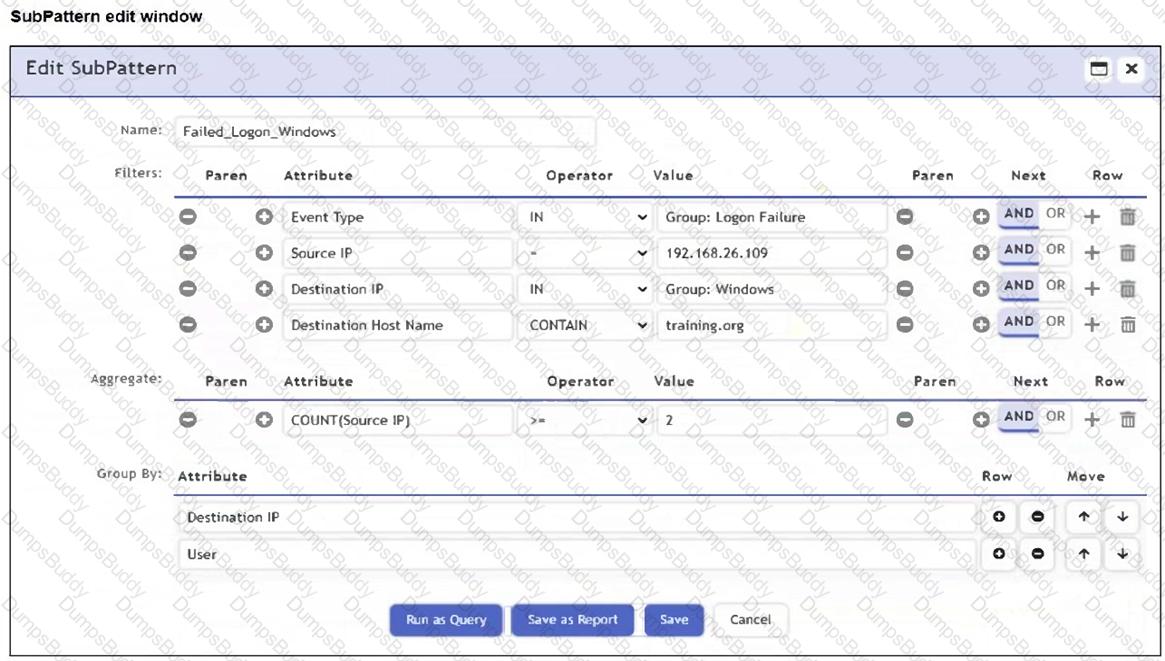
An analyst is troubleshooting the rule shown in the exhibit. It is not generating any incidents, but the filter parameters are generating events on the Analytics tab.
What is wrong with the rule conditions?
You need to model for predicting a target based on other fields in the dataset and then trigger an anomaly if the value does not match the prediction.
Which machine learning algorithm will build this type of model?
Refer to the exhibit.
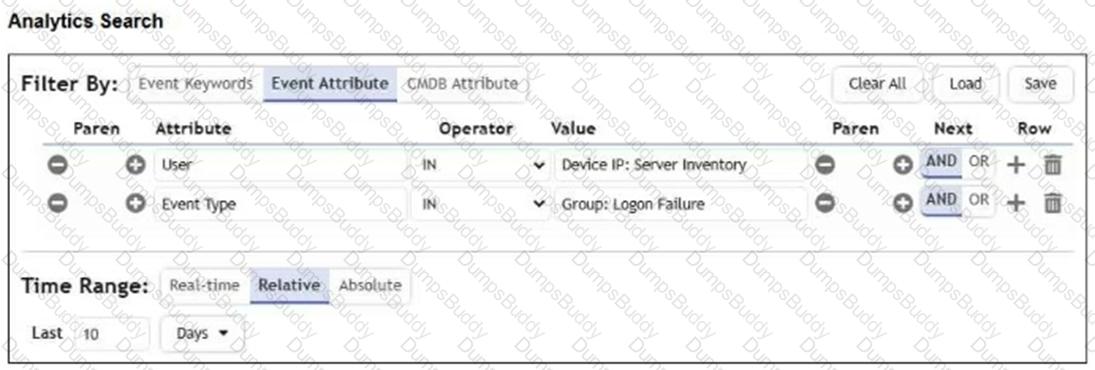
The analyst is troubleshooting the analytics query shown in the exhibit.
Why is this search not producing any results?
When configuring machine learning (ML), in which step can you modify how the model fits the training data set?
Refer to the exhibit.
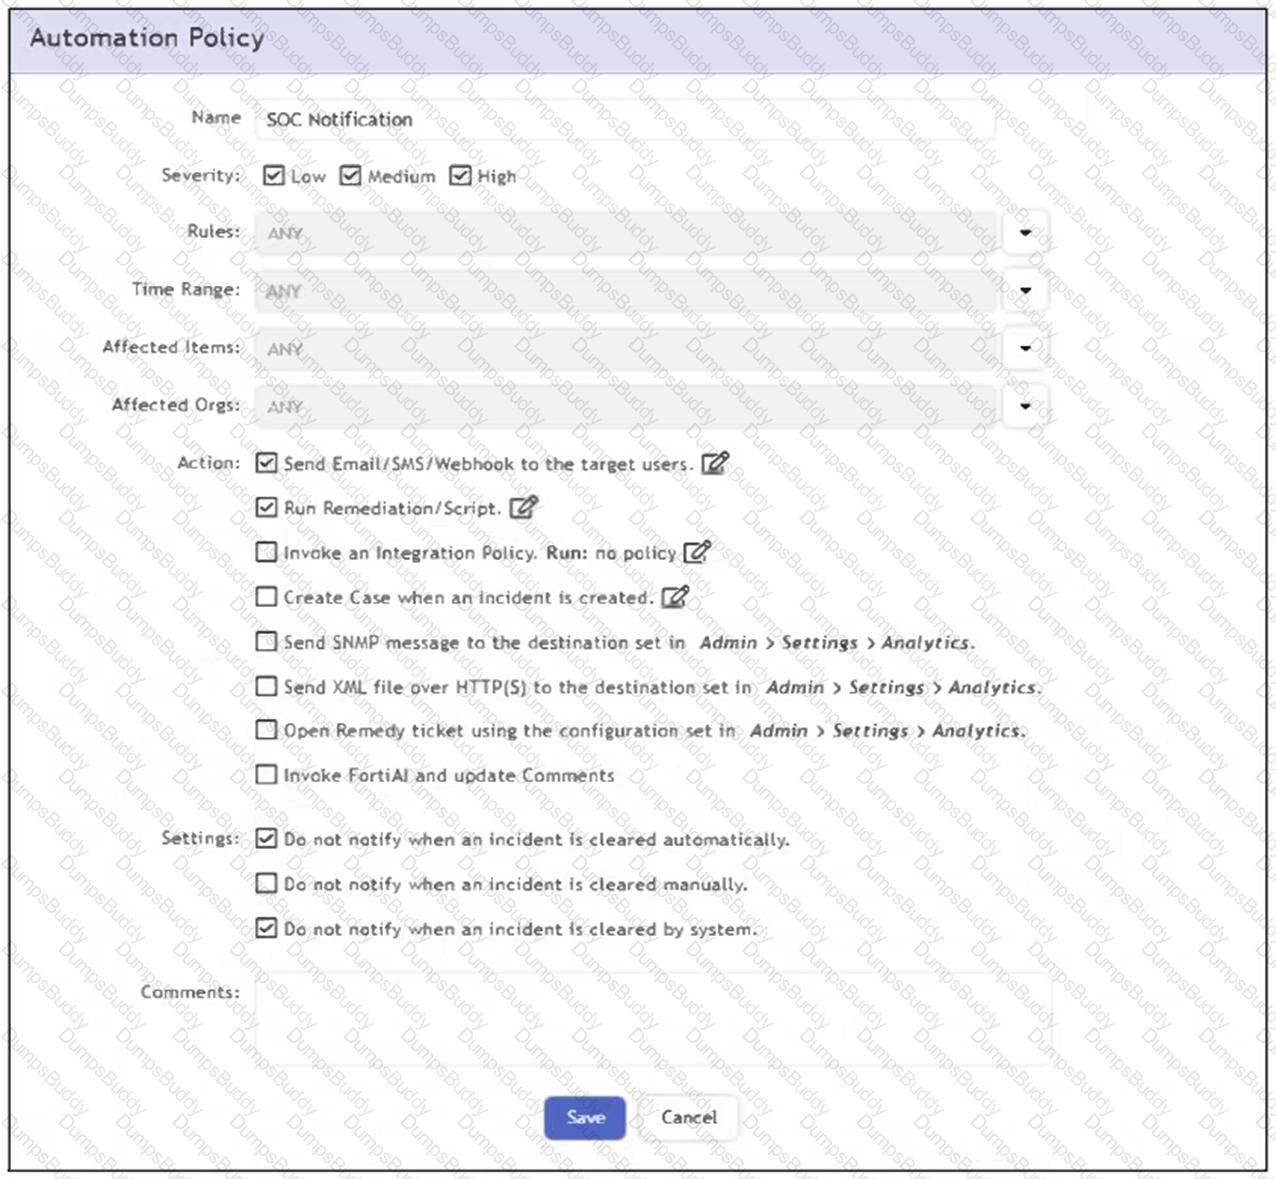
What happens when an analyst clears an incident generated by a rule containing the automation policy shown in the exhibit?
How does FortiSIEM update the incident table if a performance rule triggers repeatedly?
Refer to the exhibit.
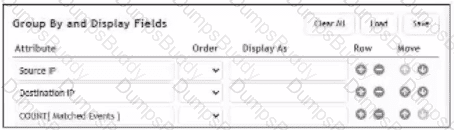
What will FortiSIEM display if you apply the Group By and Display Fields configuration to a list of allowed firewall connections?
Refer to the exhibit.

A FortiSIEM analyst is investigating an issue by examining events to two destination IP addresses. However, the analyst is not getting any results from the search.
Based on the selected filter shown in the exhibit, why is the search returning no results?
PDF + Testing Engine
Testing Engine
PDF (Q&A)