Halloween Sale Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: budy75

NSE6_EDR_AD-7.0 Fortinet NSE 6 - FortiEDR 7.0 Administrator Questions and Answers

Questions 4

What action does an on-premises reputation server take when it receives a hash request that is not found in its local database? (Choose one answer)

Options:

A.

Ignores them until manually updated

B.

Stores them locally and waits for endpoint input

C.

Requests the missing hashes from the cloud reputation service

D.

Automatically blocks applications with unknown hashes

Buy Now
Questions 5

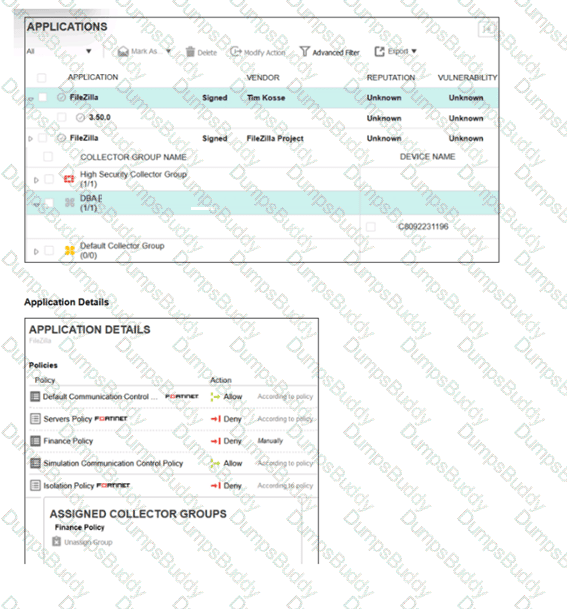
Refer to the exhibits.

NSE6_EDR_AD-7.0 Question 5

The application policy logs and application details are shown. Collector C8092231196 is a member of the Finance group. In this scenario, what must you do to block the FileZilla application? (Choose one answer)

Options:

A.

Assign the Simulation Communication Control Policy to the DBA group.

B.

Deny the application in the Finance policy.

C.

Assign the Finance policy to the DBA group.

D.

Assign the Finance policy to a broader collector group, such as the Default Collector Group.

Buy Now
Questions 6

A collector triggers a suspicious security incident that is initially flagged as potentially malicious. The environment is connected to the FortiEDR Cloud Service (FCS) for classification. How does FCS process the event for accurate classification? (Choose one answer)

Options:

A.

By data processing, comprehensive automated analysis, and comprehensive manual analysis

B.

By relying solely on the FortiGate firewall policies

C.

By comparing the event against only local signatures

D.

By correlating collector logs only

Buy Now
Questions 7

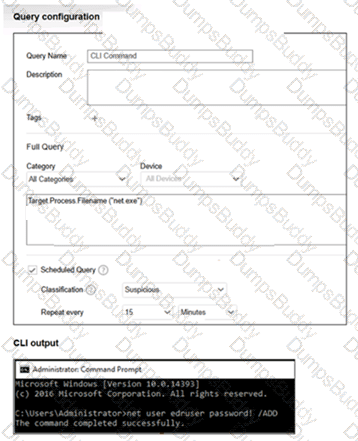
Refer to the exhibits.

NSE6_EDR_AD-7.0 Question 7

What happens when the net user command runs on an endpoint? (Choose one answer)

Options:

A.

It triggers an immediate endpoint alert.

B.

It blocks CLI commands by default.

C.

It triggers an incident when the query matches the target process (net.exe).

D.

It triggers FortiEDR rules because the activity is not suspicious.

Buy Now
Questions 8

Within the FortiEDR architecture, which component needs JumpBox capabilities to enable authenticated and controlled communication with FortiAnalyzer? (Choose one answer)

Options:

A.

Core

B.

Central manager

C.

Aggregator

D.

Reputation Server

Buy Now
Questions 9

Which two Python commands are supported when using FortiEDR Connect to directly access a protected device shell? (Choose two answers)

Options:

A.

%upload_file

B.

%ipconfig_all

C.

%psexec

D.

%timestamp

Buy Now
Questions 10

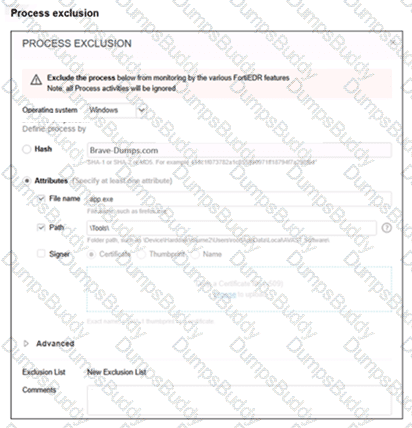
Refer to the exhibit:

NSE6_EDR_AD-7.0 Question 10

You configured an execution prevention exclusion with both File Name = app.exe and Path = C:\Tools. What will FortiEDR do? (Choose one answer)

Options:

A.

Exclude only signed versions of app.exe.

B.

Exclude only app.exe when it is running from C:\Tools.

C.

Exclude app.exe whenever it appears.

D.

Exclude all files in C:\Tools.

Buy Now
Exam Code: NSE6_EDR_AD-7.0
Exam Name: Fortinet NSE 6 - FortiEDR 7.0 Administrator
Last Update: Nov 2, 2026
Questions: 35

PDF + Testing Engine

$134.99

Testing Engine

$99.99

PDF (Q&A)

$84.99