CRISC Certified in Risk and Information Systems Control Questions and Answers
Which of the following is the MOST effective way to reduce potential losses due to ongoing expense fraud?
An organization is implementing internet of Things (loT) technology to control temperature and lighting in its headquarters. Which of the following should be of GREATEST concern?
Which of the following is MOST important for developing effective key risk indicators (KRIs)?
A new software package that could help mitigate risk in an organization has become available. Which of the following is the risk practitioner’s BEST course of action?
Which of the following is the PRIMARY consideration when determining the impact to an organization after the discovery of malware on an endpoint device?
A vendor ' s planned maintenance schedule will cause a critical application to temporarily lose failover capabilities. Of the following, who should approve this proposed schedule?
Which of the following would be MOST helpful to a risk practitioner when preparing a summary of current IT risk for senior management review?
Which of the following provides the MOST useful information to trace the impact of aggregated risk across an organization ' s technical environment?
Which key performance indicator (KPI) BEST measures the effectiveness of an organization ' s disaster recovery program?
Which of the following is the MOST important reason to communicate risk assessments to senior management?
Which of the following is the BEST way for a risk practitioner to help management prioritize risk response?
From a business perspective, which of the following is the MOST important objective of a disaster recovery test?
In which of the following system development life cycle (SDLC) phases should controls be incorporated into system specifications?
Which of the following would BEST facilitate the implementation of data classification requirements?
Which of the following would be MOST helpful when communicating roles associated with the IT risk management process?
Which of the following is the MOST important objective of embedding risk management practices into the initiation phase of the project management life cycle?
Changes in which of the following would MOST likely cause a risk practitioner to adjust the risk impact rating in the risk register?
Which of the following would BEST help to ensure that suspicious network activity is identified?
When developing a new risk register, a risk practitioner should focus on which of the following risk management activities?
The BEST key performance indicator (KPI) to measure the effectiveness of a vulnerability remediation program is the number of:
Which of the following is MOST important to ensure when reviewing an organization ' s risk register?
Which of the following would be a risk practitioner’s GREATEST concern related to the monitoring of key risk indicators (KRIs)?
What is the PRIMARY reason to periodically review key performance indicators (KPIs)?
The GREATEST benefit of introducing continuous monitoring to an IT control environment is that it:
Which of the following provides the MOST useful information for developing key risk indicators (KRIs)?
Which of the following is the MOST important objective of regularly presenting the project risk register to the project steering committee?
A new international data privacy regulation requires personal data to be
disposed after the specified retention period, which is different from the local
regulatory requirement. Which of the following is the risk practitioner ' s
BEST course of action?
Which of the following BEST enables a risk practitioner to focus on risk factors that could potentially affect the results of an IT initiative?
Which of the following is MOST important for the organization to consider before implementing a new in-house developed artificial intelligence (Al) solution?
The design of procedures to prevent fraudulent transactions within an enterprise resource planning (ERP) system should be based on:
From a governance perspective, which of the following is MOST important to ensure when risk management policies are being updated to facilitate the pursuit of new opportunities?
In order to determining a risk is under-controlled the risk practitioner will need to
After mapping generic risk scenarios to organizational security policies, the NEXT course of action should be to:
Which of the following BEST enables a risk practitioner to identify the consequences of losing critical resources due to a disaster?
Which of the following is MOST important when developing key performance indicators (KPIs)?
Which of the following is MOST important when identifying an organization ' s risk exposure associated with Internet of Things (loT) devices?
Which of the following would be the GREATEST concern for an IT risk practitioner when an employees.....
Which of the following BEST enables an organization to address risk associated with technical complexity?
Which of the following is the FIRST step in managing the security risk associated with wearable technology in the workplace?
Which of the following should be the PRIMARY objective of a risk awareness training program?
Who is ULTIMATELY accountable for the confidentiality of data in the event of a data breach within a Software as a Service (SaaS) environment?
Which of the following should be of GREATEST concern when reviewing the results of an independent control assessment to determine the effectiveness of a vendor ' s control environment?
Which of the following would provide the MOST helpful input to develop risk scenarios associated with hosting an organization ' s key IT applications in a cloud environment?
Which of the following should be the PRIMARY driver for an organization on a multi-year cloud implementation to publish a cloud security policy?
An organization is subject to a new regulation that requires nearly real-time recovery of its services following a disruption. Which of the following is the BEST way to manage the risk in this situation?
Which of the following is the PRIMARY purpose of conducting risk and control self-assessments?
Which of the following tools is MOST effective in identifying trends in the IT risk profile?
Establishing and organizational code of conduct is an example of which type of control?
The PRIMARY reason for communicating risk assessment results to data owners is to enable the:
Which of the following is MOST important to compare against the corporate risk profile?
A newly enacted information privacy law significantly increases financial penalties for breaches of personally identifiable information (Pll). Which of the following will MOST likely outcome for an organization affected by the new law?
Warning banners on login screens for laptops provided by an organization to its employees are an example of which type of control?
How does the identification of risk scenarios contribute to effective IT risk management?
A risk practitioner observed Vial a high number of pokey exceptions were approved by senior management. Which of the following is the risk practitioner’s BEST course of action to determine root cause?
An organization is participating in an industry benchmarking study that involves providing customer transaction records for analysis Which of the following is the MOST important control to ensure the privacy of customer information?
The MOST essential content to include in an IT risk awareness program is how to:
An IT department has organized training sessions to improve user awareness of organizational information security policies. Which of the following is the BEST key performance indicator (KPI) to reflect effectiveness of the training?
Which of the following is a risk practitioner ' s BEST recommendation regarding disaster recovery management (DRM) for Software as a Service (SaaS) providers?
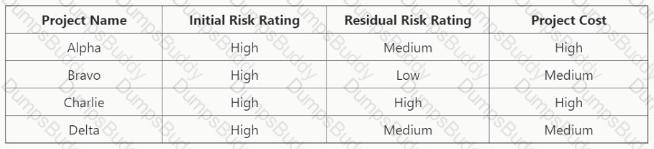
An organization has four different projects competing for funding to reduce overall IT risk. Which project should management defer?
Which of the following provides the MOST useful input to the development of realistic risk scenarios?
In the three lines of defense model, a PRIMARY objective of the second line is to:
When collecting information to identify IT-related risk, a risk practitioner should FIRST focus on IT:
Which of the following is MOST helpful to understand the consequences of an IT risk event?
Which of the following enterprise architecture (EA) controls BEST mitigates the risk of increasingly complex systems becoming compromised by unauthorized network access?
Which of the following BEST indicates the effectiveness of anti-malware software?
Which of the following would BEST enable mitigation of newly identified risk factors related to internet of Things (loT)?
Which of the following is the MOST efficient method for monitoring control effectiveness?
A risk practitioner is developing a set of bottom-up IT risk scenarios. The MOST important time to involve business stakeholders is when:
Which of the following is MOST important to ensure risk management practices are effective at all levels within the organization?
An organization moved its payroll system to a Software as a Service (SaaS) application. A new data privacy regulation stipulates that data can only be processed within the countrywhere it is collected. Which of the following should be done FIRST when addressing this situation?
Which of the following will MOST improve stakeholders ' understanding of the effect of a potential threat?
Which of the following is a PRIMARY reason for considering existing controls during initial risk assessment?
Which of the following BEST helps to identify significant events that could impact an organization?
Vulnerability analysis
A risk assessment has been completed on an application and reported to the application owner. The report includes validated vulnerability findings that require mitigation. Which of the following should be the NEXT step?
Which of the following is the MOST relevant information to include in a risk management strategy?
Which of the following is the BEST course of action for a system administrator who suspects a colleague may be intentionally weakening a system ' s validation controls in order to pass through fraudulent transactions?
Which of the following is MOST important for an organization to consider when developing its IT strategy?
Which of the following is the MOST important data source for monitoring key risk indicators (KRIs)?
Which of the following is the MOST effective way to validate organizational awareness of cybersecurity risk?
Which of the following is the FIRST step in managing the risk associated with the leakage of confidential data?
Which of the following observations would be the GREATEST concern to a risk practitioner evaluating an organization ' s risk management practices?
An organization plans to provide specific cloud security training for the IT team to help manage risks associated with cloud technology. This response is considered risk:
An organization is developing a plan to address new information security risks emerging from business changes. Which of the following BEST enables stakeholders to make decisions impacting organizational strategy?
An organization has implemented a cloud-based backup solution to help prevent loss of transactional data from offices in an earthquake zone. This strategy demonstrates risk:
Which of the following is the MOST comprehensive resource for prioritizing the implementation of information systems controls?
Which of the following is MOST important to communicate to senior management during the initial implementation of a risk management program?
The MOST important consideration when selecting a control to mitigate an identified risk is whether:
An assessment of information security controls has identified ineffective controls. Which of the following should be the risk practitioner ' s FIRST course of action?
An organization is developing a risk awareness program for contractors and consultants. Which of the following is MOST important for the organization to keep confidential?
When classifying and prioritizing risk responses, the areas to address FIRST are those with:
Which risk response strategy could management apply to both positive and negative risk that has been identified?
The MOST essential content to include in an IT risk awareness program is how to:
Which of the following should be the MAIN consideration when validating an organization ' s risk appetite?
Which of the following would be the result of a significant increase in the motivation of a malicious threat actor?
Which of the following should be of GREATEST concern to a risk practitioner when determining the effectiveness of IT controls?
In which of the following scenarios would a risk practitioner be required to provide the MOST justification for a risk assessment?
An online payment processor would be severely impacted if the fraud detection system has an outage. Which of the following is the BEST way to address this risk?
A financial organization is considering a project to implement the use of blockchain technology. To help ensure the organization ' s management team can make informed decisions on the project, which of the following should the risk practitioner reassess?
Which of the following is the MOST important consideration when developing risk strategies?
An organization uses one centralized single sign-on (SSO) control to cover many applications. Which of the following is the BEST course of action when a new application is added to the environment after testing of the SSO control has been completed?
Which of the following is a risk practitioner ' s BEST course of action upon learning that a control under internal review may no longer be necessary?
Which of the following would BEST enable a risk practitioner to embed risk management within the organization?
An organization does not have a defined process to revoke IT access of staff members who have changed roles within the organization. Which of the following is the GREATEST concern associated with this deficiency?
During the control evaluation phase of a risk assessment, it is noted that multiple controls are ineffective. Which of the following should be the risk practitioner ' s FIRST course of action?
A risk action plan has been changed during the risk mitigation effort. Which of the following is MOST important for the risk practitioner to verify?
An organization is reviewing a contract for a Software as a Service (SaaS) sales application with a 99.9% uptime service level agreement (SLA). Which of the following BEST describes ownership of availability risk?
An organization striving to be on the leading edge in regard to risk monitoring would MOST likely implement:
What is the MOST important consideration when selecting key performance indicators (KPIs) for control monitoring?
Which of the following is the MOST important course of action to foster an ethical, risk-aware culture?
Which of the following should be an element of the risk appetite of an organization?
Management has noticed storage costs have increased exponentially over the last 10 years because most users do not delete their emails. Which of the following can BEST alleviate this issue while not sacrificing security?
A recently purchased IT application does not meet project requirements. Of the following, who is accountable for the potential impact?
As part of an aggressive new marketing strategy, an organization has decided to implement an emerging technology in a critical business system. Which of the following is the BEST course of action to address the risk associated with this new technology?
Which of the following is the MAIN benefit to an organization using key risk indicators (KRIs)?
External auditors have found that management has not effectively monitored key security technologies that support regulatory objectives. Which type of indicator would BEST enable the organization to identify and correct this situation?
The MAIN reason for prioritizing IT risk responses is to enable an organization to:
An organization retains footage from its data center security camera for 30 days when the policy requires 90-day retention The business owner challenges whether the situation is worth remediating Which of the following is the risk manager s BEST response '
Which of the following is the PRIMARY benefit of using a risk map with stakeholders?
Which of the following BEST enables an organization to address new risk associated with an Internet of Things (IoT) solution?
Which of the following BEST enables the selection of appropriate risk treatment in the event of a disaster?
Which of the following is the MOST appropriate key risk indicator (KRI) for backup media that is recycled monthly?
A risk practitioner has reviewed new international regulations and realizes the new regulations will affect the organization. Which of the following should be the risk practitioner ' s NEXT course of
action?
Which of the following is MOST important to review when determining whether a potential IT service provider’s control environment is effective?
During a data loss incident, which role in the RACI chart would be aligned to the risk practitioner?
Which of the following is the MOST important reason to communicate control effectiveness to senior management?
Which of the following is the BEST key performance indicator (KPI) to measure the effectiveness of a disaster recovery plan (DRP)?
Which of the following is the MOST important consideration when developing an organization ' s risk taxonomy?
A penetration testing team discovered an ineffectively designed access control. Who is responsible for ensuring the control design gap is remediated?
Which of the following is MOST helpful to review when identifying risk scenarios associated with the adoption of Internet of Things (loT) technology in an organization?
An organization recently configured a new business division Which of the following is MOST likely to be affected?
Which of the following should be done FIRST upon learning that the organization will be affected by a new regulation in its industry?
A risk practitioner is performing a risk assessment of recent external advancements in quantum computing. Which of the following would pose the GREATEST concern for the risk practitioner?
What should be the PRIMARY consideration related to data privacy protection when there are plans for a business initiative to make use of personal information?
An organization has decided to outsource a web application, and customer data will be stored in the vendor ' s public cloud. To protect customer data, it is MOST important to ensure which of the following?
Which of the following can be interpreted from a single data point on a risk heat map?
Which of the following should a risk practitioner recommend FIRST when an increasing trend of risk events and subsequent losses has been identified?
What is MOST important for the risk practitioner to understand when creating an initial IT risk register?
Legal and regulatory risk associated with business conducted over the Internet is driven by:
Which of the following is the PRIMARY concern for a risk practitioner regarding an organization ' s adoption of innovative big data analytics capabilities?
An organization ' s IT department wants to complete a proof of concept (POC) for a security tool. The project lead has asked for approval to use the production data for testing purposes as it will yield the best results. Which of the following is the risk practitioner ' s BEST recommendation?
When of the following is the MOST significant exposure when an application uses individual user accounts to access the underlying database?
Which of the following BEST enables the timely detection of changes in the security control environment?
Which of the following emerging technologies is frequently used for botnet distributed denial of service (DDoS) attacks?
Who is MOST important lo include in the assessment of existing IT risk scenarios?
Which of the following is a risk practitioner ' s BEST recommendation to help reduce IT risk associated with scheduling overruns when starting a new application development project?
One of an organization ' s key IT systems cannot be patched because the patches interfere with critical business application functionalities. Which of the following would be the risk practitioner ' s BEST recommendation?
Which of the following BEST enables a risk practitioner to plan a vulnerability assessment that aligns to detailed organizational requirements?
Which of the following is the MOST important criteria for selecting key risk indicators (KRIs)?
An organization is implementing robotic process automation (RPA) to streamline business processes. Given that implementation of this technology is expected to impact existing controls, which of the following is the risk practitioner ' s BEST course of action?
Which of the following would BEST help to address the risk associated with malicious outsiders modifying application data?
An IT project risk was identified during a monthly steering committee meeting. Which of the following roles is BEST positioned to approve the risk mitigation response?
A control owner has completed a year-long project To strengthen existing controls. It is MOST important for the risk practitioner to:
Recent changes in an organization ' s business strategy requires an application to increase its recovery point objective (RPO). Which of the following MUST be updated?
An organization is planning to implement a Zero Trust model. From a cybersecunty perspective, which of the following is MOST important to ensure successful alignment with the overall inten Zero Trust?
When an organization is having new software implemented under contract, which of the following is key to controlling escalating costs?
Which of the following is a drawback in the use of quantitative risk analysis?
Which of the following would provide the BEST evidence of an effective internal control environment/?
Which of the following will BEST help to ensure key risk indicators (KRIs) provide value to risk owners?
Which of the following is the MOST important consideration for prioritizing risk treatment plans when faced with budget limitations?
Which of the following is MOST important when creating a program to reduce ethical risk?
Which of the following IT key risk indicators (KRIs) provides management with the BEST feedback on IT capacity?
A control owner identifies that the organization ' s shared drive contains personally identifiable information (Pll) that can be accessed by all personnel. Which of the following is the MOST effective risk response?
Which of the following is the MOST important component in a risk treatment plan?
Which of the following is the MAIN benefit of involving stakeholders in the selection of key risk indicators (KRIs)?
An insurance company handling sensitive and personal information from its customers receives a large volume of telephone requests and electronic communications daily. Which of the following
is MOST important to include in a risk awareness training session for the customer service department?
Which of the following would MOST effectively reduce risk associated with an increase of online transactions on a retailer website?
A risk practitioner is evaluating policies defined by an organization as part of its IT security framework. Which of the following would be of GREATEST concern?
An organization ' s business gap analysis reveals the need for a robust IT risk strategy. Which of the following should be the risk practitioner ' s PRIMARY consideration when participating in development of the new strategy?
Days before the realization of an acquisition, a data breach is discovered at the company to be acquired. For the accruing organization, this situation represents which of the following?
Key risk indicators (KRIs) are MOST useful during which of the following risk management phases?
Which of the following is the PRIMARY purpose of creating and documenting control procedures?
Which of the following provides the BEST evidence that risk responses have been executed according to their risk action plans?
A business unit has implemented robotic process automation (RPA) for its
repetitive back-office tasks. Which of the following should be the risk
practitioner ' s GREATEST concern?
An organization has detected unauthorized logins to its client database servers. Which of the following should be of GREATEST concern?
Improvements in the design and implementation of a control will MOST likely result in an update to:
Which of the following controls BEST helps to ensure that transaction data reaches its destination?
Which of the following provides the MOST important information to facilitate a risk response decision?
Which of the following is the MOST effective way to help ensure future risk levels do not exceed the organization ' s risk appetite?
A segregation of duties control was found to be ineffective because it did not account for all applicable functions when evaluating access. Who is responsible for ensuring the control is designed to effectively address risk?
A risk practitioner has identified that the organization ' s secondary data center does not provide redundancy for a critical application. Who should have the authority to accept the associated risk?
An organization has recently hired a large number of part-time employees. During the annual audit, it was discovered that many user IDs and passwords were documented in procedure manuals for use by the part-time employees. Which of the following BEST describes this situation?
Which of the following is MOST helpful to ensure effective security controls for a cloud service provider?
Which of the following BEST supports the communication of risk assessment results to stakeholders?
Which of the following is the MOST effective way to identify changes in the performance of the control environment?
An organization has allowed several employees to retire early in order to avoid layoffs Many of these employees have been subject matter experts for critical assets Which type of risk is MOST likely to materialize?
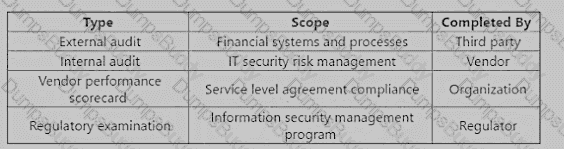
After a high-profile systems breach at an organization s key vendor, the vendor has implemented additional mitigating controls. The vendor has voluntarily shared the following set of assessments:
Which of the assessments provides the MOST reliable input to evaluate residual risk in the vendor ' s control environment?
Which of the following BEST provides an early warning that network access of terminated employees is not being revoked in accordance with the service level agreement (SLA)?
Which of the following is the MOST important benefit of key risk indicators (KRIs) '
A threat intelligence team has identified an indicator of compromise related to an advanced persistent threat (APT) actor. Which of the following is the risk practitioner ' s BEST course of action?
A risk manager has determined there is excessive risk with a particular technology. Who is the BEST person to own the unmitigated risk of the technology?
Which of the following is the GREATEST benefit of developing IT risk scenarios?
Digital signatures are an effective control method for information exchange over an insecure network because they:
Which of the following is the MOST important key performance indicator (KPI) to establish in the service level agreement (SLA) for an outsourced data center?
An IT license audit has revealed that there are several unlicensed copies of co be to:
Which of the following will be MOST effective in uniquely identifying the originator of electronic transactions?
A cote data center went offline abruptly for several hours affecting many transactions across multiple locations. Which of the to " owing would provide the MOST useful information to determine mitigating controls?
The BEST way to demonstrate alignment of the risk profile with business objectives is through:
Which of the following is the MOST significant risk associated with using cloud computing for disaster recovery?
Which of the following is the BEST indication that key risk indicators (KRls) should be revised?
Which of the following BEST indicates the efficiency of a process for granting access privileges?
An organization is conducting a review of emerging risk. Which of the following is the BEST input for this exercise?
Which of the following is the MOST effective way 10 identify an application backdoor prior to implementation ' ?
Which of the following is the MOST effective way lo ensure professional ethics are maintained as a core organizational value and adhered to by employees?
An organization has adopted an emerging technology without following proper processes. Which of the following is the risk practitioner ' s BEST course of action to address this risk?
An organization is concerned that its employees may be unintentionally disclosing data through the use of social media sites. Which of the following will MOST effectively mitigate tins risk?
Which of the following is the MAIN benefit to an organization using key risk indicators (KRIs)?
Which of the following is the MOST important component of effective security incident response?
Which of the following practices MOST effectively safeguards the processing of personal data?
Technical controls affecting access permissions for systems should be implemented according to:
A data center has recently been migrated to a jurisdiction where heavy fines will be imposed should leakage of customer personal data occur. Assuming no other changes to the operating environment, which factor should be updated to reflect this situation as an input to scenario development for this particular risk event?
Which of the following is MOST likely to be impacted when a global organization is required by law to implement a new data protection regulation across its operations?
A rule-based data loss prevention {DLP) tool has recently been implemented to reduce the risk of sensitive data leakage. Which of the following is MOST likely to change as a result of this implementation?
Which of the following is MOST important to the effectiveness of key performance indicators (KPIs)?
As part of its risk strategy, an organization decided to transition its financial system from a cloud-based provider to an internally managed system. Which of the following should the risk practitioner do FIRST?
Which of the following BEST enables a proactive approach to minimizing the potential impact of unauthorized data disclosure?
An organization recently implemented an extensive risk awareness program after a cybersecurity incident. Which of the following is MOST likely to be affected by the implementation of the program?
Which of the following BEST indicates the risk appetite and tolerance level (or the risk associated with business interruption caused by IT system failures?
Which of the following is the BEST way to help ensure risk will be managed properly after a business process has been re-engineered?
A key risk indicator (KRI) indicates a reduction in the percentage of appropriately patched servers. Which of the following is the risk practitioner ' s BEST course of action?
Which of the following scenarios presents the GREATEST risk of noncompliance with data privacy best practices?
Which of the following is the ULTIMATE goal of conducting a privacy impact analysis (PIA)?
Which of the following would MOST likely result in updates to an IT risk appetite statement?
Which of the following presents the GREATEST challenge to managing an organization ' s end-user devices?
Which of the following will BEST help in communicating strategic risk priorities?
Which of the following is the MOST critical consideration when awarding a project to a third-party service provider whose servers are located offshore?
An organization has decided to implement a new Internet of Things (loT) solution. Which of the following should be done FIRST when addressing security concerns associated with this new technology?
An organization has received notification that it is a potential victim of a cybercrime that may have compromised sensitive customer data. What should be The FIRST course of action?
During an acquisition, which of the following would provide the MOST useful input to the parent company ' s risk practitioner when developing risk scenarios for the post-acquisition phase?
Which of the following provides the BEST evidence that a selected risk treatment plan is effective?
Which of the following is MOST helpful to management when determining the resources needed to mitigate a risk?
Malware has recently affected an organization. The MOST effective way to resolve this situation and define a comprehensive risk treatment plan would be to perform:
Which of the following is the BEST approach when a risk practitioner has been asked by a business unit manager for special consideration during a risk assessment of a system?
A highly regulated enterprise is developing a new risk management plan to specifically address legal and regulatory risk scenarios What should be done FIRST by IT governance to support this effort?
Which of the following shortcomings of perimeter security does Zero Trust aim to resolve?
What is the MOST effective approach to promote ethical decision-making in a global organization?
Which of the following is the MOST essential characteristic of a good IT risk scenario?
Which of the following is MOST helpful in reducing the likelihood of inaccurate risk assessment results?
An organization is measuring the effectiveness of its change management program to reduce the number of unplanned production changes. Which of the following would be the BEST metric to determine if the program is performing as expected?
A risk practitioner is concerned with potential data loss in the event of a breach at a hosted third-party provider. Which of the following is the BEST way to mitigate this risk?
What is the PRIMARY reason an organization should include background checks on roles with elevated access to production as part of its hiring process?
To minimize the risk of a potential acquisition being exposed externally, an organization has selected a few key employees to be engaged in the due diligence process. A member of the due diligence team realizes a close acquaintance is a high-ranking IT professional at a subsidiary of the company about to be acquired. What is the BEST course of action for this team member?
A global organization is considering the acquisition of a competitor. Senior management has requested a review of the overall risk profile from the targeted organization. Which of the following components of this review would provide the MOST useful information?
An internal audit report reveals that a legacy system is no longer supported Which of the following is the risk practitioner ' s MOST important action before recommending a risk response '
Which of the following will BEST help to ensure implementation of corrective action plans?
Which of the following is the PRIMARY purpose of analyzing control effectiveness during risk analysis?
Which of the following practices would be MOST effective in protecting personality identifiable information (Ptl) from unauthorized access m a cloud environment?
Which of the following should be done FIRST when developing an initial set of risk scenarios for an organization?
Which of the following is the GREATEST benefit of reviewing security trends reported by a log monitoring system?
An organization has operations in a location that regularly experiences severe weather events. Which of the following would BEST help to mitigate the risk to operations?
A risk practitioner is reviewing accountability assignments for data risk in the risk register. Which of the following would pose the GREATEST concern?
Which of the following is the BEST course of action when an organization wants to reduce likelihood in order to reduce a risk level?
The MAIN purpose of reviewing a control after implementation is to validate that the control:
Which of the following is the BEST control to prevent unauthorized access to an organization ' s critical assets?
The PRIMARY reason for periodically monitoring key risk indicators (KRIs) is to:
An organization is implementing data warehousing infrastructure. Senior management is concerned about safeguarding client data security in this new environment. Which of the following should the risk practitioner recommend be done NEXT?
An external security audit has reported multiple findings related to control noncompliance. Which of the following would be MOST important for the risk practitioner to communicate to senior management?
Which of the following is a PRIMARY benefit of engaging the risk owner during the risk assessment process?
Which of the following is the MOST appropriate key performance indicator (KPI) to measure change management performance?
Which of the following is the MOST important consideration when establishing a recovery point objective (RPO)?
A penetration test reveals several vulnerabilities in a web-facing application. Which of the following should be the FIRST step in selecting a risk response?
A key performance indicator (KPI) has been established to monitor the number of software changes that fail and must be re-implemented. An increase in the KPI indicates an ineffective:
Which of the following is a risk practitioner ' s BEST recommendation to senior management when the cost to mitigate a risk scenario exceeds the financial impact should the risk materialize?
Which of the following should be the risk practitioner s PRIMARY focus when determining whether controls are adequate to mitigate risk?
A process maturity model is MOST useful to the risk management process because it helps:
Which of the following would provide the MOST useful information to a risk owner when reviewing the progress of risk mitigation?
Reviewing which of the following provides the BEST indication of an organizations risk tolerance?
Which of the following is the BEST indication of an improved risk-aware culture following the implementation of a security awareness training program for all employees?
When is the BEST to identify risk associated with major project to determine a mitigation plan?
Senior leadership has set guidelines for the integration of a new acquisition. The guidelines allow for a variation in the level of risk-taking. The variation indicates which of the following risk management concepts?
A risk practitioner ' s BEST guidance to help an organization develop relevant risk scenarios is to ensure the scenarios are:
The BEST way to validate that a risk treatment plan has been implemented effectively is by reviewing:
Which of the following is the MOST important reason for an organization to regularly assess the design of key risk indicators (KRIs)?
A public online information security training course is available to an organization ' s staff. The online course contains free-form discussion fields. Which of the following should be of MOST concern to the organization ' s risk practitioner?
Which of the following should be done FIRST when a new risk scenario has been identified
Where should a risk practitioner document the current state and desired future state of organizational risk?
Which of the following is the BEST way for a risk practitioner to consolidate the results of risk assessments across multiple operating units?
Which of the following provides the MOST useful information when determining if a specific control should be implemented?
Which of the following describes the relationship between risk appetite and risk tolerance?
To reduce costs, an organization is combining the second and third tines of defense in a new department that reports to a recently appointed C-level executive. Which of the following is the GREATEST concern with this situation?
Which of the following BEST indicates how well a web infrastructure protects critical information from an attacker?
Which of the following is the PRIMARY reason to perform ongoing risk assessments?
An IT risk practitioner has been tasked to engage key stakeholders to assess risk for key IT risk scenarios. Which of the following is the PRIMARY benefit of this activity?
An organization uses a biometric access control system for authentication and access to its server room. Which control type has been implemented?
Which of the following is the MOST important consideration when determining whether to accept residual risk after security controls have been implemented on a critical system?
Which of the following is the BEST key control indicator (KCI) for measuring the security of a blockchain network?
Senior management wants to increase investment in the organization ' s cybersecurity program in response to changes in the external threat landscape. Which of the following would BEST help to prioritize investment efforts?
An organization has been notified that a disgruntled, terminated IT administrator has tried to break into the corporate network. Which of the following discoveries should be of GREATEST concern to the organization?
Which of the following would provide the MOST objective assessment of the effectiveness of an organization ' s security controls?
Which of the following is the MOST important reason for a risk practitioner to continuously monitor a critical security transformation program?
Which of the following is a risk practitioner ' s BEST course of action upon learning that regulatory authorities have concerns with an emerging technology the organization is considering?
Which of the following BEST enables an organization to increase the likelihood of identifying risk associated with unethical employee behavior?
Management has determined that it will take significant time to remediate exposures in the current IT control environment. Which of the following is the BEST course of action?
Which of the following will BEST mitigate the risk associated with IT and business misalignment?
The PRIMARY benefit of conducting a risk workshop using a top-down approach instead of a bottom-up approach is the ability to:
Which of the following is the GREATEST concern when using a generic set of IT risk scenarios for risk analysis?
An organization has contracted with a cloud service provider to support the deployment of a new product. Of the following, who should own the associated risk?
An organization has identified a risk exposure due to weak technical controls in a newly implemented HR system. The risk practitioner is documenting the risk in the risk register. The risk should be owned by the:
Which of the following should be used as the PRIMARY basis for evaluating the state of an organization ' s cloud computing environment against leading practices?
A risk practitioner is reviewing a vendor contract and finds there is no clause to control privileged access to the organization ' s systems by vendor employees. Which of the following is the risk practitioner ' s BEST course of action?
An organization planning to transfer and store its customer data with an offshore cloud service provider should be PRIMARILY concerned with:
An organization is developing a risk universe to create a holistic view of its overall risk profile. Which of the following is the GREATEST barrier to achieving the initiative ' s objectives?
Which of the following is MOST helpful in developing key risk indicator (KRl) thresholds?
An organization is making significant changes to an application. At what point should the application risk profile be updated?
Which of the following observations should be of GREATEST concern to a risk practitioner assessing a third-party service provider for privacy risk?
An automobile manufacturer is considering implementing an Internet of Things (IoT) network to improve customer service by collecting customer and vehicle data. Which of the following would be the risk practitioner’s BEST recommendation?
When creating a program to manage data privacy risk, which of the following is MOST important to ensure that the program is successful?
An engineer has been assigned to conduct data restoration after a server storage failure. However, the procedure was not successful. Which of the following is the MOST probable cause of this situation?
The BEST key performance indicator (KPI) to measure the effectiveness of a backup process would be the number of:
Deviation from a mitigation action plan ' s completion date should be determined by which of the following?
An organization wants to grant remote access to a system containing sensitive data to an overseas third party. Which of the following should be of GREATEST concern to management?
Which types of controls are BEST used to minimize the risk associated with a vulnerability?
A newly hired risk practitioner finds that the risk register has not been updated in the past year. What is the risk practitioner ' s BEST course of action?
Which of the following should be of MOST concern to a risk practitioner reviewing an organization risk register after the completion of a series of risk assessments?
Prior to selecting key performance indicators (KPIs), itis MOST important to ensure:
A risk practitioner has identified that the agreed recovery time objective (RTO) with a Software as a Service (SaaS) provider is longer than the business expectation. Which of the following is the risk practitioner ' s BEST course of action?
Which of the following would be the GREATEST challenge when implementing a corporate risk framework for a global organization?
The number of tickets to rework application code has significantly exceeded the established threshold. Which of the following would be the risk practitioner s BEST recommendation?
What should a risk practitioner do FIRST when vulnerability assessment results identify a weakness in an application?
When reporting on risk for the purpose of initiating required corrective actions, the results should be submitted to the:
The BEST metric to demonstrate that servers are configured securely is the total number of servers:
An organization allows programmers to change production systems in emergency situations. Which of the following is the BEST control?
Which of the following is MOST important for an organization to have in place to identify unauthorized devices on the network?
Which of the following BEST enables detection of ethical violations committed by employees?
Which of the following is the MOST important risk management activity during project initiation?
Which of the following is the PRIMARY reason for a risk practitioner to review an organization ' s IT asset inventory?
Which of the following is the BEST approach for performing a business impact analysis (BIA) of a supply-chain management application?
Which of the following should be the PRIMARY basis for deciding whether to disclose information related to risk events that impact external stakeholders?
Which of the following is the PRIMARY reason for an organization to include an acceptable use banner when users log in?
Which of the following factors will have the GREATEST impact on the implementation of a risk mitigation strategy for an organization?
Which of the following provides the BEST protection for Internet of Things (loT) devices that are accessed within an organization?
When reviewing a report on the performance of control processes, it is MOST important to verify whether the:
For a large software development project, risk assessments are MOST effective when performed:
Which of the following is MOST important for an organization that wants to reduce IT operational risk?
When an organization ' s business continuity plan (BCP) states that it cannot afford to lose more than three hours of a critical application ' s data, the three hours is considered the application’s:
Which of the following provides the MOST insight regarding an organization ' s risk culture?
Which of the following is the BEST way to determine the value of information assets for risk management purposes?
Which of the following BEST indicates that an organization ' s risk management processes are mature?
An organization is analyzing the risk of shadow IT usage. Which of the following is the MOST important input into the assessment?
From a risk management perspective, which of the following is the PRIMARY purpose of conducting a root cause analysis following an incident?
Which of the following is MOST important when considering risk in an enterprise risk management (ERM) process?
Which of the following is the MOST important consideration for protecting data assets m a Business application system?
Which of the following is the BEST way to determine the value of information assets for risk management purposes?
Who is BEST suited to provide information to the risk practitioner about the effectiveness of a technical control associated with an application?
The MOST important reason to monitor key risk indicators (KRIs) is to help management:
An IT organization is replacing the customer relationship management (CRM) system. Who should own the risk associated with customer data leakage caused by insufficient IT security controls for the new system?
Which of the following is the BEST way to manage the risk associated with malicious activities performed by database administrators (DBAs)?
IT management has deployed a major update to reduce the risk of system compromise. What is the BEST way to validate the effectiveness of this control?
During an organization ' s simulated phishing email campaign, which of the following is the BEST indicator of a mature security awareness program?
Which of the following is the MOST important consideration for a risk practitioner when making a system implementation go-live recommendation?
A global organization has implemented an application that does not address all privacy requirements across multiple jurisdictions. Which of the following risk responses has the organization adopted with regard to privacy requirements?
Which of the following scenarios presents the GREATEST risk for a global organization when implementing a data classification policy?
An IT risk practitioner has been asked to regularly report on the overall status and effectiveness of the IT risk management program. Which of the following is MOST useful for this purpose?
Which of the following BEST facilitates the identification of appropriate key performance indicators (KPIs) for a risk management program?
Upon learning that the number of failed backup attempts continually exceeds
the current risk threshold, the risk practitioner should:
Which of the following should be determined FIRST when a new security vulnerability is made public?
During a review of the asset life cycle process, a risk practitioner identified several unreturned and unencrypted laptops belonging to former employees. Which of the following is the GREATEST concern with this finding?
Which of the following BEST indicates that risk management is embedded into the responsibilities of all employees?
Which of the following is the PRIMARY responsibility of the first line of defense related to computer-enabled fraud?
An organization ' s senior management is considering whether to acquire cyber insurance. Which of the following is the BEST way for the risk practitioner to enable management’s decision?
Which of the following should be the PRIMARY consideration when prioritizing limited resources needed to implement overdue corrective actions arising from a recent internal audit?
What would be MOST helpful to ensuring the effective implementation of a new cybersecurity program?
Which of the following is MOST important for an organization to have in place when developing a risk management framework?
An organization is unable to implement a multi-factor authentication requirement until the next fiscal year due to budget constraints. Consequently, a policy exception must be submitted. Which of the following is MOST important to include in the analysis of the exception?
Which of the following is the MOST important technology control to reduce the likelihood of fraudulent payments committed internally?
Which of the following is the MOST important responsibility of a business process owner to enable effective IT risk management?
An organization ' s IT team has proposed the adoption of cloud computing as a cost-saving measure for the business. Which of the following should be of GREATEST concern to the risk practitioner?
In response to the threat of ransomware, an organization has implemented cybersecurity awareness activities. The risk practitioner ' s BEST recommendation to further reduce the impact of ransomware attacks would be to implement:
Which of the following is the BEST way to validate whether controls to reduce user device vulnerabilities have been implemented according to management ' s action plan?
Which of the following is the PRIMARY objective of maintaining an information asset inventory?
Which of the following is MOST important to consider when selecting risk indicators (KRIs)? The ability to:
After migrating a key financial system to a new provider, it was discovered that a developer could gain access to the production environment. Which of the following is the BEST way to mitigate the risk in this situation?
Which of the following is a risk practitioner ' s MOST important course of action when the level of risk has exceeded risk tolerance?
Which of the following management actions will MOST likely change the likelihood rating of a risk scenario related to remote network access?
The risk associated with an asset after controls are applied can be expressed as:
Which of the following BEST enables senior management lo compare the ratings of risk scenarios?
Which of the following is the MOST useful information for prioritizing risk mitigation?
Which of the following is the PRIMARY objective of the three lines model for risk management?
Which of the following is MOST useful when performing a quantitative risk assessment?
Which of the following is MOST important to the effectiveness of a senior oversight committee for risk monitoring?
Which group has PRIMARY ownership of reputational risk stemming from unethical behavior within the organization?
Business areas within an organization have engaged various cloud service providers directly without assistance from the IT department. What should the risk practitioner do?
Which of the following is a responsibility of the second line of defense in the three lines of defense model?
Which of the following is the MOST useful indicator to measure the efficiency of an identity and access management process?
Which of the following is the MOST effective way to evaluate control implementation processes?
The MOST significant benefit of using a consistent risk ranking methodology across an organization is that it enables:
While reviewing an organization ' s monthly change management metrics, a risk practitioner notes that the number of emergency changes has increased substantially Which of the following would be the BEST approach for the risk practitioner to take?
Which of the following risk events would require the creation of a business continuity plan (BCP)?
Which of the following activities is PRIMARILY the responsibility of senior management?
After undertaking a risk assessment of a production system, the MOST appropriate action is for the risk manager to:
An organization has identified the need to implement an asset tiering model to establish the appropriate level of impact. Which of the following is the MOST effective risk assessment methodology for a risk practitioner to use for this initiative?
What is the GREATEST concern with maintaining decentralized risk registers instead of a consolidated risk register?
Which of the following is a crucial component of a key risk indicator (KRI) to ensure appropriate action is taken to mitigate risk?
Which of the following is the MOST important foundational element of an effective three lines of defense model for an organization?
What is the MOST important consideration when aligning IT risk management with the enterprise risk management (ERM) framework?
Which of the following BEST indicates the effective implementation of a risk treatment plan?
A business is conducting a proof of concept on a vendor ' s Al technology. Which of the following is the MOST important consideration for managing risk?
When developing risk treatment alternatives for a Business case, it is MOST helpful to show risk reduction based on:
An organization has experienced a cyber-attack that exposed customer personally identifiable information (Pll) and caused extended outages of network services. Which of the following stakeholders are MOST important to include in the cyber response team to determine response actions?
A risk practitioner has learned that an effort to implement a risk mitigation action plan has stalled due to lack of funding. The risk practitioner should report that the associated risk has been:
When presenting risk, the BEST method to ensure that the risk is measurable against the organization ' s risk appetite is through the use of a:
Which of the following is the BEST metric to demonstrate the effectiveness of an organization ' s change management process?
Reviewing historical risk events is MOST useful for which of the following processes within the risk management life cycle?
An organization has introduced risk ownership to establish clear accountability for each process. To ensure effective risk ownership, it is MOST important that:
Which of the following process controls BEST mitigates the risk of an employee issuing fraudulent payments to a vendor?
Which of the following is the MOST appropriate key control indicator (KCI) to help an organization prevent successful cyber risk events on the external-facing infrastructure?
The GREATEST benefit of including low-probability, high-impact events in a risk assessment is the ability to:
An organization has an approved bring your own device (BYOD) policy. Which of the following would BEST mitigate the security risk associated with the inappropriate use of enterprise applications on the devices?
During a risk assessment of a financial institution, a risk practitioner discovers that tellers can initiate and approve transactions of significant value. This team is also responsible for ensuring transactions are recorded and balances are reconciled by the end of the day. Which of the following is the risk practitioner ' s BEST recommendation to mitigate the associated risk?
The acceptance of control costs that exceed risk exposure MOST likely demonstrates:
Which of the following is the GREATEST benefit of updating the risk register to include outcomes from a risk assessment?
In the context of the three lines model, which of the following is responsible for providing assurance to senior management and the governing body through independent and objective reviews?
Which of the following is the GREATEST benefit to an organization when updates to the risk register are made promptly after the completion of a risk assessment?
Which of the following would be MOST helpful to an information security management team when allocating resources to mitigate exposures?
Which element of an organization ' s risk register is MOST important to update following the commissioning of a new financial reporting system?
Which of the following would BEST prevent an unscheduled application of a patch?
An application runs a scheduled job that compiles financial data from multiple business systems and updates the financial reporting system. If this job runs too long, it can delay financial reporting. Which of the following is the risk practitioner ' s BEST recommendation?
An organization plans to migrate sensitive information to a public cloud infrastructure. Which of the following is the GREATEST security risk in this scenario?
A risk register BEST facilitates which of the following risk management functions?
Which of the following is the GREATEST benefit of identifying appropriate risk owners?
Which of the following should be a risk practitioner’s MOST important consideration when developing IT risk scenarios?
Who is accountable for authorizing application access in a cloud Software as a Service (SaaS) solution?
A risk practitioner is assisting with the preparation of a report on the organization s disaster recovery (DR) capabilities. Which information would have the MOST impact on the overall recovery profile?
Which of the following is the BEST approach to mitigate the risk associated with a control deficiency?
A risk practitioner is reporting on an increasing trend of ransomware attacks in the industry. Which of the following information is MOST important to include to enable an informed response decision by key stakeholders?
Which of the following should be a risk practitioner ' s NEXT step upon learning the impact of an organization ' s noncompliance with a specific legal regulation?
Which of the following is the MOST important information to cover a business continuity awareness Ira nine, program for all employees of the organization?
A highly regulated organization acquired a medical technology startup company that processes sensitive personal information with weak data protection controls. Which of the following is the BEST way for the acquiring company to reduce its risk while still enabling the flexibility needed by the startup company?
Which of the following is the MOST effective way to determine if a risk factor exceeds risk tolerance?
The MOST appropriate key performance indicator (KPI) to communicate the effectiveness of an enterprise IT risk management program is:
Which of the following is the PRIMARY reason that risk management is important in project management?
Which of the following is the BEST way to validate privileged access to database accounts?
A risk practitioner has been asked to evaluate a new cloud-based service to enhance an organization ' s access management capabilities. When is the BEST time for the risk practitioner to provide opinions on control strength?
Which of the following is necessary to enable an IT risk register to be consolidated with the rest of the organization’s risk register?
Which of the following is the GREATEST advantage of implementing a risk management program?
Which organizational role should be accountable for ensuring information assets are appropriately classified?
Which of the following is the BEST recommendation when a key risk indicator (KRI) is generating an excessive volume of events?
Which of the following actions should a risk practitioner do NEXT when an increased industry trend of external cyber attacks is identified?
Which of the following is the PRIMARY reason to ensure software engineers test patches before release to the production environment?
Which of the following helps ensure compliance with a nonrepudiation policy requirement for electronic transactions?
Which of the following is the GREATEST concern when an organization uses a managed security service provider as a firewall administrator?
Which of the following is MOST important when discussing risk within an organization?
Which of the following elements of a risk register is MOST likely to change as a result of change in management ' s risk appetite?
Implementing which of the following will BEST help ensure that systems comply with an established baseline before deployment?
A business unit has decided to accept the risk of implementing an off-the-shelf, commercial software package that uses weak password controls. The BEST course of action would be to:
Which of the following is the BEST approach for determining whether a risk action plan is effective?
An organization is planning to outsource its payroll function to an external service provider Which of the following should be the MOST important consideration when selecting the provider?
When determining the accuracy of a key risk indicator (KRI), it is MOST important that the indicator:
An organization has outsourced its ERP application to an external SaaS provider. Which of the following provides the MOST useful information to identify risk scenarios involving data loss?
A risk assessment has revealed that the probability of a successful cybersecurity attack is increasing. The potential loss could exceed the organization ' s risk appetite. Which of the following ould be the MOST effective course of action?
Senior management has asked the risk practitioner for the overall residual risk level for a process that contains numerous risk scenarios. Which of the following should be provided?
An organization operates in a jurisdiction where heavy fines are imposed for leakage of customer data. Which of the following provides the BEST input to assess the inherent risk impact?
An organization ' s risk profile indicates that residual risk levels have fallen significantly below management ' s risk appetite. Which of the following is the BEST course of action?
Which of the following would require updates to an organization ' s IT risk register?
Which of the following would provide the MOST comprehensive information for updating an organization ' s risk register?
Which of the following is the MOST important consideration when determining the appropriate data retention period throughout the data management life cycle?
Following a significant change to a business process, a risk practitioner believes the associated risk has been reduced. The risk practitioner should advise the risk owner to FIRST
A risk owner has accepted a high-impact risk because the control was adversely affecting process efficiency. Before updating the risk register, it is MOST important for the risk practitioner to:
An organization has restructured its business processes, and the business continuity plan (BCP) needs to be revised accordingly. Which of the following should be identified FIRST?
What should a risk practitioner do FIRST when an assessment reveals a control is not operating as intended?
Which of the following would be MOST helpful in assessing the risk associated with data loss due to human vulnerabilities?
A recent audit identified high-risk issues in a business unit though a previous control self-assessment (CSA) had good results. Which of the following is the MOST likely reason for the difference?
Which of the following is the GREATEST risk associated with an environment that lacks documentation of the architecture?
A service provider is managing a client’s servers. During an audit of the service, a noncompliant control is discovered that will not be resolved before the next audit because the client cannot afford the downtime required to correct the issue. The service provider’s MOST appropriate action would be to:
An organization has completed a risk assessment of one of its service providers. Who should be accountable for ensuring that risk responses are implemented?
A recent big data project has resulted in the creation of an application used to support important investment decisions. Which of the following should be of GREATEST concern to the risk practitioner?
Which of the following BEST indicates that a control has been implemented successfully?
Which of the following is the MOST important topic to cover in a risk awareness training program for all staff?
Of the following, who is responsible for approval when a change in an application system is ready for release to production?
Which of the following is the BEST indicator of the effectiveness of a control?
Vulnerabilities have been detected on an organization ' s systems. Applications installed on these systems will not operate if the underlying servers are updated. Which of the following is the risk practitioner ' s BEST course of action?
Which of the following is the MOST important reason to validate that risk responses have been executed as outlined in the risk response plan ' '
Which of the following BEST helps to balance the costs and benefits of managing IT risk?
Which of the following functions independently reviews and provides feedback regarding the achievement of organizational objectives?
Of the following, who is accountable for ensuing the effectiveness of a control to mitigate risk?
Which of the following would BEST facilitate the maintenance of data classification requirements?
Which of the following is the GREATEST risk of relying on artificial intelligence (Al) within heuristic security systems?
Which of the following BEST helps to identify significant events that could impact an organization?
Reviewing which of the following BEST helps an organization gam insight into its overall risk profile ' '
A user has contacted the risk practitioner regarding malware spreading laterally across the organization ' s corporate network. Which of the following is the risk practitioner’s BEST course of action?
An organization becomes aware that IT security failed to detect a coordinated
cyber attack on its data center. Which of the following is the BEST course of
action?
When reviewing the business continuity plan (BCP) of an online sales order system, a risk practitioner notices that the recovery time objective (RTO) has a shorter lime than what is defined in the disaster recovery plan (DRP). Which of the following is the BEST way for the risk practitioner to address this concern?
Which of the following is the MOST important factor affecting risk management in an organization?
Within the three lines of defense model, the accountability for the system of internal control resides with:
A key risk indicator (KRI) that incorporates data from external open-source threat intelligence sources has shown changes in risk trend data. Which of the following is MOST important to update in the risk register?
Which of the following is the MOST important reason for integrating IT risk management practices into enterprise risk management (ERM)?
Which of the following is the BEST way to mitigate the risk associated with fraudulent use of an enterprise ' s brand on Internet sites?
When of the following 15 MOST important when developing a business case for a proposed security investment?
An organization recently implemented a cybersecurity awareness program that includes phishing simul-ation exercises for all employees. What type of control is being utilized?
Which of the following is MOST important for a risk practitioner to understand about an organization in order to create an effective risk
awareness program?
The software version of an enterprise ' s critical business application has reached end-of-life and is no longer supported by the vendor. IT has decided to develop an in-house replacement application. Which of the following should be the PRIMARY concern?
From a data protection and regulatory compliance perspective, which of the following is the MOST important reason for a global organization to use immutable backups?
The PRIMARY benefit of selecting an appropriate set of key risk indicators (KRIs) is that they:
Which of the following is MOST helpful in identifying loss magnitude during risk analysis of a new system?
During the initial risk identification process for a business application, it is MOST important to include which of the following stakeholders?
Which of the following is the FIRST step when conducting a business impact analysis (BIA)?
An organization has established a contract with a vendor that includes penalties for loss of availability. Which risk treatment has been adopted by the organization?
Which of the following is the MOST effective way for a large and diversified organization to minimize risk associated with unauthorized software on company devices?
An organization has an internal control that requires all access for employees be removed within 15 days of their termination date. Which of the following should the risk practitioner use to monitor
adherence to the 15-day threshold?
Which of the following is MOST important to include in a Software as a Service (SaaS) vendor agreement?
A risk practitioner is preparing a report to communicate changes in the risk and control environment. The BEST way to engage stakeholder attention is to:
Which of the following is the BEST way to address a board ' s concern about the organization ' s current cybersecurity posture?
An organization that has been the subject of multiple social engineering attacks is developing a risk awareness program. The PRIMARY goal of this program should be to:
Which of the following provides the MOST insight into an organization ' s IT threat exposure?
An external data source has released an advisory about a critical vulnerability affecting a widely used software application. Which of the following should the risk practitioner do FIRST?
The results of a risk assessment reveal risk scenarios with high impact and low likelihood of occurrence. Which of the following would be the BEST action to address these scenarios?
Which of the following is the BEST indication of the effectiveness of a business continuity program?
Which of the following would have the GREATEST impact on reducing the risk associated with the implementation of a big data project?
Which of the following BEST enables a risk practitioner to understand management ' s approach to organizational risk?
Which of the following is a risk practitioner ' s BEST course of action when a control is not meeting agreed-upon performance criteria?
When assessing the maturity level of an organization ' s risk management framework, which of the following should be of GREATEST concern to a risk practitioner?
A small organization finds it difficult to implement separation of duties necessary to mitigate the likelihood of system misuse. Which of the following would be the BEST compensating control?
An organization requires data owners to perform a quarterly review of all privileged users on key financial systems. What type of control does this represent?
A department allows multiple users to perform maintenance on a system using a single set of credentials. A risk practitioner determined this practice to be high-risk. Which of the following is the MOST effective way to mitigate this risk?
Which of the following deficiencies identified during a review of an organization ' s cybersecurity policy should be of MOST concern?
A risk practitioner has been asked to mark an identified control deficiency as remediated, despite concerns that the risk level is still too high. Which of the following is the BEST way to address this concern?
A business impact analysis (BIA) has documented the duration of maximum allowable outage for each of an organization ' s applications. Which of the following MUST be aligned with the maximum allowable outage?
Which of the following is MOST likely to result in a major change to the overall risk profile of the organization?
A risk practitioner has been made aware of a problem in an IT system that was missed during a routine risk assessment. Which of the following is the practitioner ' s BEST course of action?
During a risk assessment, what should an assessor do after identifying threats to organizational assets?
Which of the following should be the PRIMARY focus of a risk owner once a decision is made to mitigate a risk?
All business units within an organization have the same risk response plan for creating local disaster recovery plans. In an effort to achieve cost effectiveness, the BEST course of action would be to:
Winch of the following key control indicators (KCIs) BEST indicates whether security requirements are identified and managed throughout a project He cycle?
Which of the following controls BEST enables an organization to ensure a complete and accurate IT asset inventory?
After several security incidents resulting in significant financial losses, IT management has decided to outsource the security function to a third party that provides 24/7 security operation services. Which risk response option has management implemented?
Which of the following will BEST help to ensure that information system controls are effective?
What information is MOST helpful to asset owners when classifying organizational assets for risk assessment?
Which of the following is MOST important to consider when determining the value of an asset during the risk identification process?
A recent vulnerability assessment of a web-facing application revealed several weaknesses. Which of the following should be done NEXT to determine the risk exposure?
The BEST metric to monitor the risk associated with changes deployed to production is the percentage of:
PDF + Testing Engine
Testing Engine
PDF (Q&A)