Pre-Winter Sale 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: best70

CY0-001 CompTIA SecAI+ v1 Exam Questions and Answers

Questions 4

Which of the following describes the process of adjusting the distribution of underrepresented classes in an AI model data set to improve model performance?

Options:

A.

Data balancing

B.

Data lineage

C.

Data augmentation

D.

Data cleansing

Buy Now
Questions 5

A security consultant needs to detect attacks across a large language model (LLM) firewall.

Which of the following techniques should the consultant use?

Options:

A.

Signature matching

B.

Distributed denial-of-service

C.

Translation analysis

D.

Vulnerability enumeration

Buy Now
Questions 6

A cybersecurity administrator generates patching reports using AI, but the process takes a long time. Which of the following is the best way to increase performance?

Options:

A.

Deploy a Model Context Protocol (MCP) server to delegate several versions of this query to the back-end LLM simultaneously.

B.

Have the AI download the full CVE database first to prevent multiple similar external queries.

C.

Configure the AI system prompt to specify summarization algorithms.

D.

Increase the amount of model tokens available to eliminate time-consuming session restarts.

Buy Now
Questions 7

A data scientist is working with unlabeled data and wants to build a clustering model.

Which of the following techniques should a data scientist use?

Options:

A.

Supervised learning

B.

Reinforcement learning

C.

Unsupervised learning

D.

Semi-supervised learning

Buy Now
Questions 8

Which of the following controls is the best way to mitigate a denial-of-service (DoS) attack?

Options:

A.

Model guardrails

B.

Rate limiting

C.

End-to-end encryption

D.

Access controls

Buy Now
Questions 9

Which of the following attacks is most enabled by AI-generated content?

Options:

A.

Model poisoning

B.

Phishing

C.

Ransomware

D.

Remote code execution

Buy Now
Questions 10

Which of the following is an example of how a security analyst uses generative AI in the triage process?

Options:

A.

To predict the next attack target with higher accuracy

B.

To use statistical analysis for malicious code assessment

C.

To summarize security findings by category

D.

To tag malware using machine learning (ML) algorithms

Buy Now
Questions 11

Which of the following requires developers to harden infrastructure to protect AI systems?

Options:

A.

Intake processes

B.

Acceptable use policies

C.

Development guidelines

D.

Configuration standards

Buy Now
Questions 12

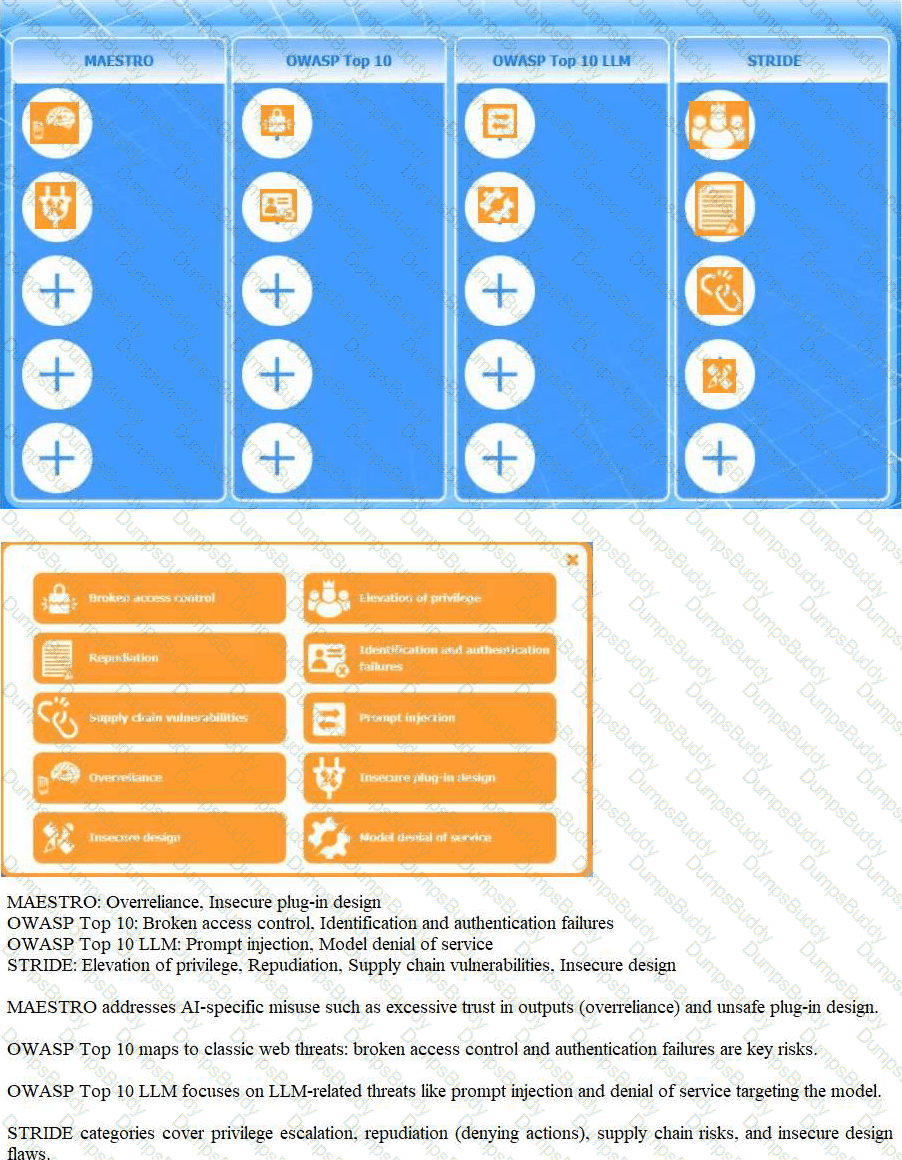
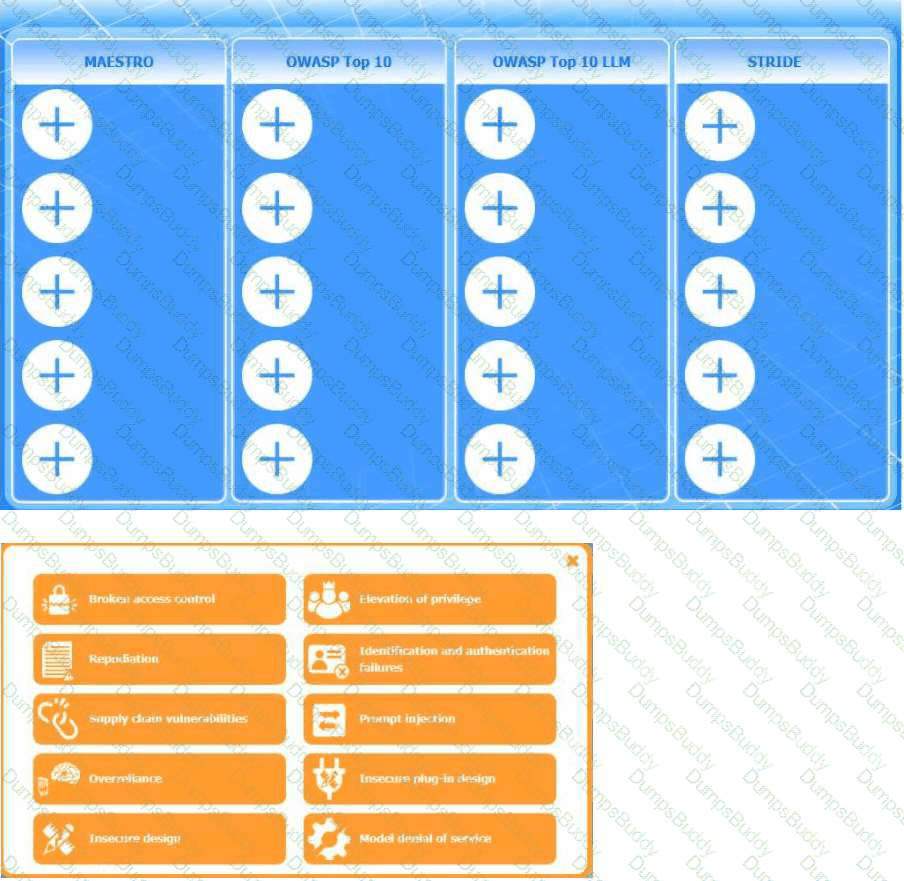
Instructions: Click the (+) to assign each threat category into its appropriate framework.

An architect is modeling an agentic system to meet security standards.
CY0-001 Question 12

Options:

Buy Now
Questions 13

A security team is using an AI-based tool to try to bypass organizational boundaries. The team uses AI to look at the current state and suggest different attack vectors based on the outcome of the previous ones.

Which of the following techniques is the team most likely using?

Options:

A.

Manual signature matching

B.

Code quality testing

C.

Fraud detection

D.

Automated penetration testing

Buy Now
Questions 14

A critical AI system cannot be shut down and must remain secure. Which of the following actions should be performed to apply controls?

Options:

A.

Removing the data encryption

B.

Patching critical vulnerabilities

C.

Scanning logs to detect anomalies

D.

Redeploying the production models

Buy Now
Questions 15

A security administrator wants to prevent prompt injection attacks and ensure responses have sanitized output.

Which of the following provides a primary compensating control for these requirements?

Options:

A.

Least privilege

B.

Encryption

C.

A large language model (LLM) firewall

D.

Rate limiting

Buy Now
Questions 16

Which of the following responsible AI standards refers to a principle that clearly states the reasons behind the decisions for a particular conclusion?

Options:

A.

Accountability

B.

Auditability

C.

Transparency

D.

Explainability

Buy Now
Questions 17

An administrator, who works for a financial institution, is required to implement data security controls for data at rest within AI systems that involve data disclosure.

Which of the following is the most suitable control?

Options:

A.

Data lineage

B.

Rate limits

C.

Encryption

D.

Masking

Buy Now
Questions 18

Which of the following is the most concerning risk for a company that allows corporate end users to use public-facing large language models (LLMs)?

Options:

A.

Inaccuracies due to hallucinations

B.

Out-of-date acceptable use policies

C.

Data security regulatory violations

D.

Malicious code generation

Buy Now
Questions 19

A company deploys an internet-facing chatbot using RAG. Logs show that an administrator can retrieve employee names and usernames while an employee receives ' information not available. ' Which of the following is reducing the risk of sensitive data exposure in this scenario?

Options:

A.

Data access controls

B.

Model-specific guardrails

C.

Rate limiting

D.

Prompt templates

Buy Now
Questions 20

An organization deploys a browser-based AI plug-in to detect malicious websites and phishing links in corporate email.

Which of the following techniques is used in this AI plug-in?

Options:

A.

Code quality testing

B.

Pattern recognition and signature matching

C.

Automated penetration testing

D.

Automated incident response

Buy Now
Questions 21

A developer is selecting authentication controls for an AI system.

Which of the following is the best way to prevent threat actor replay attacks?

Options:

A.

Identity provider (IdP) federation

B.

Secure Shell (SSH)-based certificate authentication

C.

Expiring session tokens

D.

Identity and access management access keys

Buy Now
Questions 22

Which of the following is the primary security risk when deploying AI models in production?

Options:

A.

Graphics processing unit (GPU) acceleration

B.

Model overfitting

C.

Model encryption

D.

Data exposure

Buy Now
Questions 23

Customer feedback for an AI chatbot has a high-rate of non-answers, which is causing higher central processing unit (CPU) utilization.

Which of the following should be implemented?

Options:

A.

Guardrails

B.

Response confidence level

C.

Prompt logging

D.

Cost monitoring

Buy Now
Questions 24

A security operations center (SOC) has a very high volume of logs and alerts. The manager proposes the implementation of a machine learning (ML) system to help with triage.

Which of the following tasks is most suitable?

Options:

A.

Applying filters on specific alerts

B.

Automatically patching vulnerable systems

C.

Identifying and classifying alerts

D.

Summarizing the content of alerts

Buy Now
Questions 25

A company develops an AI model to diagnose patients. Hospitals access the model through an integrated application programming interface (API). The security team performs a denial-of-service (DoS) attack via brute force on the model.

Which of the following controls would have prevented this issue?

Options:

A.

Tokenization

B.

Model guardrails

C.

Rate limiting

D.

Prompt firewall

Buy Now
Questions 26

A manufacturing company wants to use AI within its operations to improve the efficiency and accuracy of its processes.

Which of the following should the organization do first to enable adoption and achieve the business objectives?

Options:

A.

Achieve International Organization for Standardization (ISO) 42001 certification.

B.

Hire a data and AI architect.

C.

Select a large language model (LLM).

D.

Introduce a generative adversarial network (GAN).

Buy Now
Questions 27

A team of data scientists is ready to release a model for enterprise use. The team wants to protect the model from unintentional changes or tampering.

Which of the following is the most appropriate action?

Options:

A.

Change the model to a large language model (LLM) for interactive features with guardrails.

B.

Provide secure copies of the model for local runtime usage.

C.

Restrict access to only IT professionals in the organization.

D.

Integrate an application programming interface (API) with identity and access management (IAM) roles to interact with the model.

Buy Now
Questions 28

A cybersecurity analyst wants to choose a machine learning (ML) model to classify log entries while providing the best explainability.

Which of the following models should the analyst use?

Options:

A.

Large language model (LLM)

B.

Neural networks

C.

Decision trees

D.

Generative adversarial network (GAN)

Buy Now
Questions 29

A short AI-generated video shows a celebrity ' s likeness talking about a fake public security event.

Which of the following was used to create this video?

Options:

A.

Statistical analysis

B.

Convolutional neural network

C.

Machine learning (ML) classifier

D.

Random forest

Buy Now
Questions 30

After the latest software update, a developer receives reports that the system no longer requires reauthentication to display account balances because this issue was present in a previous release. Which of the following should the developer do to best mitigate the risk of recurrence?

Options:

A.

Ensure that AI approvals are required to push changes into production.

B.

Implement AI regression testing into the continuous integration/continuous deployment (CI/CD) pipeline.

C.

Deploy an AI-assisted change management system to schedule and track feature releases.

D.

Use code commit automation to perform AI-assisted static application security testing (SAST) scans.

Buy Now
Questions 31

A team of engineers builds an application using a large language model (LLM). The application is built on Linux and is hosted on a virtual server. Users must create an account in order to access and use the platform.

Which of the following should the team do to protect the account credentials?

Options:

A.

Patch the model with the latest data set.

B.

Update the Linux and virtual servers.

C.

Implement hashing and encryption.

D.

Deploy an authenticated application programming interface (API).

Buy Now
Questions 32

An AI architect reviews AI utilization and wants to improve the user experience.

Which of the following should the architect review within the logs?

Options:

A.

Rate monitoring

B.

Model accuracy

C.

Access controls

D.

Data storage

Buy Now
Questions 33

Which of the following should an auditor reference when reviewing a company ' s human resources AI systems for legal non-compliance?

Options:

A.

Organization for Economic Cooperation and Development (OECD) standard

B.

National Institute of Standards and Technology (NIST) AI Risk Management Framework (RMF)

C.

European Union (EU) AI Act

D.

International Organization for Standardization (ISO)

Buy Now
Questions 34

Which of the following is the most impactful security risk associated with the use of a generative AI chatbot?

Options:

A.

Overly permissive access

B.

Data leakage

C.

Weak encryption

D.

Model validation

Buy Now
Questions 35

An AI security administrator receives an inquiry about an unusually high monthly bill from the AI solution provider. The administrator thinks the majority of staff might be using the most powerful model available.

Which of the following AI measures should the administrator implement to lower costs?

Options:

A.

Storage monitoring

B.

Modality types

C.

Prompt firewalls

D.

Token limits

Buy Now
Questions 36

A global security operations center (SOC) wants to adapt and leverage the strength of AI in order to enhance its security operations.

Which of the following is the best way to enhance the global SOC functions?

Options:

A.

Generate code and execute in production to help save time.

B.

Enable a personal assistant that can act in the global SOC with no human intervention.

C.

Use open-source models in production to help the efficiency of threat detection and threat analysis.

D.

Summarize alerts to easily gain insights on the environment.

Buy Now
Questions 37

After the deployment of an AI system, an organization is unable to identify who approved the system and the method of validation. Which of the following governance failures occurred?

Options:

A.

Absence of a completed threat model

B.

Absence of an audit trail

C.

Absence of blueprint controls

D.

Absence of organizational policies

Buy Now
Questions 38

A management team is concerned about an unexpected cost increase for a public-facing AI chatbot.

Which of the following should a security administrator examine first to determine the root cause?

Options:

A.

Firewall logs

B.

Web application firewall (WAF) rules

C.

Vector database input/output operations per second performance

D.

Model token usage

Buy Now
Questions 39

A developer is proposing a new AI application for human resources systems. Which of the following are the most important considerations?

Options:

A.

Geniality and appeal

B.

Privacy and security

C.

Graphics and design

D.

Brevity and summarization

Buy Now
Questions 40

An IT company implements an adaptable chatbot that learns from user prompts. Based on the conversation shown — where User 2 injected false information about a company acquisition that caused the chatbot to give incorrect responses to User 3 — which of the following compensating controls should an administrator implement to mitigate the issue?

Options:

A.

Data encryption

B.

Rate-limiting application programming interfaces (APIs)

C.

Transfer learning

D.

Guardrails

Buy Now
Questions 41

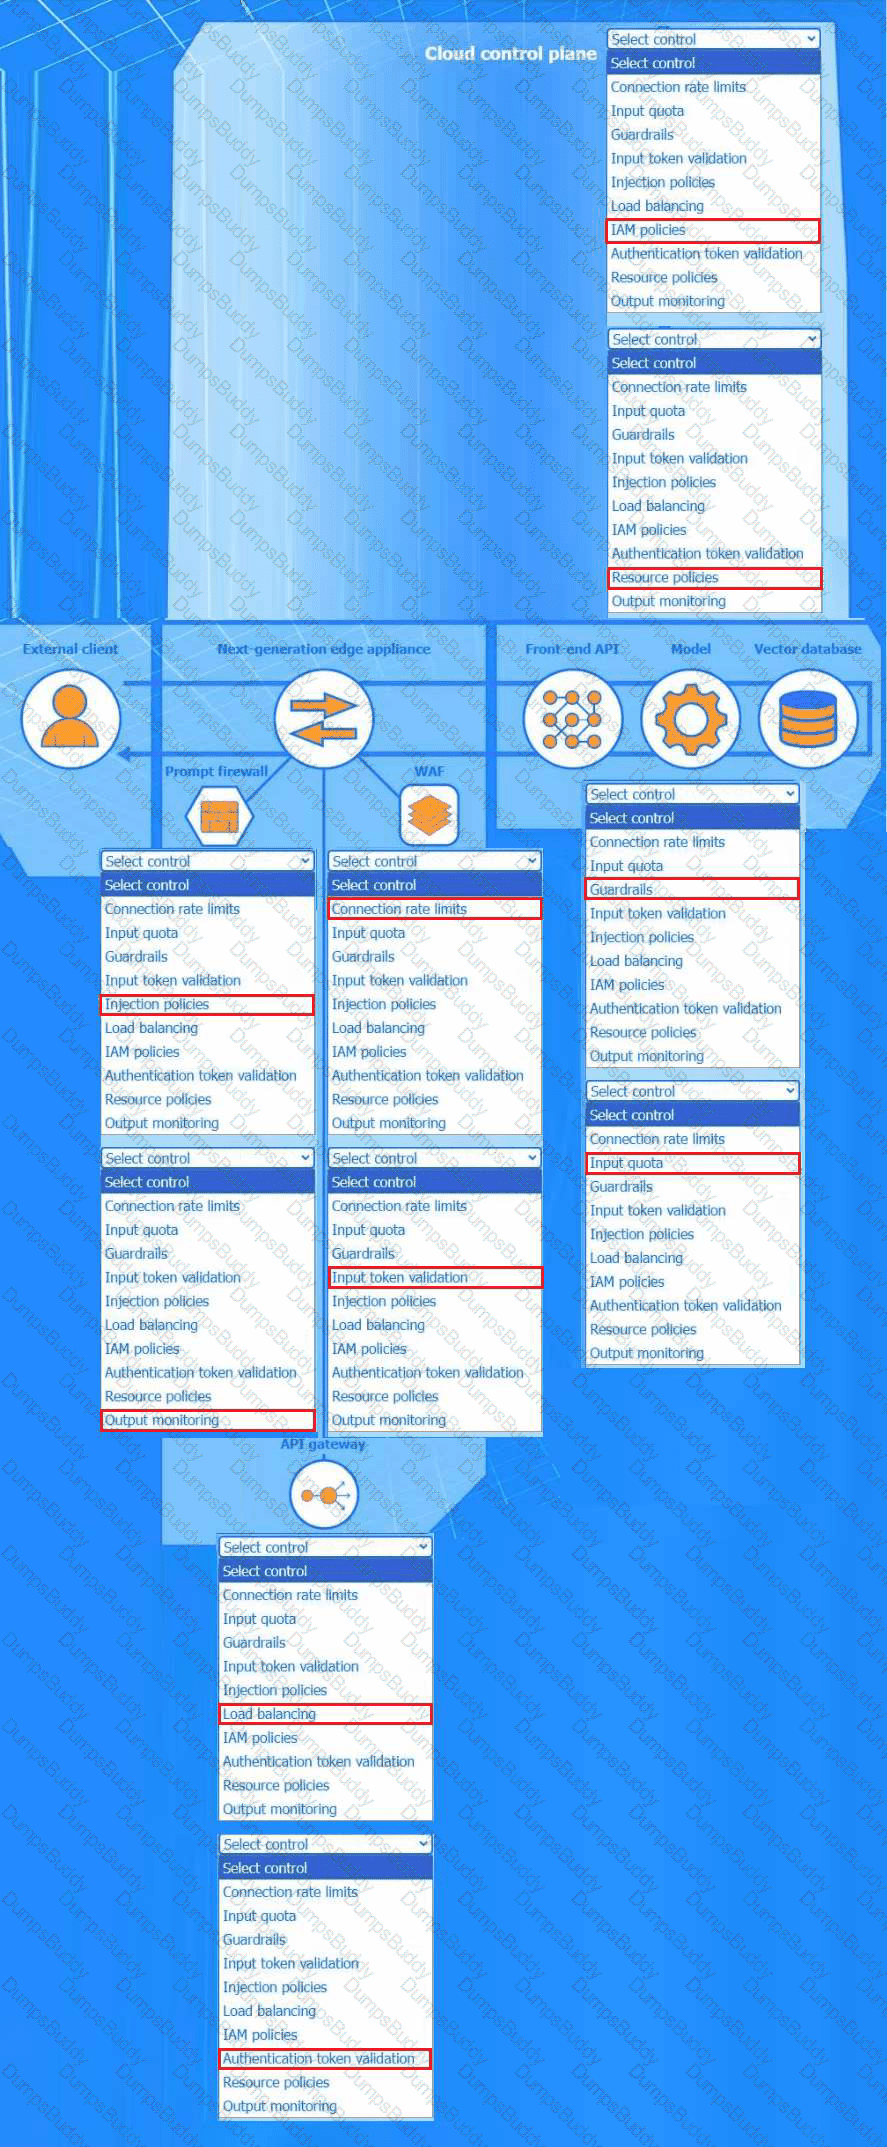
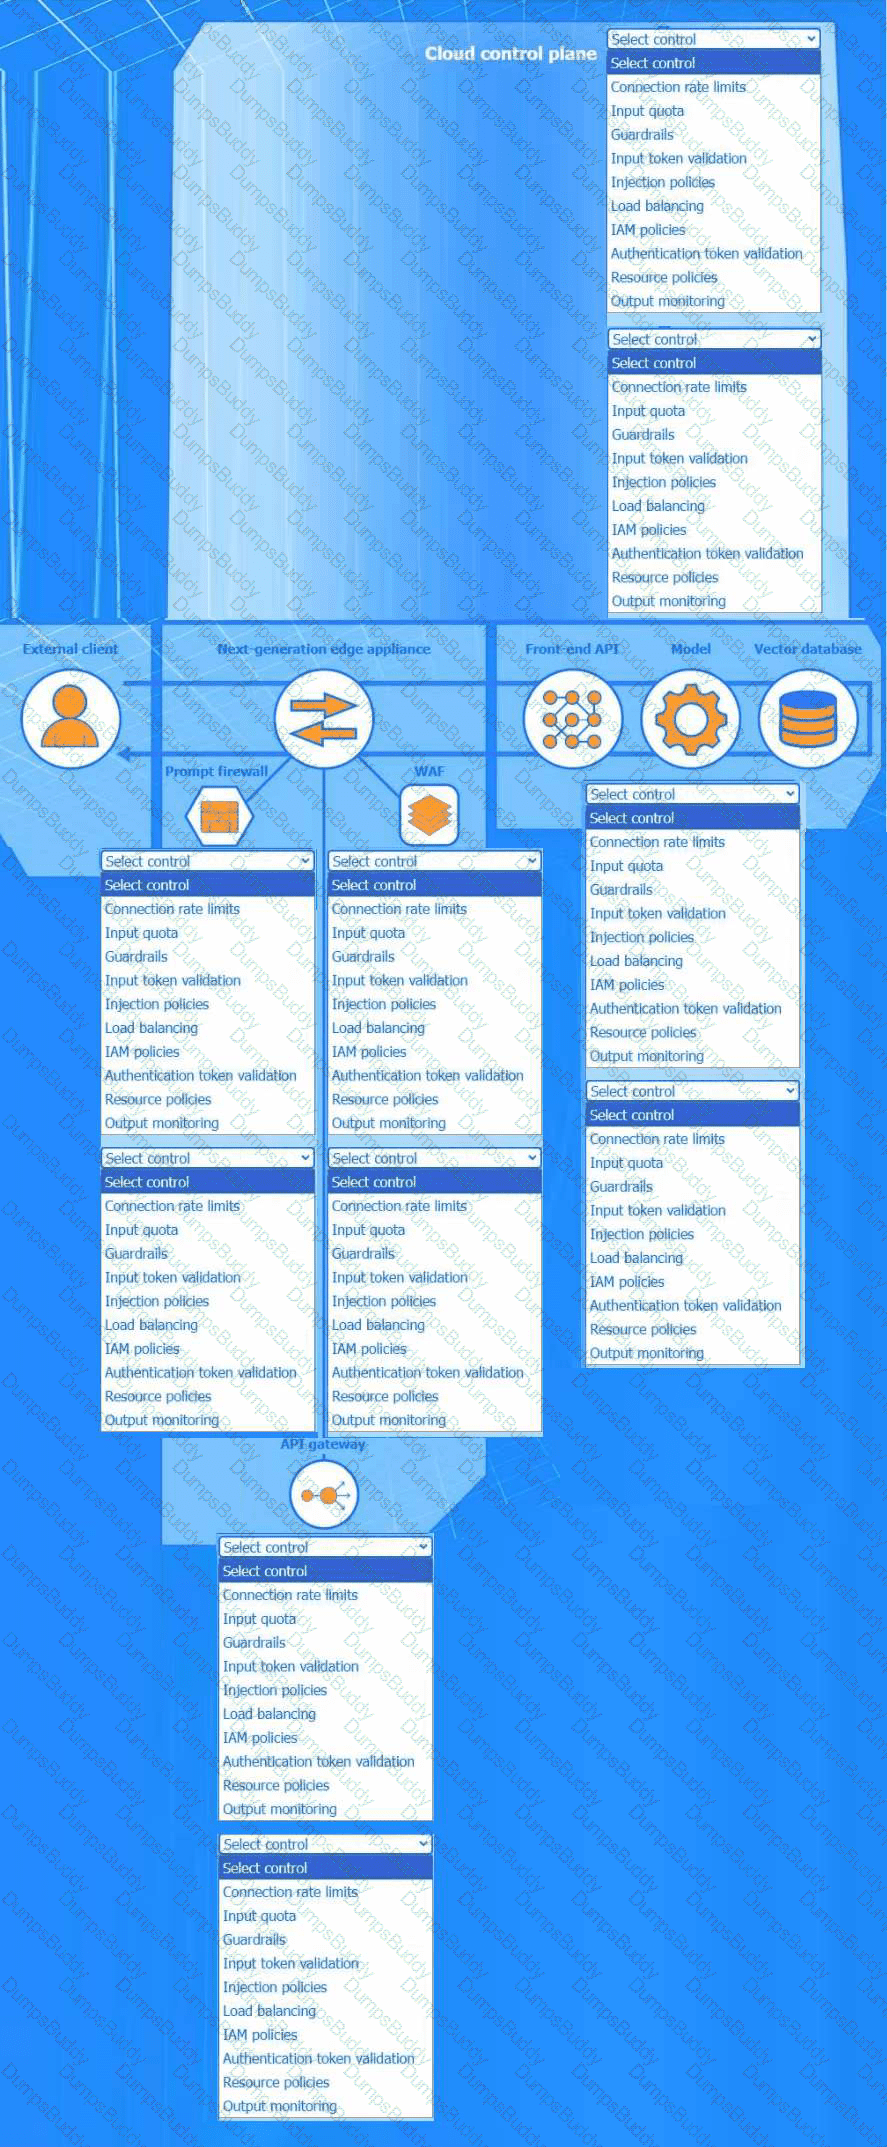
Instructions: Use the drop-down menus to define two appropriate security controls for each component of the AI system. Each control may be used only once.

An engineer is deploying a new AI system and wants to integrate it into the core system through an API.
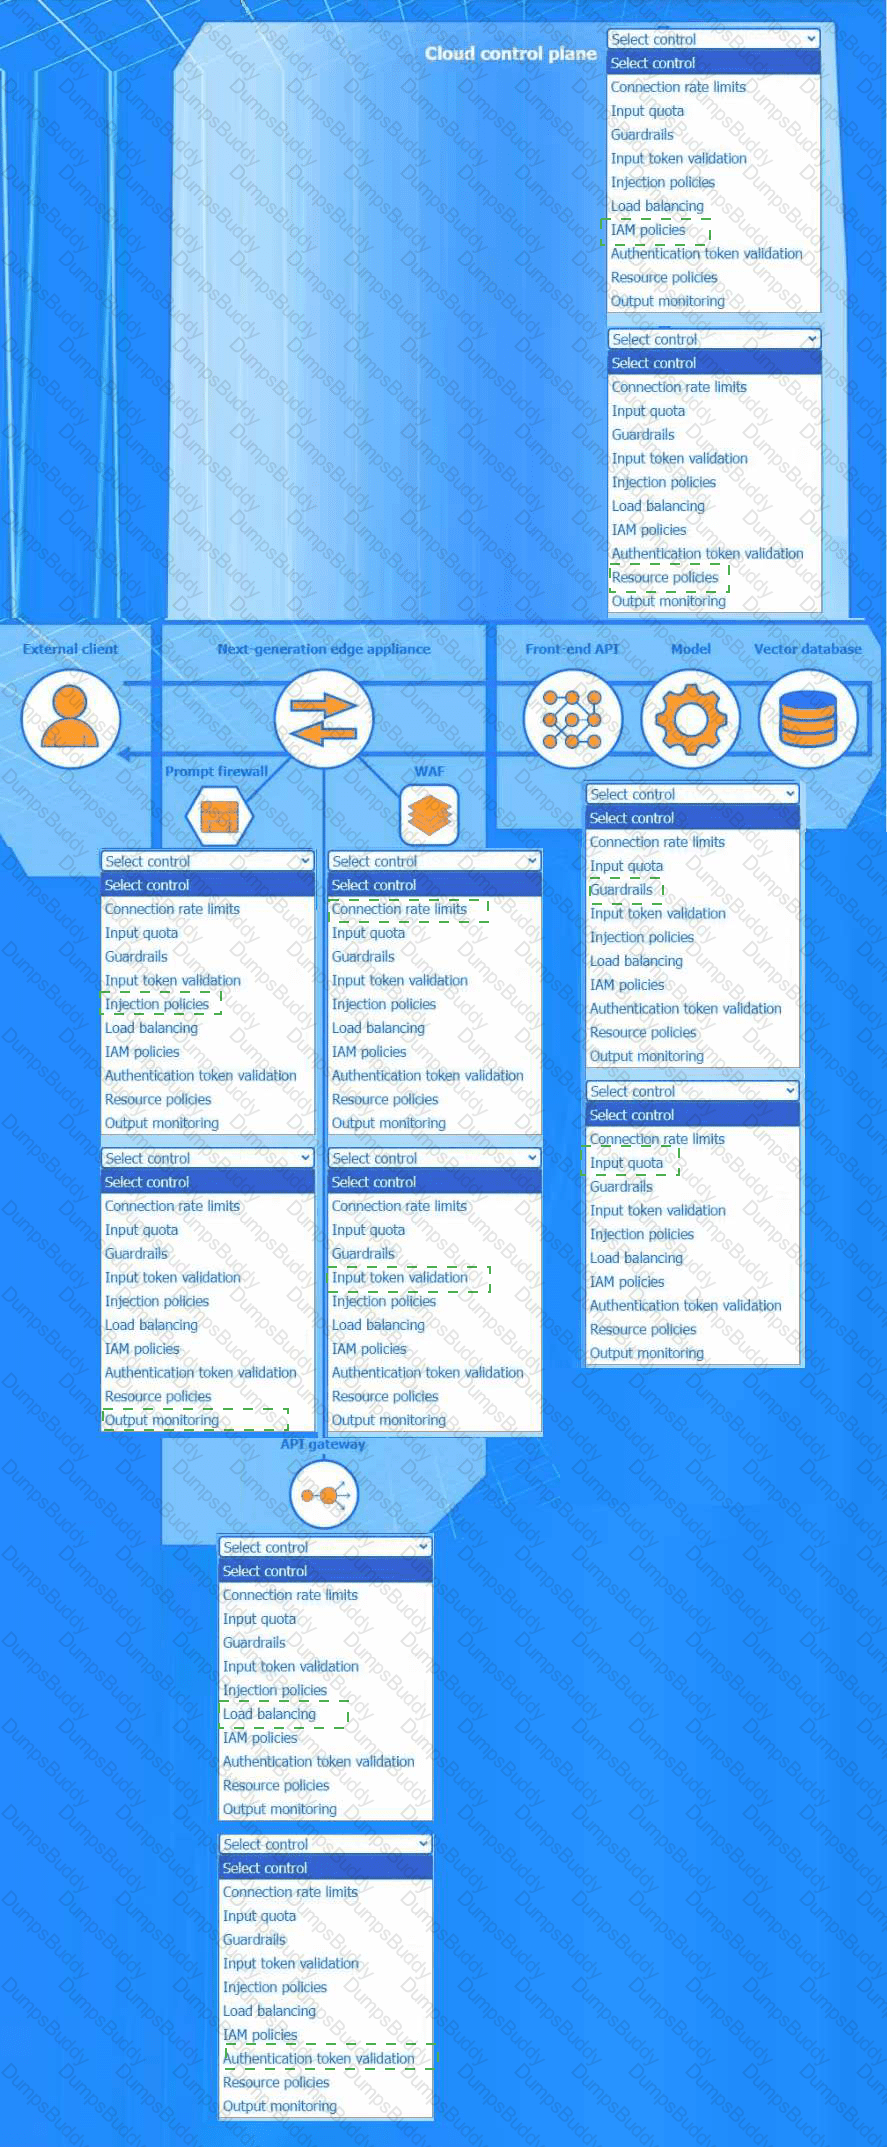
CY0-001 Question 41

Options:

Buy Now
Questions 42

Which of the following explains the reason a cybersecurity analyst prefers a machine learning (ML) model over a statistical model for attack classification?

Options:

A.

The ability to learn complex problems and adapt to new information

B.

A simplified development pipeline and deployment process

C.

Improved performance with a small data set and high durability

D.

Large community support and availability of global experts

Buy Now
Questions 43

For which of the following situations would a human-in-the-loop be most recommended?

Options:

A.

A large language model (LLM) that summarizes large blocks of text

B.

A generative model that creates graphics for websites

C.

A chatbot that provides answers based on frequently asked questions

D.

Agentic AI that automates system patching for an organization

Buy Now
Questions 44

Which of the following improves the observability and auditing of an AI system?

Options:

A.

Redeploying the model

B.

Using manual detection

C.

Implementing machine learning operations (MLOps)

D.

Using anomaly detections

Buy Now
Questions 45

A security engineer needs to monitor an AI-based system for runtime operations. The engineer is mostly concerned about the visibility of internal activity.

Which of the following is the most appropriate monitoring solution?

Options:

A.

Deploying a security information and event management (SIEM) tool

B.

Implementing a web application firewall (WAF) with header logging

C.

Relying on vendor model controls and monitoring prompt inputs

D.

Enabling stack call and debugging level traces at the function level

Buy Now
Questions 46

Which of the following attacks would be the best to automate with AI during dynamic application software testing (DAST)?

Options:

A.

Distributed denial-of-service (DDoS)

B.

Data poisoning

C.

Payload creation

D.

Threat modeling

Buy Now
Questions 47

A healthcare company deploys an AI chatbot that implements retrieval-augmented generation (RAG) using the company ' s historical data set. The chatbot output contains patient information.

Which of the following is the most effective technique to mitigate this vulnerability?

Options:

A.

Masking

B.

Classification

C.

Minimization

D.

Normalization

Buy Now
Exam Code: CY0-001
Exam Name: CompTIA SecAI+ v1 Exam
Last Update: Oct 13, 2026
Questions: 159

PDF + Testing Engine

$140

Testing Engine

$105

PDF (Q&A)

$90