CS0-004 CompTIA Cybersecurity Analyst CySA+ V4 (New Version) Questions and Answers
Which of the following is the most difficult for threat actors to change according to the Pyramid of Pain model?
A security operations center (SOC) analyst investigates the results of a password spray test conducted by the vulnerability management team.
The analyst must:
Identify Linux systems that have successful and unsuccessful logins with username "User1".
Create an output report named "linux-events" of all the events to a flat file.
The analyst issues the following console command:
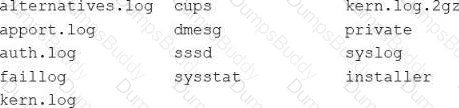
ls /var/log/
The shortened output of the command is below:
Which of the following commands should the analyst use to meet the report output requirements?
A security team reviews a penetration testing report of a web application that contains multiple cross-site scripting (XSS) and Structured Query Language injection (SQLi) vulnerabilities.
Which of the following is most likely causing these to occur?
A security analyst receives a notice about a possible data breach. The report identifies unapproved, current access dates for files found in the following personnel archives:
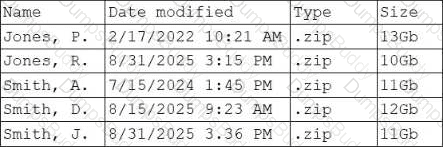
Which of the following actions should the analyst take first?
A security analyst responds to an alert regarding identity and access management activity within the cloud environment. The attacker is currently trying to gain access from one isolated cloud subscription to another via a compromised user role.
Which of the following aspects of the MITRE ATT & CK framework is the attacker trying to perform?
A security operations center analyst receives an alert from the security information and event management system. The analyst quickly reviews the alert and sees a workstation infected with malware. The analyst then uses the endpoint detection and response tool to isolate the workstation from the network.
Which of the following best describes the steps that occurred in this scenario?
A security architect reviews a report from a third-party incident response consultant and observes the following:
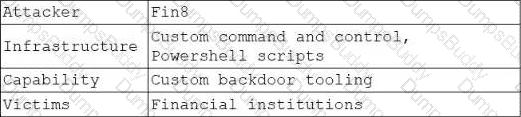
Which of the following frameworks did the consultant use to perform analysis?
An analyst receives the following output:
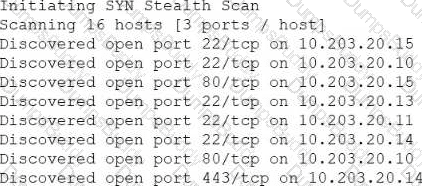
Which of the following is the correct number of discovered systems that are allowing unencrypted traffic?
A public threat intelligence report includes indicators of compromise (IoCs) for threat actors. The threat actors are exploiting a zero-day vulnerability that the vendor has not fixed.
Which of the following techniques should be used until a patch is available?
Which of the following should a cybersecurity analyst utilize when a notification is inaccurate?
A new security operations center (SOC) manager joins a team that struggles to meet service-level agreements (SLAs). The alert backlog continues to increase daily.
Which of the following will the manager most likely need to do?
An analyst reviews the following system logs from a recent breach attempt:
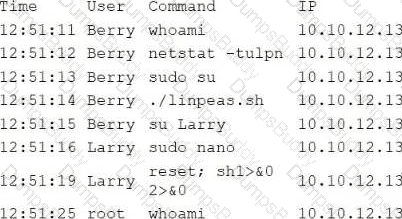
Which of the following techniques did the attacker attempt to use?
A server was recently compromised. A security analyst needs to collect artifacts for further analysis before disconnecting the server from the network.
Which of the following artifacts should the analyst collect first?
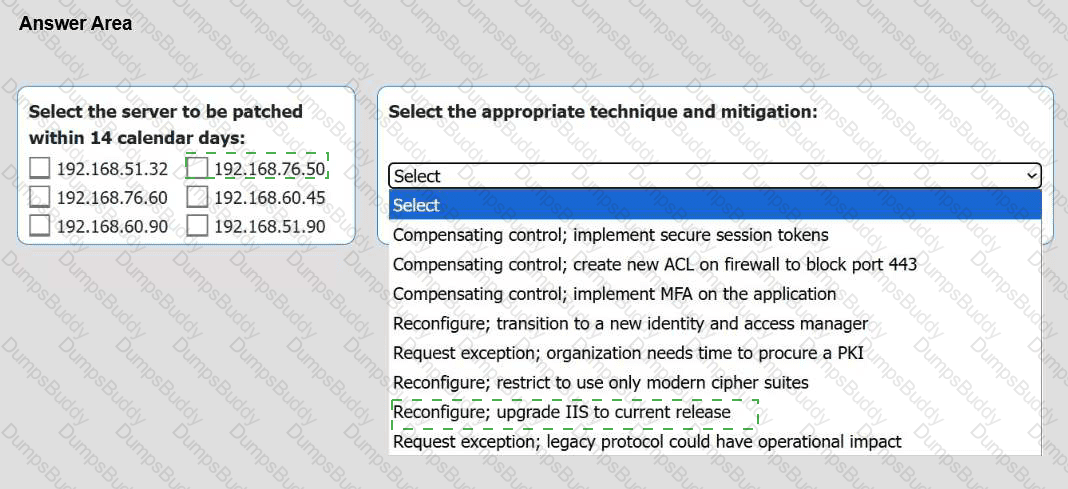
A systems administrator is reviewing the output of a vulnerability scan.
INSTRUCTIONS -
Review the information in each tab.
Based on the organization’s environment architecture and remediation standards, select the server to be patched within 14 days and select the appropriate technique and mitigation.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
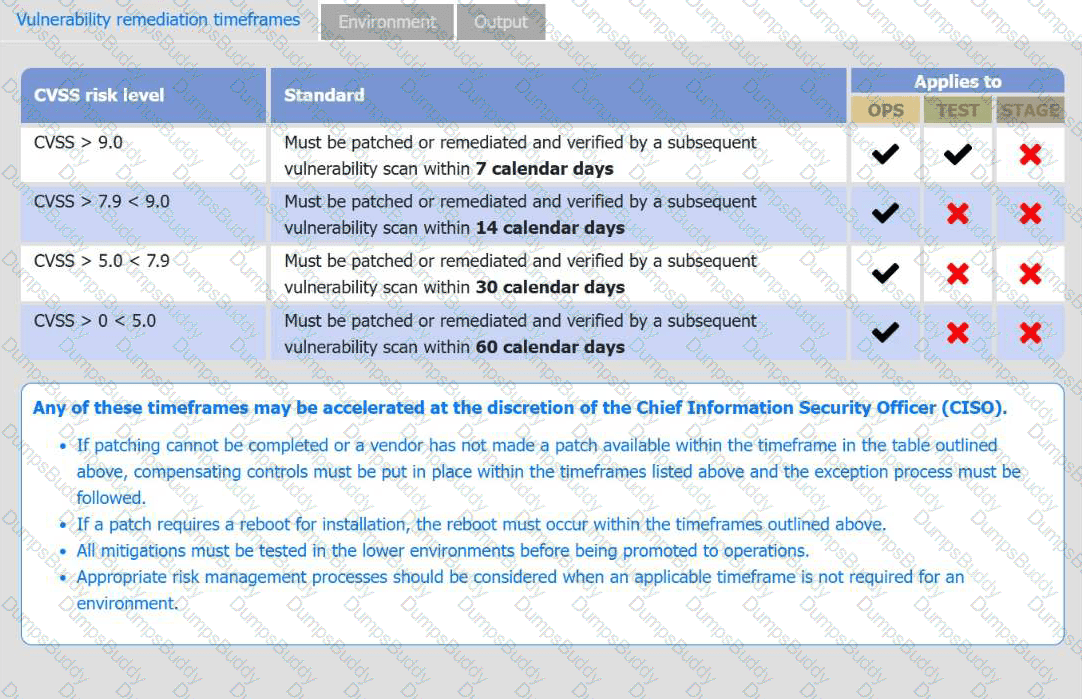
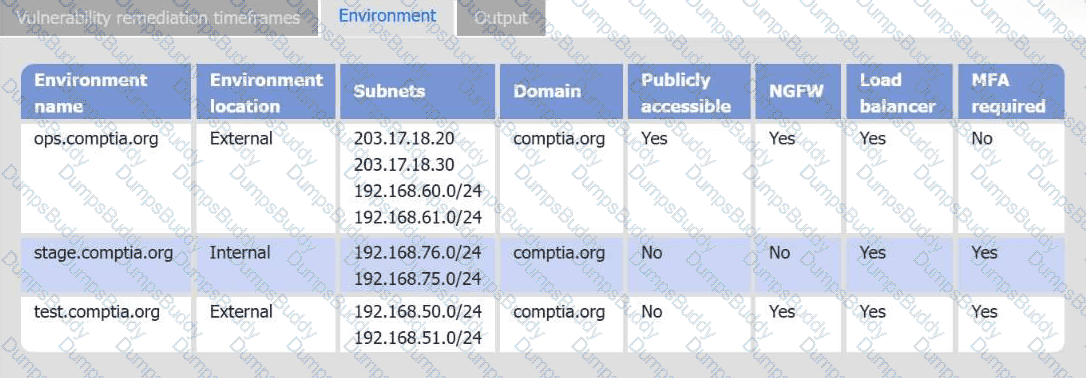
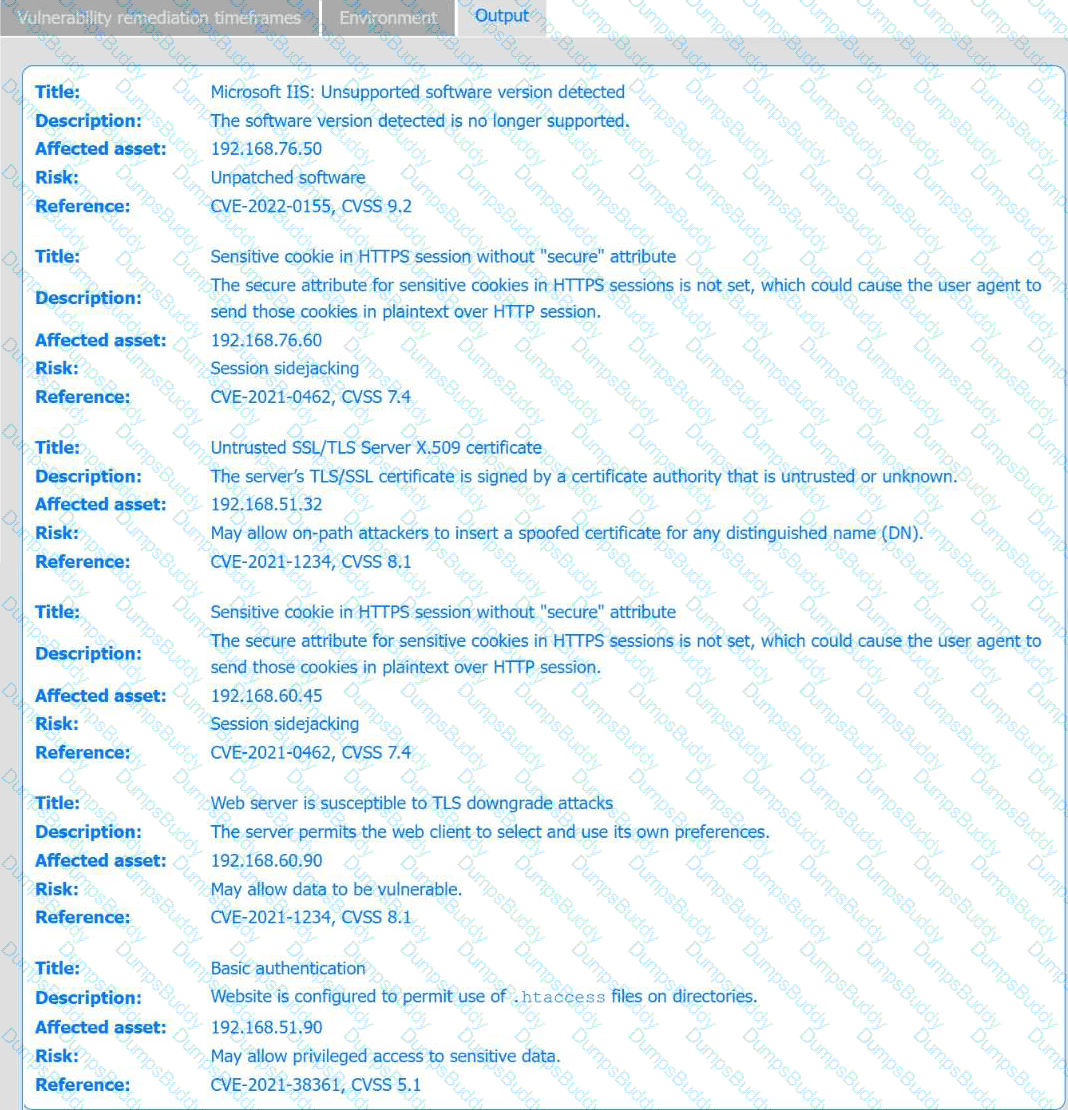
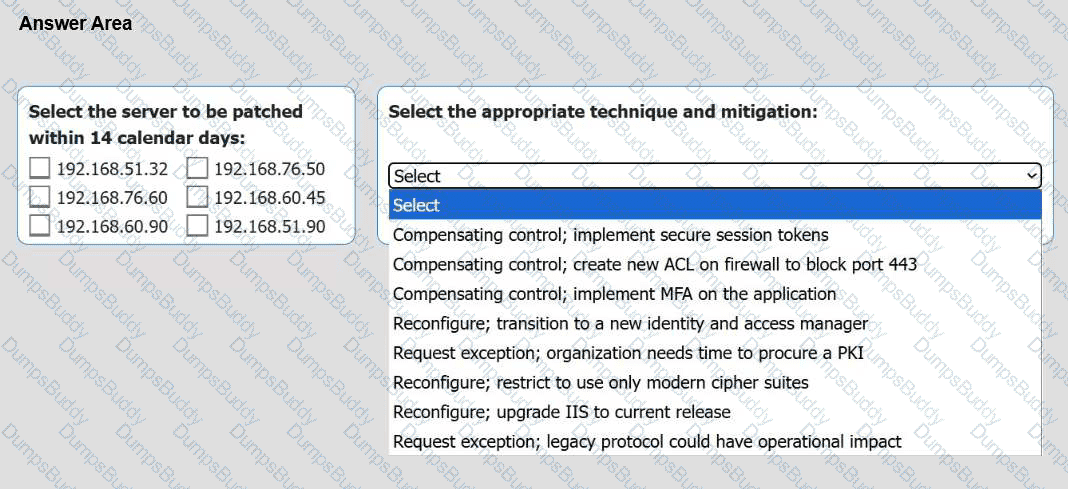
The Chief Information Security Officer wants to improve internal security measures by continuously validating and verifying access to the production environment.
Which of the following concepts best describes this practice?
A vendor releases details of a new vulnerability. When an analyst reviews the scheduled scans, no vulnerabilities are identified. The vulnerability is only discovered after a configuration change.
Which of the following scan types did the analyst configure?
Which of the following best explains why sensitive data should be encrypted at rest on laptops?
A security analyst runs an Nmap scan against a host with multiple open ports using the following command:
nmap 10.10.10.1 -p-
The following output is obtained after the scan:
Starting Nmap 7.95 ( https://nmap.org ) at 2025-07-15 15:55 UTC
Note: Host seems down.
Nmap done: 1 IP address (0 hosts up) scanned in 3.16 seconds
Which of the following is the most accurate way to scan the target IP for open ports?
Before merging with a software company, the acquiring company's legal team requires a detailed software scan to determine if all code base is using open-source or paid licensed libraries. The vulnerability management analyst needs to provide this report.
Which of the following scan methods will best meet this requirement?
Which of the following contains stakeholder contact information for incident response reporting?
An incident response team identifies a malicious uniform resource locator (URL) associated with a required business process and performs the following activities:
• Access to the URL has been restricted only to the necessary users through firewall rules and Cloud Security Group rules.
• Additional monitoring has been enabled for traffic related to that site and the allowed users.
• All application servers that need to access that site have been patched with the latest security and software updates.
• Application owners have been notified of the severity and need to remediate this reported issue.
Which of the following best describes the overall mitigation the security team is performing?
PDF + Testing Engine
Testing Engine
PDF (Q&A)