Halloween Sale Special 75% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: budy75

350-701 Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0) Questions and Answers

Questions 4

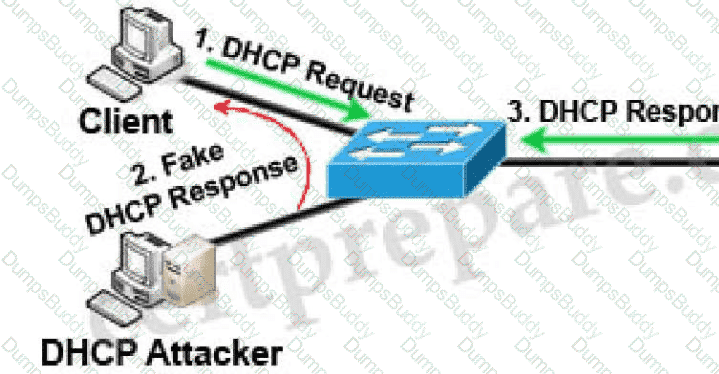
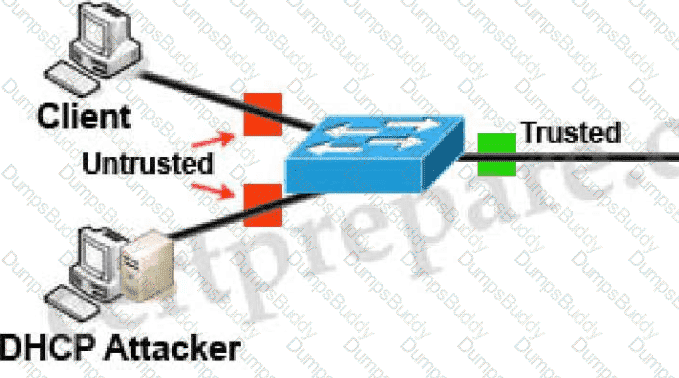
An administrator is configuring a DHCP server to better secure their environment. They need to be able to ratelimit the traffic and ensure that legitimate requests are not dropped. How would this be accomplished?
Options:

A.

Set a trusted interface for the DHCP server

B.

Set the DHCP snooping bit to 1

C.

Add entries in the DHCP snooping database

D.

Enable ARP inspection for the required VLAN

Buy Now
Questions 5

What is a difference between a DoS attack and a DDoS attack?

Options:

A.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where multiple systems target a single system with a DoS attack

B.

A DoS attack is where a computer is used to flood a server with TCP and UDP packets whereas a DDoS attack is where a computer is used to flood multiple servers that are distributed over a LAN

C.

A DoS attack is where a computer is used to flood a server with UDP packets whereas a DDoS attack is where a computer is used to flood a server with TCP packets

D.

A DoS attack is where a computer is used to flood a server with TCP packets whereas a DDoS attack is where a computer is used to flood a server with UDP packets

Buy Now
Questions 6

What is the difference between EPP and EDR?

Options:

A.

EPP focuses primarily on threats that have evaded front-line defenses that entered the environment.

B.

Having an EPP solution allows an engineer to detect, investigate, and remediate modern threats.

C.

EDR focuses solely on prevention at the perimeter.

D.

Having an EDR solution gives an engineer the capability to flag offending files at the first sign of malicious behavior.

Buy Now
Questions 7

In which cloud services model is the customer responsible for scanning for and mitigation of application vulnerabilities?

Options:

A.

PaaS

B.

VMaaS

C.

IaaS

D.

SaaS

Buy Now
Questions 8

An organization deploys multiple Cisco FTD appliances and wants to manage them using one centralized

solution. The organization does not have a local VM but does have existing Cisco ASAs that must migrate over

to Cisco FTDs. Which solution meets the needs of the organization?

Options:

A.

Cisco FMC

B.

CSM

C.

Cisco FDM

D.

CDO

Buy Now
Questions 9

Which CLI command is used to register a Cisco FirePower sensor to Firepower Management Center?

Options:

A.

configure system add < host > < key >

B.

configure manager < key > add host

C.

configure manager delete

D.

configure manager add < host > < key

Buy Now
Questions 10

Which attack type attempts to shut down a machine or network so that users are not able to access it?

Options:

A.

smurf

B.

bluesnarfing

C.

MAC spoofing

D.

IP spoofing

Buy Now
Questions 11

A network engineer must enable DHCP snooping on the corporate switches only for VLAN 2. Management requires DHCP traffic from unauthorized servers to be dropped. DHCP snooping is already enabled globally, and the uplink interface toward the authorized DHCP server is already trusted. Which configuration command must be applied to meet the requirement?

Options:

A.

ip dhcp snooping trust vlan 2

B.

ip dhcp relay information trusted vlan 2

C.

ip dhcp snooping information option vlan 2

D.

ip dhcp snooping vlan 2

Buy Now
Questions 12

Which two conditions are prerequisites for stateful failover for IPsec? (Choose two)

Options:

A.

Only the IKE configuration that is set up on the active device must be duplicated on the standby device; theIPsec configuration is copied automatically

B.

The active and standby devices can run different versions of the Cisco IOS software but must be the sametype of device.

C.

The IPsec configuration that is set up on the active device must be duplicated on the standby device

D.

Only the IPsec configuration that is set up on the active device must be duplicated on the standby device;the IKE configuration is copied automatically.

E.

The active and standby devices must run the same version of the Cisco IOS software and must be thesame type of device

Buy Now
Questions 13

What is a key feature of the Bring Your Own Device (BYOD) capability in Cisco ISE?

Options:

A.

Provide temporary Internet access for the personal devices of guest users.

B.

Assess the security posture of personal devices before network access is allowed.

C.

Fully manage network devices based on their characteristics before access is allowed.

D.

Encrypt endpoint data according to predefined security policies.

Buy Now
Questions 14

Which technology must De used to Implement secure VPN connectivity among company branches over a private IP cloud with any-to-any scalable connectivity?

Options:

A.

GET VPN

B.

IPsec DVTI

C.

DMVPN

D.

FlexVPN

Buy Now
Questions 15

Which interface mode does a Cisco Secure IPS device use to block suspicious traffic?

Options:

A.

Passive

B.

Inline

C.

Promiscuous

D.

Active

Buy Now
Questions 16

When a Cisco Secure Web Appliance checks a web request, what occurs if it is unable to match a user-defined policy?

Options:

A.

It applies the next identification profile policy.

B.

It applies the advanced policy.

C.

It applies the global policy.

D.

It blocks the request.

Buy Now
Questions 17

Which Cisco Umbrella package supports selective proxy for Inspection of traffic from risky domains?

Options:

A.

SIG Advantage

B.

DNS Security Essentials

C.

SIG Essentials

D.

DNS Security Advantage

Buy Now
Questions 18

Drag and drop the features of Cisco ASA with Firepower from the left onto the benefits on the right.
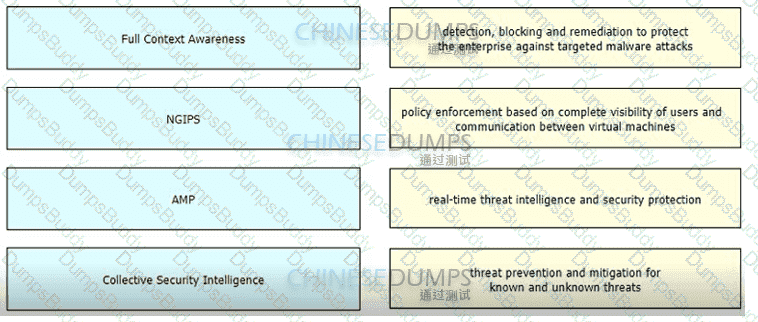
350-701 Question 18

Options:

Buy Now
Questions 19

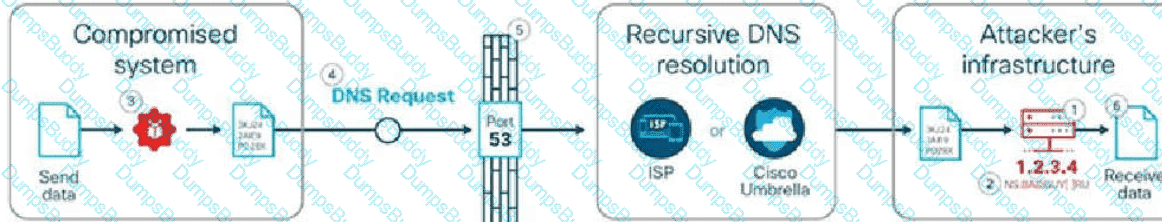
How does DNS Tunneling exfiltrate data?

Options:

A.

An attacker registers a domain that a client connects to based on DNS records and sends malware throughthat connection.

B.

An attacker opens a reverse DNS shell to get into the client’s system and install malware on it.

C.

An attacker uses a non-standard DNS port to gain access to the organization’s DNS servers in order topoison the resolutions.

D.

An attacker sends an email to the target with hidden DNS resolvers in it to redirect them to a maliciousdomain.

Buy Now
Questions 20

When planning a VPN deployment, for which reason does an engineer opt for an active/active FlexVPN

configuration as opposed to DMVPN?

Options:

A.

Multiple routers or VRFs are required.

B.

Traffic is distributed statically by default.

C.

Floating static routes are required.

D.

HSRP is used for faliover.

Buy Now
Questions 21

What are two functions of TAXII in threat intelligence sharing? (Choose two.)

Options:

A.

determines the " what " of threat intelligence

B.

Supports STIX information

C.

allows users to describe threat motivations and abilities

D.

exchanges trusted anomaly intelligence information

E.

determines how threat intelligence information is relayed

Buy Now
Questions 22

A company identified a phishing vulnerability during a pentest What are two ways the company can protect employees from the attack? (Choose two.)

Options:

A.

using Cisco Umbrella

B.

using Cisco ESA

C.

using Cisco FTD

D.

using an inline IPS/IDS in the network

E.

using Cisco ISE

Buy Now
Questions 23

Which IPS engine detects ARP spoofing?

Options:

A.

Atomic ARP Engine

B.

Service Generic Engine

C.

ARP Inspection Engine

D.

AIC Engine

Buy Now
Questions 24

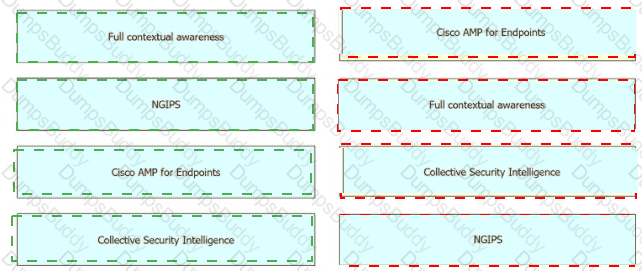
Drag and drop the security solutions from the left onto the benefits they provide on the right.
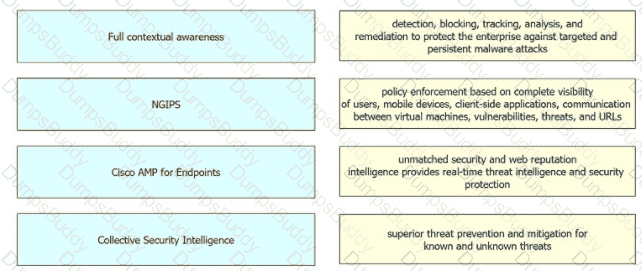
350-701 Question 24

Options:

Buy Now
Questions 25

An engineer is implementing Cisco CES in an existing Microsoft Office 365 environment and must route inbound email to Cisco CE.. record must be modified to accomplish this task?

Options:

A.

CNAME

B.

MX

C.

SPF

D.

DKIM

Buy Now
Questions 26

Which Cisco AMP file disposition valid?

Options:

A.

pristine

B.

malware

C.

dirty

D.

non malicious

Buy Now
Questions 27

What features does Cisco FTDv provide over ASAv?

Options:

A.

Cisco FTDv runs on VMWare while ASAv does not

B.

Cisco FTDv provides 1GB of firewall throughput while Cisco ASAv does not

C.

Cisco FTDv runs on AWS while ASAv does not

D.

Cisco FTDv supports URL filtering while ASAv does not

Buy Now
Questions 28

What is a difference between Cisco AMP for Endpoints and Cisco Umbrella?

Options:

A.

Cisco AMP for Endpoints is a cloud-based service, and Cisco Umbrella is not.

B.

Cisco AMP for Endpoints prevents connections to malicious destinations, and C malware.

C.

Cisco AMP for Endpoints automatically researches indicators of compromise ..

D.

Cisco AMP for Endpoints prevents, detects, and responds to attacks before and against Internet threats.

Buy Now
Questions 29

What does the Cloudlock Apps Firewall do to mitigate security concerns from an application perspective?

Options:

A.

It allows the administrator to quarantine malicious files so that the application can function, just notmaliciously.

B.

It discovers and controls cloud apps that are connected to a company’s corporate environment.

C.

It deletes any application that does not belong in the network.

D.

It sends the application information to an administrator to act on.

Buy Now
Questions 30

An engineer is configuring web filtering for a network using Cisco Umbrella Secure Internet Gateway.

The requirement is that all traffic needs to be filtered. Using the SSL decryption feature, which type of

certificate should be presented to the end-user to accomplish this goal?

Options:

A.

third-party

B.

self-signed

C.

organization owned root

D.

SubCA

Buy Now
Questions 31

A group of hospitals is collaborating to transition from an on-premises infrastructure to a cloud solution. The solution must be cost-effective, flexible, scalable, and support large volumes of data traffic. Each hospital has its own rules and policies that require direct control over its processes. Sensitive data, including patient records, must remain on-premises. Which type of cloud must be used?

Options:

A.

Federated

B.

Private

C.

Public

D.

Hybrid

Buy Now
Questions 32

What is the purpose of joining Cisco WSAs to an appliance group?

Options:

A.

All WSAs in the group can view file analysis results.

B.

The group supports improved redundancy

C.

It supports cluster operations to expedite the malware analysis process.

D.

It simplifies the task of patching multiple appliances.

Buy Now
Questions 33

What are two ways a network administrator transparently identifies users using Active Directory on the Cisco WSA? (Choose two.)

Options:

A.

Create an LDAP authentication realm and disable transparent user identification.

B.

Create NTLM or Kerberos authentication realm and enable transparent user identification.

C.

Deploy a separate Active Directory agent such as Cisco Context Directory Agent.

D.

The eDirectory client must be installed on each client workstation.

E.

Deploy a separate eDirectory server; the dent IP address is recorded in this server.

Buy Now
Questions 34

Which solution offers automated blocking of known threats and visibility into zero-day attack behavior, with the ability to respond directly from the console?

Options:

A.

EPP solution with an HIDS integration

B.

Cloud-native antivirus with offline update support

C.

EDR with behavioral analytics and remote containment

D.

Secure Email Gateway with phishing sandboxing

Buy Now
Questions 35

A web hosting company must upgrade its older, unsupported on-premises servers. The company wants a cloud solution in which the cloud provider is responsible for:

Server patching

Application maintenance

Data center security

Disaster recovery

Which type of cloud meets the requirements?

Options:

A.

Hybrid

B.

IaaS

C.

SaaS

D.

PaaS

Buy Now
Questions 36

Which portion of the network do EPP solutions solely focus on and EDR solutions do not?

Options:

A.

server farm

B.

perimeter

C.

core

D.

East-West gateways

Buy Now
Questions 37

What Cisco command shows you the status of an 802.1X connection on interface gi0/1?

Options:

A.

show authorization status

B.

show authen sess int gi0/1

C.

show connection status gi0/1

D.

show ver gi0/1

Buy Now
Questions 38

What is the process In DevSecOps where all changes In the central code repository are merged and synchronized?

Options:

A.

CD

B.

EP

C.

CI

D.

QA

Buy Now
Questions 39

Which two descriptions of AES encryption are true? (Choose two)

Options:

A.

AES is less secure than 3DES.

B.

AES is more secure than 3DES.

C.

AES can use a 168-bit key for encryption.

D.

AES can use a 256-bit key for encryption.

E.

AES encrypts and decrypts a key three times in sequence.

Buy Now
Questions 40

Which DevSecOps practice helps reduce vulnerabilities introduced through external open-source components?

Options:

A.

Performing static routing configuration checks

B.

Conducting software composition analysis during builds

C.

Using dynamic routing between Kubernetes clusters

D.

Setting up round-robin DNS resolution for service discovery

Buy Now
Questions 41

Which compliance status is shown when a configured posture policy requirement is not met?

Options:

A.

compliant

B.

unknown

C.

authorized

D.

noncompliant

Buy Now
Questions 42

An engineer needs behavioral analysis to detect malicious activity on the hosts, and is configuring the

organization’s public cloud to send telemetry using the cloud provider’s mechanisms to a security device. Which

mechanism should the engineer configure to accomplish this goal?

Options:

A.

mirror port

B.

Flow

C.

NetFlow

D.

VPC flow logs

Buy Now
Questions 43

An engineer is configuring guest WLAN access using Cisco ISE and the Cisco WLC. Which action temporarily gives guest endpoints access dynamically while maintaining visibility into who or what is connecting?

Options:

A.

Modify the WLC configuration to require local WLC logins for the authentication prompts.

B.

Configure ISE and the WLC for guest redirection and services using a self-registered portal.

C.

Configure ISE and the WLC for guest redirection and services using a hotspot portal.

D.

Modify the WLC configuration to allow any endpoint to access an internet-only VLAN.

Buy Now
Questions 44

Due to a traffic storm on the network, two interfaces were error-disabled, and both interfaces sent SNMP traps.

Which two actions must be taken to ensure that interfaces are put back into service? (Choose two)

Options:

A.

Have Cisco Prime Infrastructure issue an SNMP set command to re-enable the ports after the preconfigured interval.

B.

Use EEM to have the ports return to service automatically in less than 300 seconds.

C.

Enter the shutdown and no shutdown commands on the interfaces.

D.

Enable the snmp-server enable traps command and wait 300 seconds

E.

Ensure that interfaces are configured with the error-disable detection and recovery feature

Buy Now
Questions 45

A company wants to enforce security policy using Cisco Secure Access Secure Internet Access. The design requirements are:

    Block adult-content and gambling categories for all users.

    Inspect file downloads for malware.

    Bypass TLS decryption for financial and healthcare domains because of compliance requirements.

    Allow the Marketing department to use social media while keeping file scanning active for downloads from those sites.

Which two configuration actions must the engineer perform in Cisco Secure Access to meet the requirements? (Choose two.)

Options:

A.

Configure a Marketing policy with higher precedence to allow social-networking sites, and apply a decryption-bypass list for financial and healthcare domains.

B.

Disable TLS decryption globally and rely on DNS-layer reputation to block adult-content and gambling sites.

C.

Use destination allow lists for financial and healthcare sites to prevent SSL inspection, with malware scanning enabled in full-inspection mode for all traffic.

D.

Create a global policy that blocks adult-content and gambling categories with TLS inspection enabled, and create a higher-precedence Marketing policy that allows social-networking sites.

E.

Implement one global policy that blocks adult-content and gambling categories, and add a web-application allow rule for social networking.

Buy Now
Questions 46

What are two benefits of using Cisco Duo as an MFA solution? (Choose two.)

Options:

A.

grants administrators a way to remotely wipe a lost or stolen device

B.

provides simple and streamlined login experience for multiple applications and users

C.

native integration that helps secure applications across multiple cloud platforms or on-premises environments

D.

encrypts data that is stored on endpoints

E.

allows for centralized management of endpoint device applications and configurations

Buy Now
Questions 47

What is the recommendation in a zero-trust model before granting access to corporate applications and

resources?

Options:

A.

to use multifactor authentication

B.

to use strong passwords

C.

to use a wired network, not wireless

D.

to disconnect from the network when inactive

Buy Now
Questions 48

After a recent breach, an organization determined that phishing was used to gain initial access to the network before regaining persistence. The information gained from the phishing attack was a result of users visiting known malicious websites. What must be done in order to prevent this from happening in the future?

Options:

A.

Modify an access policy

B.

Modify identification profiles

C.

Modify outbound malware scanning policies

D.

Modify web proxy settings

Buy Now
Questions 49

Why is it important to have a patching strategy for endpoints?

Options:

A.

to take advantage of new features released with patches

B.

so that functionality is increased on a faster scale when it is used

C.

so that known vulnerabilities are targeted and having a regular patch cycle reduces risks

D.

so that patching strategies can assist with disabling nonsecure protocols in applications

Buy Now
Questions 50

Which two services must remain as on-premises equipment when a hybrid email solution is deployed? (Choose two)

Options:

A.

DDoS

B.

antispam

C.

antivirus

D.

encryption

E.

DLP

Buy Now
Questions 51

What causes alert fatigue in Cisco XDR?

Options:

A.

Alerts lacking sufficient context to be accurate

B.

Reauthentication of an active endpoint during a vulnerability incident

C.

Notifications from too few devices in a data-breach event

D.

Automatic policy enforcement during a suspicious event

Buy Now
Questions 52

Which two methods are available in Cisco Secure Web Appliance to process client requests when configured in Transparent mode? (Choose two.)

Options:

A.

WCCP

B.

Browser settings

C.

WPAD

D.

PAC files

E.

PBR

Buy Now
Questions 53

What are two rootkit types? (Choose two)

Options:

A.

registry

B.

virtual

C.

bootloader

D.

user mode

E.

buffer mode

Buy Now
Questions 54

Which feature enforces continuous connectivity by preventing users from disconnecting the Cisco Secure Client tunnel?

Options:

A.

Always-On

B.

Smart Tunnel

C.

Path MTU Discovery

D.

Allow Local LAN Access

Buy Now
Questions 55

What is the purpose of threat intelligence in the Cisco Security Reference Architecture?

Options:

A.

To assist with threat monitoring and incident response

B.

To manage access control and authentication mechanisms

C.

To analyze network traffic and identify potential vulnerabilities

D.

To ensure compliance with industry regulations

Buy Now
Questions 56

Which two endpoint measures are used to minimize the chances of falling victim to phishing and social

engineering attacks? (Choose two)

Options:

A.

Patch for cross-site scripting.

B.

Perform backups to the private cloud.

C.

Protect against input validation and character escapes in the endpoint.

D.

Install a spam and virus email filter.

E.

Protect systems with an up-to-date antimalware program

Buy Now
Questions 57

What is the function of Cisco Cloudlock for data security?

Options:

A.

data loss prevention

B.

controls malicious cloud apps

C.

detects anomalies

D.

user and entity behavior analytics

Buy Now
Questions 58

Which threat intelligence standard contains malware hashes?

Options:

A.

advanced persistent threat

B.

open command and control

C.

structured threat information expression

D.

trusted automated exchange of indicator information

Buy Now
Questions 59

Which policy represents a shared set of features or parameters that define the aspects of a managed device that are likely to be similar to other managed devices in a deployment?

Options:

A.

Group Policy

B.

Access Control Policy

C.

Device Management Policy

D.

Platform Service Policy

Buy Now
Questions 60

Which technology provides a combination of endpoint protection endpoint detection, and response?

Options:

A.

Cisco AMP

B.

Cisco Talos

C.

Cisco Threat Grid

D.

Cisco Umbrella

Buy Now
Questions 61

Under which two circumstances is a CoA issued? (Choose two)

Options:

A.

A new authentication rule was added to the policy on the Policy Service node.

B.

An endpoint is deleted on the Identity Service Engine server.

C.

A new Identity Source Sequence is created and referenced in the authentication policy.

D.

An endpoint is profiled for the first time.

E.

A new Identity Service Engine server is added to the deployment with the Administration persona

Buy Now
Questions 62

An organization has a requirement to collect full metadata information about the traffic going through their AWS cloud services They want to use this information for behavior analytics and statistics Which two actions must be taken to implement this requirement? (Choose two.)

Options:

A.

Configure Cisco ACI to ingest AWS information.

B.

Configure Cisco Thousand Eyes to ingest AWS information.

C.

Send syslog from AWS to Cisco Stealthwatch Cloud.

D.

Send VPC Flow Logs to Cisco Stealthwatch Cloud.

E.

Configure Cisco Stealthwatch Cloud to ingest AWS information

Buy Now
Questions 63

A network engineer must distribute an operating system image to a network device and activate the image on that device by using the Cisco Catalyst Center API. Which two API requests perform the required operations? (Choose two.)

Options:

A.

POST /dna/intent/api/v1/image/distribution

B.

POST /dna/intent/api/v1/onboarding/pnp-device/import

C.

POST /dna/intent/api/v1/image/activation/device

D.

POST /dna/intent/api/v1/network/{site_id}

E.

POST /dna/intent/api/v1/template-programmer/project/{project_id}/template

Buy Now
Questions 64

What are two benefits of Flexible NetFlow records? (Choose two)

Options:

A.

They allow the user to configure flow information to perform customized traffic identification

B.

They provide attack prevention by dropping the traffic

C.

They provide accounting and billing enhancements

D.

They converge multiple accounting technologies into one accounting mechanism

E.

They provide monitoring of a wider range of IP packet information from Layer 2 to 4

Buy Now
Questions 65

What is a benefit of using Cisco Tetration?

Options:

A.

It collects telemetry data from servers and then uses software sensors to analyze flowinformation.

B.

It collects policy compliance data and process details.

C.

It collects enforcement data from servers and collects interpacket variation.

D.

It collects near-real time data from servers and inventories the software packages that exist onservers.

Buy Now
Questions 66

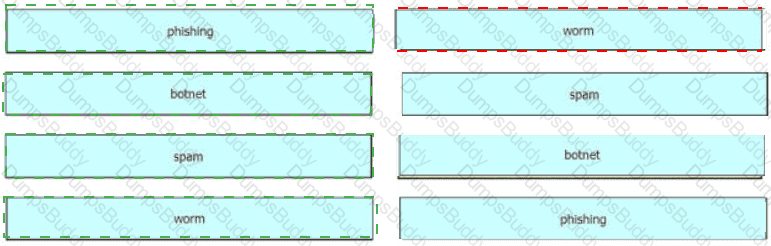
Drag and drop the common security threats from the left onto the definitions on the right.
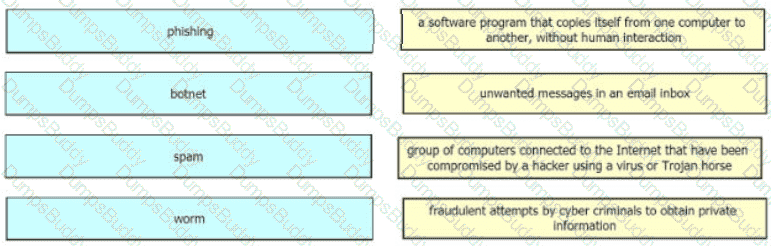
350-701 Question 66

Options:

Buy Now
Questions 67

When web policies are configured in Cisco Umbrella, what provides the ability to ensure that domains are blocked when they host malware, command and control, phishing, and more threats?

Options:

A.

Application Control

B.

Security Category Blocking

C.

Content Category Blocking

D.

File Analysis

Buy Now
Questions 68

Which Talos reputation center allows you to track the reputation of IP addresses for email and web traffic?

Options:

A.

IP Blacklist Center

B.

File Reputation Center

C.

AMP Reputation Center

D.

IP and Domain Reputation Center

Buy Now
Questions 69

For a given policy in Cisco Umbrella, how should a customer block website based on a custom list?

Options:

A.

by specifying blocked domains in me policy settings

B.

by specifying the websites in a custom blocked category

C.

by adding the websites to a blocked type destination list

D.

by adding the website IP addresses to the Cisco Umbrella blocklist

Buy Now
Questions 70

Which algorithm is an NGE hash function?

Options:

A.

HMAC

B.

SHA-1

C.

MD5

D.

SISHA-2

Buy Now
Questions 71

When choosing an algorithm to us, what should be considered about Diffie Hellman and RSA for key

establishment?

Options:

A.

RSA is an asymmetric key establishment algorithm intended to output symmetric keys

B.

RSA is a symmetric key establishment algorithm intended to output asymmetric keys

C.

DH is a symmetric key establishment algorithm intended to output asymmetric keys

D.

DH is an asymmetric key establishment algorithm intended to output symmetric keys

Buy Now
Questions 72

Which mitigation strategy should be used to protect against session hijacking attacks in a cloud environment?

Options:

A.

Implement input validation.

B.

Use secure cookies.

C.

Apply the principle of least privilege.

D.

Use anti-cross-site request forgery tokens.

Buy Now
Questions 73

What is a benefit of performing device compliance?

Options:

A.

Verification of the latest OS patches

B.

Device classification and authorization

C.

Providing multi-factor authentication

D.

Providing attribute-driven policies

Buy Now
Questions 74

What are two functionalities of northbound and southbound APIs within Cisco SDN architecture? (Choose two.)

Options:

A.

Southbound APIs are used to define how SDN controllers integrate with applications.

B.

Southbound interfaces utilize device configurations such as VLANs and IP addresses.

C.

Northbound APIs utilize RESTful API methods such as GET, POST, and DELETE.

D.

Southbound APIs utilize CLI, SNMP, and RESTCONF.

E.

Northbound interfaces utilize OpenFlow and OpFlex to integrate with network devices.

Buy Now
Questions 75

What are two workload security models? (Choose two.)

Options:

A.

SaaS

B.

PaaS

C.

off-premises

D.

on-premises

E.

IaaS

Buy Now
Questions 76

What is the role of Cisco Umbrella Roaming when it is installed on an endpoint?

Options:

A.

To protect the endpoint against malicious file transfers

B.

To ensure that assets are secure from malicious links on and off the corporate network

C.

To establish secure VPN connectivity to the corporate network

D.

To enforce posture compliance and mandatory software

Buy Now
Questions 77

An organization wants to reduce their attach surface for cloud applications. They want to understand application communications, detect abnormal application Behavior, and detect vulnerabilities within the applications. Which action accomplishes this task?

Options:

A.

Configure Cisco Secure Workload to detect anomalies and vulnerabilities.

B.

Use Cisco ISE to provide application visibility and restrict access to them.

C.

Implement Cisco Umbrella lo control the access each application is granted.

D.

Modify the Cisco Duo configuration to restrict access between applications.

Buy Now
Questions 78

What are two ways that Cisco Container Platform provides value to customers who utilize cloud service providers? (Choose two.)

Options:

A.

Allows developers to create code once and deploy to multiple clouds

B.

helps maintain source code for cloud deployments

C.

manages Docker containers

D.

manages Kubernetes clusters

E.

Creates complex tasks for managing code

Buy Now
Questions 79

What is the difference between deceptive phishing and spear phishing?

Options:

A.

Deceptive phishing is an attacked aimed at a specific user in the organization who holds a C-level role.

B.

A spear phishing campaign is aimed at a specific person versus a group of people.

C.

Spear phishing is when the attack is aimed at the C-level executives of an organization.

D.

Deceptive phishing hijacks and manipulates the DNS server of the victim and redirects the user to a false webpage.

Buy Now
Questions 80

Refer to the exhibit.

350-701 Question 80

An engineer is implementing a network access control solution. Users can authenticate against the RADIUS server using 802.1X, and now the engineer wants to configure a downloadable access control list on the switchport using Cisco ISE. Which command must be used next on the Cisco Catalyst switch to complete the requirement?

Options:

A.

ip access-group ACL-NAME out

B.

switchport mode access

C.

authentication order mab dot1x

D.

radius-server vsa send authentication

Buy Now
Questions 81

A security engineer must create a policy based on the reputation verdict of a file from a Cisco Secure Email Gateway. The file with an undetermined verdict must be dropped. Which action must the security engineer take to meet the requirement?

Options:

A.

Configure threshold settings for files with no score to be allowed.

B.

Set up a policy to automatically drop files with no reputation score.

C.

Implement a policy to disable file analysis.

D.

Create a policy to send a file to quarantine.

Buy Now
Questions 82

Which two services are provided by the Cisco Talos Incident Response group? (Choose two.)

Options:

A.

Security policy authorization

B.

Bug identification

C.

Automatic vulnerability remediation

D.

Threat hunting

E.

Cyber range training

Buy Now
Questions 83

A network administrator configures Dynamic ARP Inspection on a switch. After Dynamic ARP Inspection is applied, all users on that switch are unable to communicate with any destination. The network administrator checks the interface status of all interfaces, and there is no err-disabled interface. What is causing this problem?
Options:

A.

DHCP snooping has not been enabled on all VLANs.

B.

The ip arp inspection limit command is applied on all interfaces and is blocking the traffic of all users.

C.

Dynamic ARP Inspection has not been enabled on all VLANs

D.

The no ip arp inspection trust command is applied on all user host interfaces

Buy Now
Questions 84

How is DNS tunneling used to exfiltrate data out of a corporate network?

Options:

A.

It corrupts DNS servers by replacing the actual IP address with a rogue address to collect information or start other attacks.

B.

It encodes the payload with random characters that are broken into short strings and the DNS serverrebuilds the exfiltrated data.

C.

It redirects DNS requests to a malicious server used to steal user credentials, which allows further damageand theft on the network.

D.

It leverages the DNS server by permitting recursive lookups to spread the attack to other DNS servers.

Buy Now
Questions 85

Which Cisco solution integrates industry-leading artificial intelligence and machine learning analytics and an assurance database to review the security posture and maintain visibility of an organization’s cloud environment?

Options:

A.

Cisco CSR1000v

B.

Cisco Secure Workload

C.

Cisco DNA

D.

Cisco FTD

Buy Now
Questions 86

Which API is used for Content Security?

Options:

A.

NX-OS API

B.

IOS XR API

C.

OpenVuln API

D.

AsyncOS API

Buy Now
Questions 87

In which two customer environments is the Cisco Secure Web Appliance Virtual connector traffic direction method selected? (Choose two.)

Options:

A.

Customer needs to support roaming users.

B.

Customer does not own Cisco hardware and needs Transparent Redirection (WCCP).

C.

Customer owns ASA Appliance and Virtual Form Factor is required.

D.

Customer does not own Cisco hardware and needs Explicit Proxy.

E.

Customer owns ASA Appliance and SSL Tunneling is required.

Buy Now
Questions 88

Which two prevention techniques are used to mitigate SQL injection attacks? (Choose two)

Options:

A.

Check integer, float, or Boolean string parameters to ensure accurate values.

B.

Use prepared statements and parameterized queries.

C.

Secure the connection between the web and the app tier.

D.

Write SQL code instead of using object-relational mapping libraries.

E.

Block SQL code execution in the web application database login.

Buy Now
Questions 89

The main function of northbound APIs in the SDN architecture is to enable communication between which two areas of a network?
Options:

A.

SDN controller and the cloud

B.

management console and the SDN controller

C.

management console and the cloud

D.

SDN controller and the management solution

Buy Now
Questions 90

350-701 Question 90

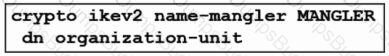
Refer to the exhibit. An engineer is implementing a certificate-based VPN. What is the result of the existing configuration?

Options:

A.

The OU of the IKEv2 peer certificate is encrypted when the OU is set to MANGLER.

B.

The OU of the IKEv2 peer certificate is used as the identity when matching an IKEv2 authorization policy.

C.

Only an IKEv2 peer that has an OU certificate attribute set to MANGLER establishes an IKEv2 SA successfully.

D.

The OU of the IKEv2 peer certificate is set to MANGLER.

Buy Now
Questions 91

What is a difference between SQL injection and buffer overflow?

Options:

A.

SQL injection is delivered by a web form, and buffer overflow bypasses all forms of user authentication entirely.

B.

SQL injection gives unauthorized access to a database, and buffer overflow executes arbitrary code and corrupts memory.

C.

SQL injection causes denial-of-service, and buffer overflow bypasses all forms of user authentication.

D.

SQL injection is a stack-based attack, and buffer overflow is a heap-based attack.

Buy Now
Questions 92

What is an advantage of network telemetry over SNMP pulls?

Options:

A.

accuracy

B.

encapsulation

C.

security

D.

scalability

Buy Now
Questions 93

Which term describes when the Cisco Firepower downloads threat intelligence updates from Cisco Talos?

Options:

A.

consumption

B.

sharing

C.

analysis

D.

authoring

Buy Now
Questions 94

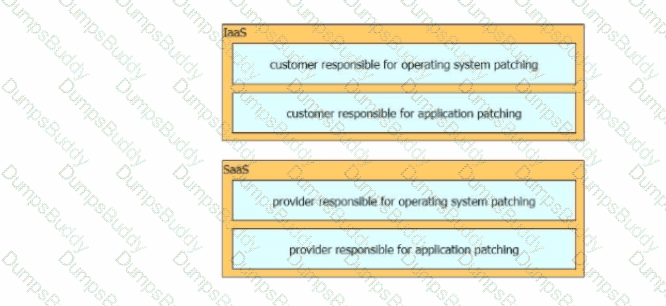
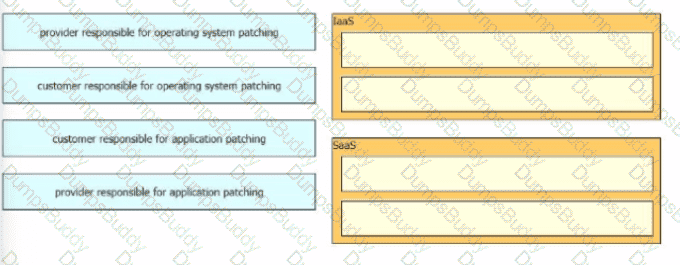
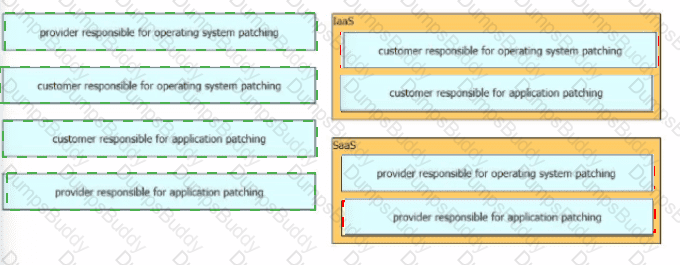
Drag and drop the security responsibilities from the left onto the corresponding cloud service models on the right.
350-701 Question 94

Options:

Buy Now
Questions 95

What is a description of microsegmentation?

Options:

A.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate

B.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery

C.

Environments implement private VLAN segmentation to group servers with similar applications.

D.

Environments deploy centrally managed host-based firewall rules on each server or container

Buy Now
Questions 96

Refer to the exhibit.

350-701 Question 96

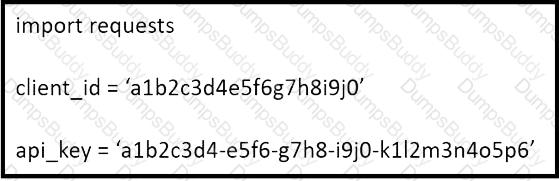
What does the API key do while working with https://api.amp.cisco.com/v1/computers?

Options:

A.

displays client ID

B.

HTTP authorization

C.

Imports requests

D.

HTTP authentication

Buy Now
Questions 97

Which feature within Cisco Umbrella allows for the ability to inspect secure HTTP traffic?

Options:

A.

File Analysis

B.

SafeSearch

C.

SSL Decryption

D.

Destination Lists

Buy Now
Questions 98

Which command enables 802.1X globally on a Cisco switch?

Options:

A.

dot1x system-auth-control

B.

dot1x pae authenticator

C.

authentication port-control aut

D.

aaa new-model

Buy Now
Questions 99

Which feature enables a Cisco ISR to use the default bypass list automatically for web filtering?

Options:

A.

filters

B.

group key

C.

company key

D.

connector

Buy Now
Questions 100

Which flaw does an attacker leverage when exploiting SQL injection vulnerabilities?

Options:

A.

user input validation in a web page or web application

B.

Linux and Windows operating systems

C.

database

D.

web page images

Buy Now
Questions 101

An engineer implements Cisco CloudLock to secure a Microsoft Office 365 application in the cloud. The engineer must configure protection for corporate files in case of any incidents. Which two actions must be taken to complete the implementation? (Choose two.)

Options:

A.

Expire the public share URL

B.

Send Cisco Webex message to specified users when an incident is triggered

C.

Transfer ownership of the files to a specified owner and folder

D.

Remove all users as collaborators on the files

E.

Disable the ability for commenters and viewers to download and copy the files

Buy Now
Questions 102

Which policy is used to capture host information on the Cisco Firepower Next Generation Intrusion Prevention

System?

Options:

A.

Correlation

B.

Intrusion

C.

Access Control

D.

Network Discovery

Buy Now
Questions 103

What is the target in a phishing attack?

Options:

A.

perimeter firewall

B.

IPS

C.

web server

D.

endpoint

Buy Now
Questions 104

Which policy does a Cisco Secure Web Appliance use to block or monitor URL requests based on the reputation score?

Options:

A.

Encryption

B.

Enforcement Security

C.

Cisco Data Security

D.

Outbound Malware Scanning

Buy Now
Questions 105

Which encryption algorithm provides highly secure VPN communications?

Options:

A.

3DES

B.

AES 256

C.

AES 128

D.

DES

Buy Now
Questions 106

How does a Cisco Secure Firewall help to lower the risk of exfiltration techniques that steal customer data?

Options:

A.

Blocking UDP port 53

B.

Blocking TCP port 53

C.

Encrypting the DNS communication

D.

Inspecting the DNS traffic

Buy Now
Questions 107

An administrator needs to configure the Cisco ASA via ASDM such that the network management system

can actively monitor the host using SNMPv3. Which two tasks must be performed for this configuration?

(Choose two.)

Options:

A.

Specify the SNMP manager and UDP port.

B.

Specify an SNMP user group

C.

Specify a community string.

D.

Add an SNMP USM entry

E.

Add an SNMP host access entry

Buy Now
Questions 108

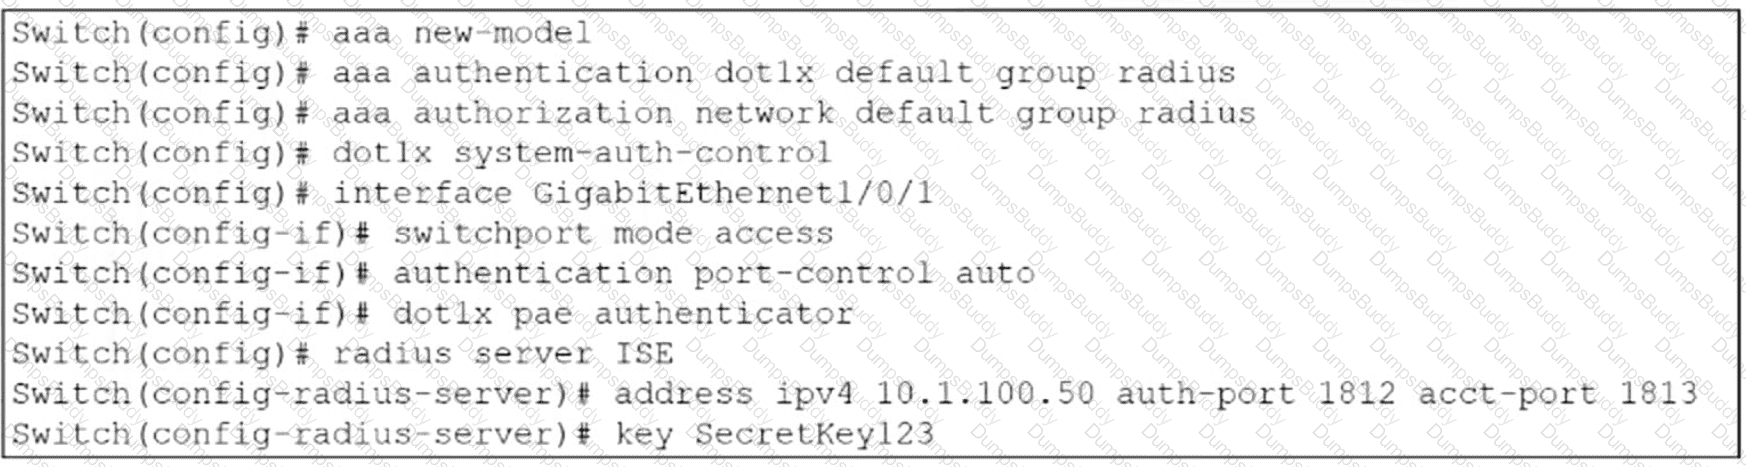
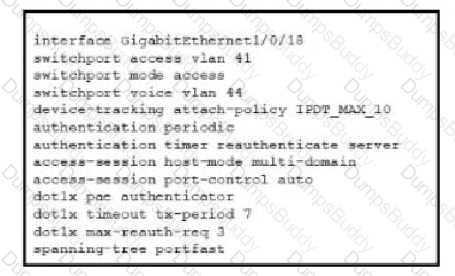
Refer to the exhibit.

350-701 Question 108

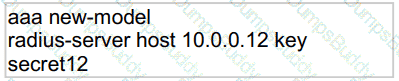
Which statement about the authentication protocol used in the configuration is true?

Options:

A.

The authentication request contains only a password

B.

The authentication request contains only a username

C.

The authentication and authorization requests are grouped in a single packet

D.

There are separate authentication and authorization request packets

Buy Now
Questions 109

What is a functional difference between Cisco Secure Endpoint and Cisco Umbrella Roaming Client?

Options:

A.

Secure Endpoint authenticates users and provides segmentation, and the Umbrella Roaming Client allows only for VPN connectivity.

B.

Secure Endpoint stops and tracks malicious activity on hosts, and the Umbrella Roaming Client tracks only URL-based threats.

C.

The Umbrella Roaming Client authenticates users and provides segmentation, and Secure Endpoint allows only for VPN connectivity.

D.

The Umbrella Roaming client stops and tracks malicious activity on hosts, and Secure Endpoint tracks only URL-based threats.

Buy Now
Questions 110

Which capability is exclusive to a Cisco AMP public cloud instance as compared to a private cloud instance?

Options:

A.

RBAC

B.

ETHOS detection engine

C.

SPERO detection engine

D.

TETRA detection engine

Buy Now
Questions 111

An engineer is configuring cloud logging on Cisco ASA and needs events to compress. Which component must be configured to accomplish this goal?

Options:

A.

CDO event viewer

B.

SWC service

C.

Cisco analytics

D.

SDC VM

Buy Now
Questions 112

What must be enabled to secure SaaS-based applications?

Options:

A.

modular policy framework

B.

two-factor authentication

C.

application security gateway

D.

end-to-end encryption

Buy Now
Questions 113

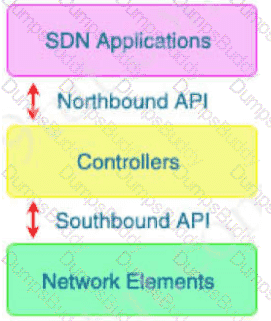
Which type of API is being used when a controller within a software-defined network architecture dynamically

makes configuration changes on switches within the network?
Options:

A.

westbound AP

B.

southbound API

C.

northbound API

D.

eastbound API

Buy Now
Questions 114

350-701 Question 114

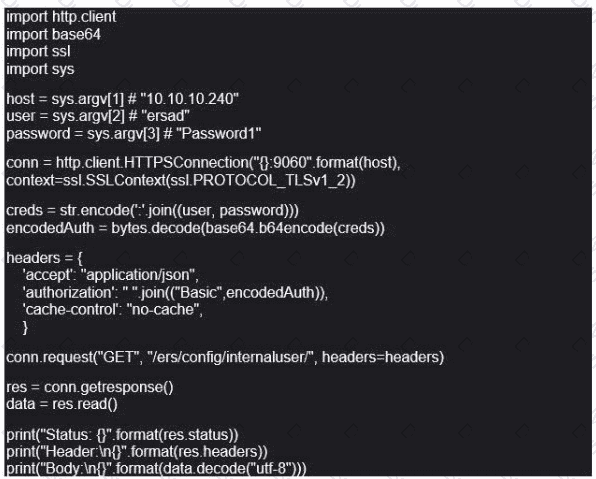
Refer to the exhibit. What does this Python script accomplish?

Options:

A.

It allows authentication with TLSv1 SSL protocol

B.

It authenticates to a Cisco ISE with an SSH connection.

C.

lt authenticates to a Cisco ISE server using the username of ersad

D.

It lists the LDAP users from the external identity store configured on Cisco ISE

Buy Now
Questions 115

Which Cisco security solution provides patch management in the cloud?

Options:

A.

Cisco Umbrella

B.

Cisco ISE

C.

Cisco CloudLock

D.

Cisco Tetration

Buy Now
Questions 116

Which kind of API that is used with Cisco DNA Center provisions SSIDs, QoS policies, and update software versions on switches?

Options:

A.

Integration

B.

Intent

C.

Event

D.

Multivendor

Buy Now
Questions 117

Which statement about IOS zone-based firewalls is true?

Options:

A.

An unassigned interface can communicate with assigned interfaces

B.

Only one interface can be assigned to a zone.

C.

An interface can be assigned to multiple zones.

D.

An interface can be assigned only to one zone.

Buy Now
Questions 118

Which two criteria must a certificate meet before the WSA uses it to decrypt application traffic? (Choose two.)

Options:

A.

It must include the current date.

B.

It must reside in the trusted store of the WSA.

C.

It must reside in the trusted store of the endpoint.

D.

It must have been signed by an internal CA.

E.

it must contain a SAN.

Buy Now
Questions 119

An engineer must deploy a Cisco Secure Web Appliance. Antimalware scanning must use the Outbreak Heuristics antimalware category on files identified as malware before performing any other processes. What must be configured on the Secure Web Appliance to meet the requirements?

Options:

A.

Sophos scanning engine

B.

Webroot scanning engine

C.

McAfee scanning engine

D.

Adaptive Scanning

Buy Now
Questions 120

An organization wants to use Cisco FTD or Cisco ASA devices. Specific URLs must be blocked from being

accessed via the firewall which requires that the administrator input the bad URL categories that the

organization wants blocked into the access policy. Which solution should be used to meet this requirement?

Options:

A.

Cisco ASA because it enables URL filtering and blocks malicious URLs by default, whereas Cisco FTDdoes not

B.

Cisco ASA because it includes URL filtering in the access control policy capabilities, whereas Cisco FTD does not

C.

Cisco FTD because it includes URL filtering in the access control policy capabilities, whereas Cisco ASA does not

D.

Cisco FTD because it enables URL filtering and blocks malicious URLs by default, whereas Cisco ASA does not

Buy Now
Questions 121

Which Cisco WSA feature supports access control using URL categories?

Options:

A.

transparent user identification

B.

SOCKS proxy services

C.

web usage controls

D.

user session restrictions

Buy Now
Questions 122

A security policy administrator configures a Cisco Secure Access SIA DNS policy to block all social media categories for the Marketing Active Directory group. While testing from one of the user machines, access to the domain https://socialmediaexample.org is allowed. When searching for this domain in User Activity Search, no queries for that specific domain are returned. Consider these facts:

    The test user is part of the Marketing Active Directory group.

    The domain socialmediaexample.org belongs to the social media category.

    The user is configured with the Umbrella Roaming Client for DNS redirection.

    All other social media websites are properly blocked for the same user and match the correct policy.

Which configuration must the administrator implement in Cisco Secure Access to meet the requirement?

Options:

A.

Enable HTTPS inspection in the web policy because this is an HTTPS site.

B.

Add socialmediaexample.org to the External Domains list.

C.

Enable the intelligent proxy to identify this domain properly.

D.

Add socialmediaexample.org to the Internal Domains list.

Buy Now
Questions 123

An engineer is securing access to data served by a cloud-based application. The data must be protected from modification in transit, and its integrity must be validated. The following security measures have been implemented:

• Governance with role-based access control based on the principle of least privilege

• TLS 1.3 with signed certificates

• AES-256 with MD5

What must be configured to complete the secure implementation?

Options:

A.

3DES instead of AES

B.

DES instead of TLS 1.3

C.

SHA-512 instead of MD5

D.

SSLv3 instead of MD5

Buy Now
Questions 124

An administrator configures a new destination list in Cisco Umbrella so that the organization can block specific domains for its devices. What should be done to ensure that all subdomains of domain.com are blocked?

Options:

A.

Configure the *.com address in the block list.

B.

Configure the *.domain.com address in the block list

C.

Configure the *.domain.com address in the block list

D.

Configure the domain.com address in the block list

Buy Now
Questions 125

Which service allows a user to export application usage and performance statistics with Cisco Application Visibility and Control?

Options:

A.

SNMP

B.

802.1X

C.

NetFlow

D.

SNORT

Buy Now
Questions 126

Which solution supports high availability in routed or transparent mode as well as in northbound and

southbound deployments?

Options:

A.

Cisco FTD with Cisco ASDM

B.

Cisco FTD with Cisco FMC

C.

Cisco Firepower NGFW physical appliance with Cisco. FMC

D.

Cisco Firepower NGFW Virtual appliance with Cisco FMC

Buy Now
Questions 127

Which open standard creates a framework for sharing threat intelligence in a machine-digestible format?
Options:

A.

OpenC2

B.

OpenlOC

C.

CybOX

D.

STIX

Buy Now
Questions 128

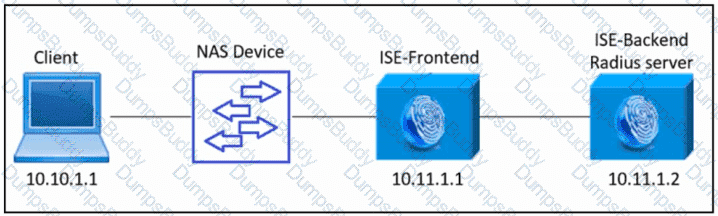
350-701 Question 128

Refer to the exhibit. An engineer must configure a new Cisco ISE backend server as a RADIUS server to provide AAA for all access requests from the client to the ISE-Frontend server.

Which Cisco ISE configuration must be used?

Options:

A.

Set 10.11.1.2 as a network device in ISE-Frontend. Set port 1700/2083 for RADIUS authentication.

B.

Set 10.11.1.1 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

C.

Set 10.11.1.2 as the external RADIUS server in ISE-Frontend. Set ports 1812/1813 for authentication and accounting.

D.

Set 10.11.1.1 as a network device in ISE-Frontend. Set ports 1700/2083 for RADIUS authentication.

Buy Now
Questions 129

In which two ways does Easy Connect help control network access when used with Cisco TrustSec? (Choose two)
Options:

A.

It allows multiple security products to share information and work together to enhance security posture in the network.

B.

It creates a dashboard in Cisco ISE that provides full visibility of all connected endpoints.

C.

It allows for the assignment of Security Group Tags and does not require 802.1x to be configured on the switch or the endpoint.

D.

It integrates with third-party products to provide better visibility throughout the network.

E.

It allows for managed endpoints that authenticate to AD to be mapped to Security Groups (PassiveID).

Buy Now
Questions 130

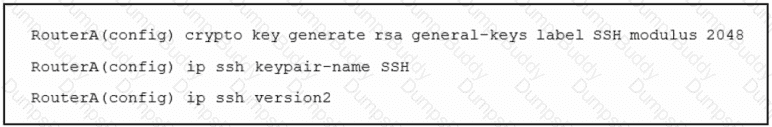
350-701 Question 130

Refer to the exhibit. An engineer must enable secure SSH protocols and enters this configuration. What are two results of running this set of commands on a Cisco router? (Choose two.)

Options:

A.

Labels the key pair to be used for SSH

B.

Uses the FQDN with the label command

C.

Generates AES key pairs on the router

D.

Generates RSA key pair on the router

E.

Enables SSHv1 on the router

Buy Now
Questions 131

Which two capabilities of Integration APIs are utilized with Cisco Catalyst Center? (Choose two.)

Options:

A.

Create new SSIDs on a wireless LAN controller

B.

Connect to ITSM platforms

C.

Automatically deploy new virtual routers

D.

Upgrade software on switches and routers

E.

Third party reporting

Buy Now
Questions 132

Which action controls the amount of URI text that is stored in Cisco WSA logs files?

Options:

A.

Configure the datasecurityconfig command

B.

Configure the advancedproxyconfig command with the HTTPS subcommand

C.

Configure a small log-entry size.

D.

Configure a maximum packet size.

Buy Now
Questions 133

Which type of dashboard does Cisco DNA Center provide for complete control of the network?
Options:

A.

service management

B.

centralized management

C.

application management

D.

distributed management

Buy Now
Questions 134

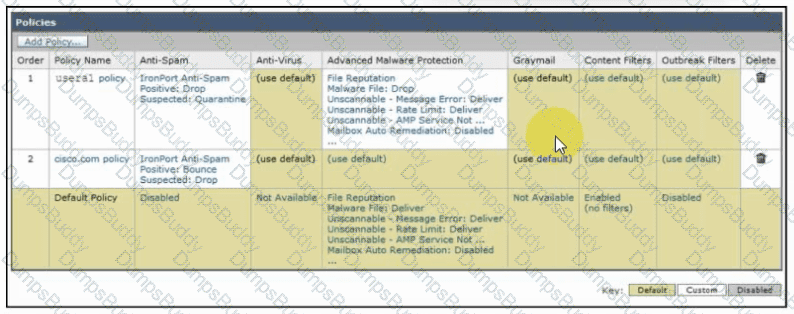
350-701 Question 134

Refer to the exhibit. An engineer must configure an incoming mail policy so that each email sent from usera1@example.com to a domain of @cisco.com is scanned for antispam and advanced malware protection. All other settings will use the default behavior. What must be configured in the incoming mail policy to meet the requirements?

Options:

A.

Policy Name: Default Policy  Sender: usera1@example.com  Recipient: @cisco.com

B.

Policy Name: usera1 policy  Sender: usera1@example.com  Recipient: @cisco.com

C.

Policy Name: Anti-Malware policy  Sender: usera1@example.com  Recipient: @cisco.com

D.

Policy Name: cisco.com policy  Sender: usera1@example.com  Recipient: @cisco.com

Buy Now
Questions 135

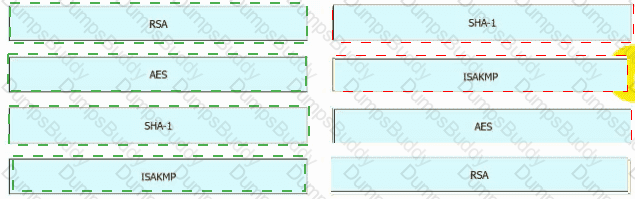
Drag and drop the VPN functions from the left onto the descriptions on the right.
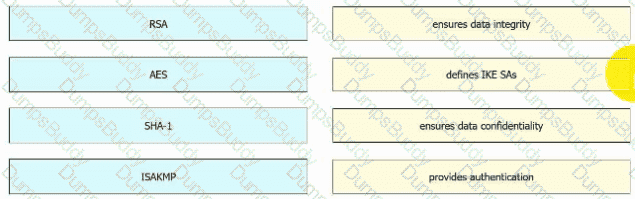
350-701 Question 135

Options:

Buy Now
Questions 136

A network engineer has entered the snmp-server user andy myv3 auth sha cisco priv aes 256

cisc0380739941 command and needs to send SNMP information to a host at 10.255.254.1. Which command achieves this goal?

Options:

A.

snmp-server host inside 10.255.254.1 version 3 andy

B.

snmp-server host inside 10.255.254.1 version 3 myv3

C.

snmp-server host inside 10.255.254.1 snmpv3 andy

D.

snmp-server host inside 10.255.254.1 snmpv3 myv3

Buy Now
Questions 137

Which Cisco platform ensures that machines that connect to organizational networks have the recommended

antivirus definitions and patches to help prevent an organizational malware outbreak?
Options:

A.

Cisco WiSM

B.

Cisco ESA

C.

Cisco ISE

D.

Cisco Prime Infrastructure

Buy Now
Questions 138

Which ESA implementation method segregates inbound and outbound email?

Options:

A.

one listener on a single physical Interface

B.

pair of logical listeners on a single physical interface with two unique logical IPv4 addresses and one IPv6 address

C.

pair of logical IPv4 listeners and a pair Of IPv6 listeners on two physically separate interfaces

D.

one listener on one logical IPv4 address on a single logical interface

Buy Now
Questions 139

An administrator is implementing management plane protection and must configure an interface on a Cisco router to only terminate management packets that are destined for the router. Which set of IOS commands must be used to complete the implementation?

Options:

A.
B.
C.
D.
Buy Now
Questions 140

A network engineer must migrate a Cisco WSA virtual appliance from one physical host to another physical host by using VMware vMotion. What is a requirement for both physical hosts?
Options:

A.

The hosts must run Cisco AsyncOS 10.0 or greater.

B.

The hosts must run different versions of Cisco AsyncOS.

C.

The hosts must have access to the same defined network.

D.

The hosts must use a different datastore than the virtual appliance.

Buy Now
Questions 141

What is the role of an endpoint in protecting a user from a phishing attack?

Options:

A.

Use Cisco Stealthwatch and Cisco ISE Integration.

B.

Utilize 802.1X network security to ensure unauthorized access to resources.

C.

Use machine learning models to help identify anomalies and determine expected sending behavior.

D.

Ensure that antivirus and anti malware software is up to date

Buy Now
Questions 142

Which system performs compliance checks and remote wiping?

Options:

A.

MDM

B.

ISE

C.

AMP

D.

OTP

Buy Now
Questions 143

350-701 Question 143

Refer to the exhibit. What function does the API key perform while working with https://api.amp.cisco.com/v1/computers?

Options:

A.

imports requests

B.

HTTP authorization

C.

HTTP authentication

D.

plays dent ID

Buy Now
Questions 144

Which DoS attack uses fragmented packets in an attempt to crash a target machine?

Options:

A.

teardrop

B.

smurf

C.

LAND

D.

SYN flood

Buy Now
Questions 145

Which type of data does the Cisco Stealthwatch system collect and analyze from routers, switches, and firewalls?

Options:

A.

NTP

B.

syslog

C.

SNMP

D.

NetFlow

Buy Now
Questions 146

Which statement about the configuration of Cisco ASA NetFlow v9 Secure Event Logging is true?

Options:

A.

To view bandwidth usage for NetFlow records, the QoS feature must be enabled.

B.

A sysopt command can be used to enable NSEL on a specific interface.

C.

NSEL can be used without a collector configured.

D.

A flow-export event type must be defined under a policy

Buy Now
Questions 147

Which exfiltration method does an attacker use to hide and encode data inside DNS requests and queries?

Options:

A.

DNS tunneling

B.

DNSCrypt

C.

DNS security

D.

DNSSEC

Buy Now
Questions 148

How does Cisco Umbrella protect clients when they operate outside of the corporate network?

Options:

A.

by modifying the registry for DNS lookups

B.

by using Active Directory group policies to enforce Cisco Umbrella DNS servers

C.

by using the Cisco Umbrella roaming client

D.

by forcing DNS queries to the corporate name servers

Buy Now
Questions 149

Which two configurations must be made on Cisco ISE and on Cisco TrustSec devices to force a session to be adjusted after a policy change is made? (Choose two)

Options:

A.

posture assessment

B.

aaa authorization exec default local

C.

tacacs-server host 10.1.1.250 key password

D.

aaa server radius dynamic-author

E.

CoA

Buy Now
Questions 150

A network engineer must create an access control list on a Cisco Adaptive Security Appliance firewall. The access control list must permit HTTP traffic to the internet from the organization ' s inside network 192.168.1.0/24. Which IOS command must oe used to create the access control list?

Options:

A.
B.
C.
D.
Buy Now
Questions 151

An organization configures Cisco Umbrella to be used for its DNS services. The organization must be able to block traffic based on the subnet that the endpoint is on but it sees only the requests from its public IP address instead of each internal IP address. What must be done to resolve this issue?

Options:

A.

Set up a Cisco Umbrella virtual appliance to internally field the requests and see the traffic of each IP address

B.

Use the tenant control features to identify each subnet being used and track the connections within theCisco Umbrella dashboard

C.

Install the Microsoft Active Directory Connector to give IP address information stitched to the requests in the Cisco Umbrella dashboard

D.

Configure an internal domain within Cisco Umbrella to help identify each address and create policy from the domains

Buy Now
Questions 152

A network administrator needs to find out what assets currently exist on the network. Third-party systems need to be able to feed host data into Cisco Firepower. What must be configured to accomplish this?

Options:

A.

a Network Discovery policy to receive data from the host

B.

a Threat Intelligence policy to download the data from the host

C.

a File Analysis policy to send file data into Cisco Firepower

D.

a Network Analysis policy to receive NetFlow data from the host

Buy Now
Questions 153

What is the difference between deceptive phishing and spear phishing?

Options:

A.

Deceptive phishing is an attack aimed at a specific user in the organization who holds a C-level role.

B.

A spear phishing campaign is aimed at a specific person versus a group of people.

C.

Spear phishing is when the attack is aimed at the C-level executives of an organization.

D.

Deceptive phishing hijacks and manipulates the DNS server of the victim and redirects the user to a false webpage.

Buy Now
Questions 154

What is a difference between an XSS attack and an SQL injection attack?

Options:

A.

SQL injection is a hacking method used to attack SQL databases, whereas XSS attacks can exist in many different types of applications

B.

XSS is a hacking method used to attack SQL databases, whereas SQL injection attacks can exist in many different types of applications

C.

SQL injection attacks are used to steal information from databases whereas XSS attacks are used toredirect users to websites where attackers can steal data from them

D.

XSS attacks are used to steal information from databases whereas SQL injection attacks are used toredirect users to websites where attackers can steal data from them

Buy Now
Questions 155

Which statement describes a serverless application?

Options:

A.

The application delivery controller in front of the server farm designates on which server the application runs each time.

B.

The application runs from an ephemeral, event-triggered, and stateless container that is fully managed by a cloud provider.

C.

The application is installed on network equipment and not on physical servers.

D.

The application runs from a containerized environment that is managed by Kubernetes or Docker Swarm.

Buy Now
Questions 156

An organization has a Cisco Stealthwatch Cloud deployment in their environment. Cloud logging is working as expected, but logs are not being received from the on-premise network, what action will resolve this issue?

Options:

A.

Configure security appliances to send syslogs to Cisco Stealthwatch Cloud

B.

Configure security appliances to send NetFlow to Cisco Stealthwatch Cloud

C.

Deploy a Cisco FTD sensor to send events to Cisco Stealthwatch Cloud

D.

Deploy a Cisco Stealthwatch Cloud sensor on the network to send data to Cisco Stealthwatch Cloud

Buy Now
Questions 157

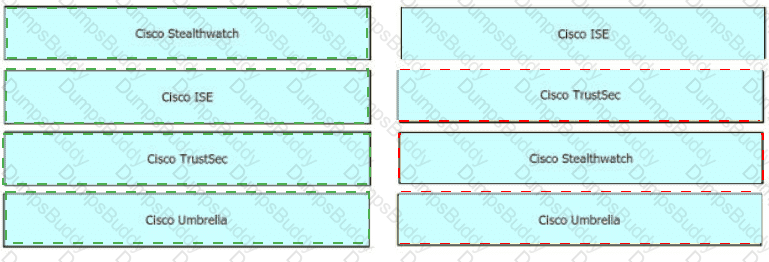
Drag and drop the solutions from the left onto the solution ' s benefits on the right.
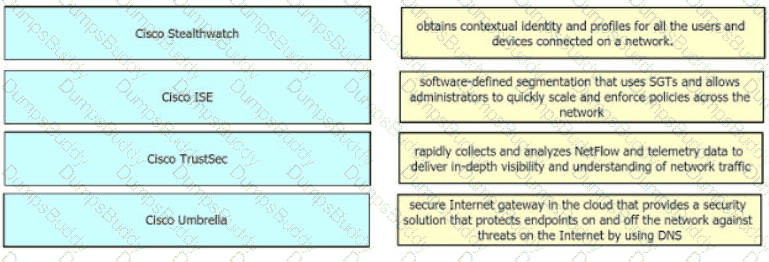
350-701 Question 157

Options:

Buy Now
Questions 158

Which feature requires that network telemetry be enabled?

Options:

A.

per-interface stats

B.

SNMP trap notification

C.

Layer 2 device discovery

D.

central syslog system

Buy Now
Questions 159

Why is it important to patch endpoints consistently?

Options:

A.

Patching reduces the attack surface of the infrastructure.

B.

Patching helps to mitigate vulnerabilities.

C.

Patching is required per the vendor contract.

D.

Patching allows for creating a honeypot.

Buy Now
Questions 160

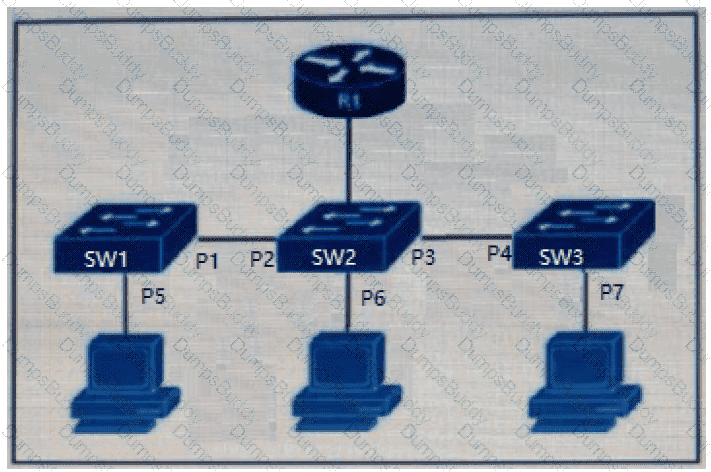
Refer to the exhibit.

350-701 Question 160

The DHCP snooping database resides on router R1, and dynamic ARP inspection is configured only on switch SW2. Which ports must be configured as untrusted so that dynamic ARP inspection operates normally?

Options:

A.

P2 and P3 only

B.

P5, P6, and P7 only

C.

P1, P2, P3, and P4 only

D.

P2, P3, and P6 only

Buy Now
Questions 161

Which technology must be used to implement secure VPN connectivity among company branches over a

private IP cloud with any-to-any scalable connectivity?

Options:

A.

DMVPN

B.

FlexVPN

C.

IPsec DVTI

D.

GET VPN

Buy Now
Questions 162

Which method is used to deploy certificates and configure the supplicant on mobile devices to gain access to

network resources?

Options:

A.

BYOD on boarding

B.

Simple Certificate Enrollment Protocol

C.

Client provisioning

D.

MAC authentication bypass

Buy Now
Questions 163

What is an advantage of using a next-generation firewall compared to a traditional firewall?

Options:

A.

Next-generation firewalls have stateless inspection capabilities, and traditional firewalls use stateful inspection.

B.

Next-generation firewalls use dynamic packet filtering, and traditional firewalls use static packet filtering.

C.

Next-generation firewalls have threat intelligence feeds, and traditional firewalls use signature detection.

D.

Next-generation firewalls use intrusion prevention policies, and traditional firewalls use intrusion detection policies.

Buy Now
Questions 164

An organization wants to secure users, data, and applications in the cloud. The solution must be API-based and

operate as a cloud-native CASB. Which solution must be used for this implementation?

Options:

A.

Cisco Cloudlock

B.

Cisco Cloud Email Security

C.

Cisco Firepower Next-Generation Firewall

D.

Cisco Umbrella

Buy Now
Questions 165

Which feature is used to restrict communication between interfaces on a Cisco ASA?

Options:

A.

VLAN subinterfaces

B.

Traffic zones

C.

Security levels

D.

VxLAN interfaces

Buy Now
Questions 166

Which Cisco security solution gives the most complete view of the relationships and evolution of Internet domains IPs, and flies, and helps to pinpoint attackers ' infrastructures and predict future threat?

Options:

A.

Cisco Secure Network Analytics

B.

Cisco Secure Cloud Analytics

C.

Cisco Umbrella Investigate

D.

Cisco pxGrid

Buy Now
Questions 167

An engineer is configuring cloud logging using a company-managed Amazon S3 bucket for Cisco Umbrella logs. What benefit does this configuration provide for accessing log data?

Options:

A.

It is included m the license cost for the multi-org console of Cisco Umbrella

B.

It can grant third-party SIEM integrations write access to the S3 bucket

C.

No other applications except Cisco Umbrella can write to the S3 bucket

D.

Data can be stored offline for 30 days.

Buy Now
Questions 168

An organization is using Cisco Firepower and Cisco Meraki MX for network security and needs to centrally

manage cloud policies across these platforms. Which software should be used to accomplish this goal?

Options:

A.

Cisco Defense Orchestrator

B.

Cisco Secureworks

C.

Cisco DNA Center

D.

Cisco Configuration Professional

Buy Now
Questions 169

What is a prerequisite when integrating a Cisco ISE server and an AD domain?

Options:

A.

Place the Cisco ISE server and the AD server in the same subnet

B.

Configure a common administrator account

C.

Configure a common DNS server

D.

Synchronize the clocks of the Cisco ISE server and the AD server

Buy Now
Questions 170

What is a benefit of using GET VPN over FlexVPN within a VPN deployment?

Options:

A.

GET VPN supports Remote Access VPNs

B.

GET VPN natively supports MPLS and private IP networks

C.

GET VPN uses multiple security associations for connections

D.

GET VPN interoperates with non-Cisco devices

Buy Now
Questions 171

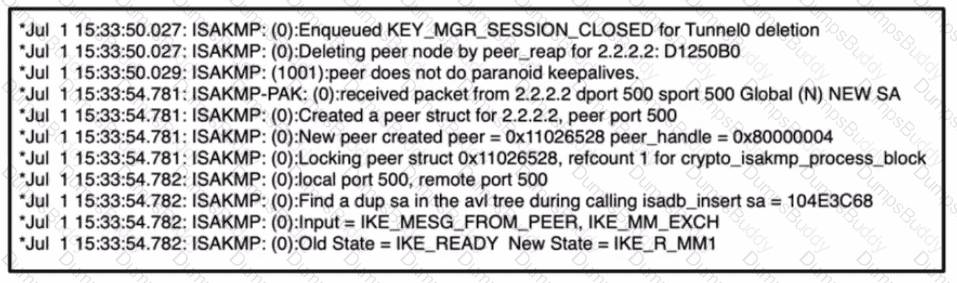
Refer to the exhibit,

350-701 Question 171

which command results in these messages when attempting to troubleshoot an iPsec VPN connection?

Options:

A.

debug crypto isakmp

B.

debug crypto ipsec endpoint

C.

debug crypto Ipsec

D.

debug crypto isakmp connection

Buy Now
Questions 172

What are two DDoS attack categories? (Choose two)

Options:

A.

sequential

B.

protocol

C.

database

D.

volume-based

E.

screen-based

Buy Now
Questions 173

Which Cisco Secure Client module is integrated with Splunk Enterprise to provide monitoring capabilities to administrators to allow them to view endpoint application usage?

Options:

A.

Umbrella Roaming Security

B.

Network Visibility

C.

AMP Enabler

D.

ISE Posture

Buy Now
Questions 174

What is a characteristic of Cisco ASA Netflow v9 Secure Event Logging?

Options:

A.

It tracks flow-create, flow-teardown, and flow-denied events.

B.

It provides stateless IP flow tracking that exports all records of a specific flow.

C.

It tracks the flow continuously and provides updates every 10 seconds.

D.

Its events match all traffic classes in parallel.

Buy Now
Questions 175

Which two functions does the Cisco Advanced Phishing Protection solution perform in trying to protect from phishing attacks? (Choose two.)

Options:

A.

blocks malicious websites and adds them to a block list

B.

does a real-time user web browsing behavior analysis

C.

provides a defense for on-premises email deployments

D.

uses a static algorithm to determine malicious

E.

determines if the email messages are malicious

Buy Now
Questions 176

A manufacturing company contracted an external software vendor to develop an application that dynamically creates marketing messages personalized to the business and audience. To ensure that communication between the sender and recipient email addresses does not create false positives, an exception rule must be configured in Cisco Secure Email Threat Defense. Which configuration must be performed?

Options:

A.

Implement an Exception Rule with a wildcard email address.

B.

Add a Policy Exception Rule with a Sender/Recipient pair set.

C.

Apply a sender-based Policy Exception Rule.

D.

Configure a recipient-based Policy Exception Rule.

Buy Now
Questions 177

Which functions of an SDN architecture require southbound APIs to enable communication?

Options:

A.

SDN controller and the network elements

B.

management console and the SDN controller

C.

management console and the cloud

D.

SDN controller and the cloud

Buy Now
Questions 178

Which Cisco AMP feature allows an engineer to look back to trace past activities, such as file and process activity on an endpoint?

Options:

A.

Retrospective security

B.

Endpoint isolation

C.

Advanced investigation

D.

Advanced search

Buy Now
Questions 179

Which two solutions help combat social engineering and phishing at the endpoint level? (Choose two.)

Options:

A.

Cisco Umbrella

B.

Cisco ISE

C.

Cisco DNA Center

D.

Cisco TrustSec

E.

Cisco Duo Security

Buy Now
Questions 180

A facilities team is onboarding a fleet of badge readers and IP cameras through MAB authentication on Cisco Catalyst access switches integrated with Cisco ISE. After Cisco ISE profiles each endpoint, an authorization policy must dynamically move the device into a dedicated IoT VLAN that differs from the access VLAN statically defined on the port. The endpoints lack a supplicant and cannot automatically renew their DHCP addresses. The network engineer requires Cisco ISE to issue a Change of Authorization that forces each endpoint to re-establish connectivity and request a fresh DHCP lease under the new authorization policy. Which configuration action must be performed on Cisco ISE to meet the requirement?

Options:

A.

Configure the authorization profile to send a CoA-Reauth to the access switch.

B.

Configure the authentication policy to send a CoA-Terminate to reconnect the endpoint.

C.

Configure the authorization profile to send a Port-Bounce CoA to the switch.

D.

Configure the authorization policy to send a CoA-Reconnect and rely on the idle timeout.

Buy Now
Questions 181

Refer to the exhibit.

350-701 Question 181

Refer to the exhibit. A Cisco ISE administrator adds a new switch to an 802.1X deployment and has difficulty with some endpoints gaining access.

Most PCs and IP phones can connect and authenticate using their machine certificate credentials. However printer and video cameras cannot base d on the interface configuration provided, what must be to get these devices on to the network using Cisco ISE for authentication and authorization while maintaining security controls?

Options:

A.

Change the default policy in Cisco ISE to allow all devices not using machine authentication .

B.

Enable insecure protocols within Cisco ISE in the allowed protocols configuration.

C.

Configure authentication event fail retry 2 action authorize vlan 41 on the interface

D.

Add mab to the interface configuration.

Buy Now
Questions 182

Which Cisco Advanced Malware protection for Endpoints deployment architecture is designed to keep data

within a network perimeter?

Options:

A.

cloud web services

B.

network AMP

C.

private cloud

D.

public cloud

Buy Now
Questions 183

Which feature within Cisco ISE verifies the compliance of an endpoint before providing access to the

network?
Options:

A.

Posture

B.

Profiling

C.

pxGrid

D.

MAB

Buy Now
Questions 184

What is a description of microsegmentation?

Options:

A.

Environments deploy a container orchestration platform, such as Kubernetes, to manage the application delivery.

B.

Environments apply a zero-trust model and specify how applications on different servers or containers can communicate.

C.

Environments deploy centrally managed host-based firewall rules on each server or container.

D.

Environments implement private VLAN segmentation to group servers with similar applications.

Buy Now
Questions 185

350-701 Question 185

Refer to the exhibit. Consider that any feature of DNS requests, such as the length of the domain name and the number of subdomains, can be used to construct models of expected behavior to which observed values can be compared. Which type of malicious attack are these values associated with?

Options:

A.

W32/AutoRun worm

B.

HeartBleed SSL Bug

C.

Spectre Worm

D.

Eternal Blue Windows

Buy Now
Questions 186

A network engineer must configure a Cisco Secure Email Gateway to prompt users to enter two forms of information before gaining access. The Secure Email Gateway must also join a cluster machine using preshared keys. What must be configured to meet these requirements?

Options:

A.

Enable two-factor authentication through a RADIUS server and then join the cluster by using the Secure Email Gateway CLI.

B.

Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Secure Email Gateway CLI.

C.

Enable two-factor authentication through a RADIUS server and then join the cluster by using the Secure Email Gateway GUI.

D.

Enable two-factor authentication through a TACACS+ server and then join the cluster by using the Secure Email Gateway GUI.

Buy Now
Questions 187

Why would a user choose an on-premises ESA versus the CES solution?

Options:

A.

Sensitive data must remain onsite.

B.

Demand is unpredictable.

C.

The server team wants to outsource this service.

D.

ESA is deployed inline.

Buy Now
Questions 188

What is the purpose of the Cisco Endpoint loC feature?

Options:

A.

It provides stealth threat prevention.

B.

lt is a signature-based engine.

C.

lt is an incident response tool

D.

It provides precompromise detection.

Buy Now
Questions 189

Refer to the exhibit.

350-701 Question 189

An engineer must configure a Cisco switch to perform PPP authentication via a TACACS server located at IP address 10.1.1.10. Authentication must fall back to the local database using the username LocalUser and password C1Sc0451069341l if the TACACS server is unreachable.

Drag and drop the commands from the left onto the corresponding configuration steps on the right.
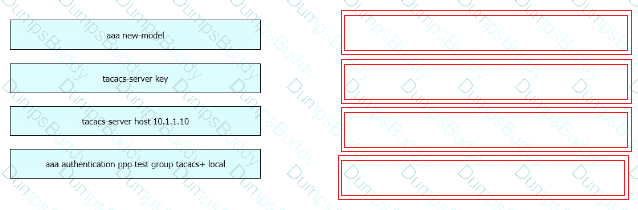
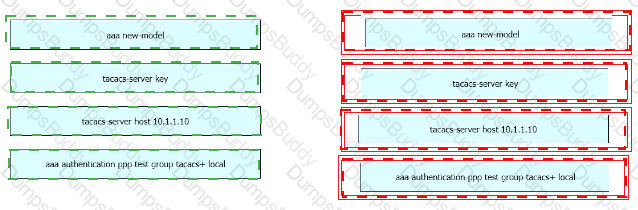
350-701 Question 189

Options:

Buy Now
Questions 190

What provides the ability to program and monitor networks from somewhere other than the DNAC GUI?

Options:

A.

NetFlow

B.

desktop client

C.

ASDM

D.

API

Buy Now
Questions 191

What provides total management for mobile and PC including managing inventory and device tracking, remote view, and live troubleshooting using the included native remote desktop support?

Options:

A.

mobile device management

B.

mobile content management

C.

mobile application management

D.

mobile access management

Buy Now
Questions 192

A network engineer is configuring DMVPN and entered the crypto isakmp key cisc0380739941 address 0.0.0.0 command on hostA. The tunnel is not being established to hostB. What action is needed to authenticate the VPN?

Options:

A.

Change isakmp to ikev2 in the command on hostA.

B.

Enter the command with a different password on hostB.

C.

Enter the same command on hostB.

D.

Change the password on hostA to the default password.

Buy Now
Questions 193

Which two features of Cisco Email Security can protect your organization against email threats? (Choose two)

Options:

A.

Time-based one-time passwords

B.

Data loss prevention

C.

Heuristic-based filtering

D.

Geolocation-based filtering

E.

NetFlow

Buy Now
Questions 194

An engineer is configuring AMP for endpoints and wants to block certain files from executing. Which outbreak

control method is used to accomplish this task?

Options:

A.

device flow correlation

B.

simple detections

C.

application blocking list

D.

advanced custom detections

Buy Now
Questions 195

What is a benefit of flexible NetFlow records?

Options:

A.

They are used for security

B.

They are used for accounting

C.

They monitor a packet from Layer 2 to Layer 5

D.

They have customized traffic identification

Buy Now
Questions 196

Which function is included when Cisco AMP is added to web security?

Options:

A.

multifactor, authentication-based user identity

B.

detailed analytics of the unknown file ' s behavior

C.

phishing detection on emails

D.

threat prevention on an infected endpoint

Buy Now
Questions 197

What are two benefits of using an MDM solution? (Choose two.)

Options:

A.

grants administrators a way to remotely wipe a lost or stolen device

B.

provides simple and streamlined login experience for multiple applications and users

C.

native integration that helps secure applications across multiple cloud platforms or on-premises environments

D.

encrypts data that is stored on endpoints

E.

allows for centralized management of endpoint device applications and configurations

Buy Now
Questions 198

An organization is implementing AAA for their users. They need to ensure that authorization is verified for every command that is being entered by the network administrator. Which protocol must be configured in order to provide this capability?

Options:

A.

EAPOL

B.

SSH

C.

RADIUS

D.

TACACS+

Buy Now
Questions 199

When a next-generation endpoint security solution is selected for a company, what are two key

deliverables that help justify the implementation? (Choose two.)

Options:

A.

signature-based endpoint protection on company endpoints

B.

macro-based protection to keep connected endpoints safe

C.

continuous monitoring of all files that are located on connected endpoints

D.

email integration to protect endpoints from malicious content that is located in email

E.

real-time feeds from global threat intelligence centers

Buy Now
Questions 200

A customer has various external HTTP resources available including Intranet Extranet and Internet, with a

proxy configuration running in explicit mode. Which method allows the client desktop browsers to be configured

to select when to connect direct or when to use the proxy?

Options:

A.

Transport mode

B.

Forward file

C.

PAC file

D.

Bridge mode

Buy Now
Questions 201

After deploying a Cisco ESA on your network, you notice that some messages fail to reach their destinations.

Which task can you perform to determine where each message was lost?

Options:

A.

Configure the trackingconfig command to enable message tracking.

B.

Generate a system report.

C.

Review the log files.

D.

Perform a trace.

Buy Now
Questions 202

A logistics company issues corporate laptops that must automatically establish a Cisco Secure Client VPN tunnel whenever users are outside the office and connected to an untrusted external network. Cisco Secure Firewall Threat Defense is the VPN headend and is already configured with remote-access profiles, address pools, and a PKI that distributes both machine and user certificates to endpoints. Management requires the tunnel to come up unattended before any user signs in to a laptop. Device-based authentication must be used, and the client must distinguish the corporate LAN from outside networks. The VPN must be connected when a user is outside the corporate network. Which configuration action must be performed to meet the requirements?

Options:

A.

Configure a Management VPN tunnel with user-certificate authentication for unattended connectivity.

B.

Configure Trusted Network Detection and Start Before Login with machine-certificate authentication for the client.

C.

Configure Trusted Network Detection using cached domain credentials for client authentication.

D.

Implement Start Before Login paired with user-certificate authentication in the profile.

Buy Now
Questions 203

Which action configures the IEEE 802.1X Flexible Authentication feature to support Layer 3 authentication mechanisms?

Options:

A.

Add MAB into the switch to allow redirection to a Layer 3 device for authentication.

B.

Identify the devices using this feature and create a policy that allows them to pass Layer 2 authentication.

C.

Modify the Dot1x configuration on the VPN server to send Layer 3 authentications to an external authentication database.

D.

Configure WebAuth so the hosts are redirected to a web page for authentication.

Buy Now
Questions 204

What are two reasons for implementing a multifactor authentication solution such as Duo Security provide to an

organization? (Choose two)

Options:

A.

flexibility of different methods of 2FA such as phone callbacks, SMS passcodes, and push notifications

B.

single sign-on access to on-premises and cloud applications

C.

integration with 802.1x security using native Microsoft Windows supplicant

D.

secure access to on-premises and cloud applications

E.

identification and correction of application vulnerabilities before allowing access to resources

Buy Now
Questions 205

A mall provides security services to customers with a shared appliance. The mall wants separation of

management on the shared appliance. Which ASA deployment mode meets these needs?

Options:

A.

routed mode

B.

transparent mode

C.

multiple context mode

D.

multiple zone mode

Buy Now
Questions 206

Which two capabilities of Cisco Secure Workload facilitate the detection of lateral movement within data-center and cloud environments? (Choose two.)
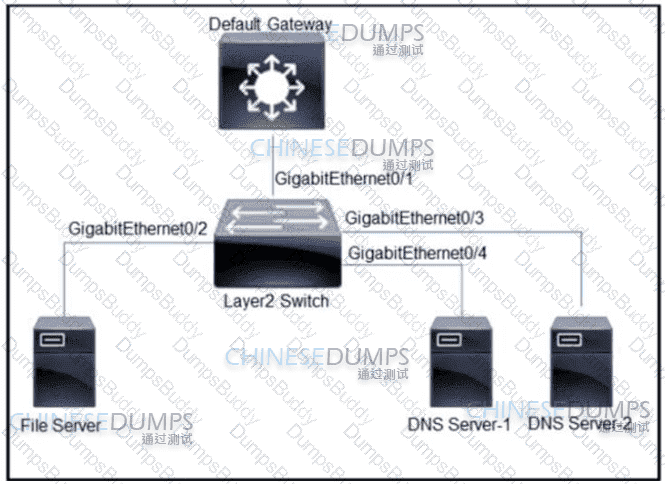
Options:

A.

Dynamic updates to firewall rules based on user access

B.

Integration with threat intelligence for identifying malicious IP addresses

C.

Automatic blocking of all inbound and outbound traffic

D.

Real-time visibility into communication patterns between workloads

E.

Recommendations for implementing VLANs for network segmentation

Buy Now
Questions 207

350-701 Question 207

Refer to the exhibit. All servers are in the same VLAN/Subnet. DNS Server-1 and DNS Server-2 must communicate with each other, and all servers must communicate with default gateway multilayer switch. Which type of private VLAN ports should be configured to prevent communication between DNS servers and the file server?

Options:

A.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as isolated port, and GigabitEthernet0/3 and GigabitEthernet0/4 as promiscuous ports.

B.

Configure GigabitEthernet0/1 as community port, GigabitEthernet0/2 as promiscuous port, Gigabit Ethernet0/3 and GigabitEthernet0/4 as isolated ports C. Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as isolated port and GigabitEthernet0/3 and GrgabitEthernet0/4 as community ports

C.

Configure GigabitEthernet0/1 as promiscuous port, GigabitEthernet0/2 as community port, and GigabitEthernet0/3 and GrgabitEthernet0/4 as isolated ports.

Buy Now
Questions 208

Which function is performed by certificate authorities but is a limitation of registration authorities?

Options:

A.

accepts enrollment requests

B.

certificate re-enrollment

C.

verifying user identity

D.

CRL publishing

Buy Now
Questions 209

What is the function of SDN southbound API protocols?

Options:

A.

to allow for the dynamic configuration of control plane applications

B.

to enable the controller to make changes

C.

to enable the controller to use REST

D.

to allow for the static configuration of control plane applications

Buy Now
Questions 210

How does Cisco AMP for Endpoints provide next-generation protection?

Options:

A.

It encrypts data on user endpoints to protect against ransomware.

B.

It leverages an endpoint protection platform and endpoint detection and response.

C.

It utilizes Cisco pxGrid, which allows Cisco AMP to pull threat feeds from threat intelligence centers.

D.

It integrates with Cisco FTD devices.

Buy Now
Questions 211

Which VPN technology supports a multivendor environment and secure traffic between sites?

Options:

A.

FlexVPN

B.

DMVPN

C.

SSL VPN

D.

GET VPN

Buy Now
Questions 212

Which two devices support WCCP for traffic redirection? (Choose two.)

Options:

A.

Cisco Secure Web Appliance

B.

Cisco IOS

C.

proxy server

D.

Cisco ASA

E.

Cisco IPS

Buy Now
Questions 213

A pharmaceutical research facility has implemented a “Clean Room” network segment to protect sensitive research data and automated manufacturing equipment. Strict compliance requirements mandate that all network traffic logs from the Cisco Secure Firewall serving the segment be forwarded to Splunk for auditing. A Splunk Universal Forwarder is deployed locally on the log-collection servers to monitor syslog files. The engineer must configure the Universal Forwarder to monitor the local syslog files and assign a specific source type for proper ingestion into Splunk. Which stanza configuration must be used to meet the requirements?

Options:

A.

inputs.conf using [monitor:///var/log/syslog]

B.

server.conf using [monitor:///syslog]

C.

props.conf using [syslog]

D.

outputs.conf using [tcpout]

Buy Now
Questions 214

Which feature of a secure CI/CD pipeline defends container workloads against detected exploits, application flaws, configuration errors, and policy violations?

Options:

A.

Control groups

B.

Separation of duties

C.

Runtime protection

D.

Cloud-native firewalling

Buy Now
Questions 215

Which baseline form of telemetry is recommended for network infrastructure devices?

Options:

A.

SDNS

B.

NetFlow

C.

passive taps

D.

SNMP

Buy Now
Questions 216

Which security solution protects users leveraging DNS-layer security?

Options:

A.

Cisco ISE

B.

Cisco FTD

C.

Cisco Umbrella

D.

Cisco ASA

Buy Now
Questions 217

Which Cisco platform processes behavior baselines, monitors for deviations, and reviews for malicious processes in data center traffic and servers while performing software vulnerability detection?

Options:

A.

Cisco Tetration

B.

Cisco ISE

C.

Cisco AMP for Network

D.

Cisco AnyConnect

Buy Now
Questions 218

Drag and drop the Cisco CWS redirection options from the left onto the capabilities on the right.
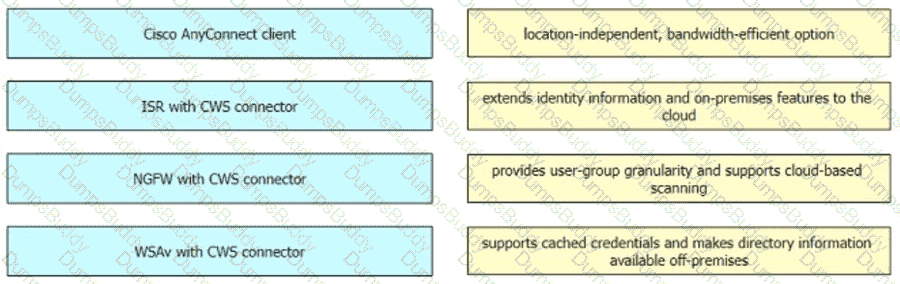
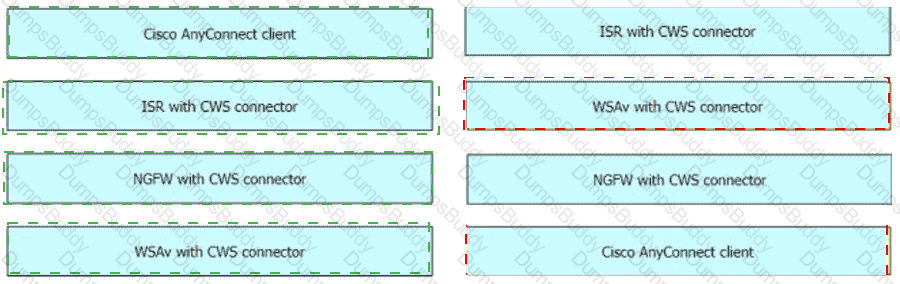
350-701 Question 218

Options:

Buy Now
Questions 219

What are two security benefits of an MDM deployment? (Choose two.)

Options:

A.

robust security policy enforcement

B.

privacy control checks

C.

on-device content management

D.

distributed software upgrade

E.

distributed dashboard

Buy Now
Questions 220

What does Cisco ISE use to collect endpoint attributes that are used in profiling?

Options:

A.

probes

B.

posture assessment

C.

Cisco AnyConnect Secure Mobility Client

D.

Cisco pxGrid

Buy Now
Questions 221

An organization is implementing URL blocking using Cisco Umbrella. The users are able to go to some sites but other sites are not accessible due to an error. Why is the error occurring?

Options:

A.

Client computers do not have the Cisco Umbrella Root CA certificate installed.

B.

IP-Layer Enforcement is not configured.

C.

Intelligent proxy and SSL decryption is disabled in the policy.

D.

Client computers do not have an SSL certificate deployed from an internal CA server.

Buy Now
Questions 222

Which two characteristics of messenger protocols make data exfiltration difficult to detect and prevent?

(Choose two)

Options:

A.

Outgoing traffic is allowed so users can communicate with outside organizations.

B.

Malware infects the messenger application on the user endpoint to send company data.

C.

Traffic is encrypted, which prevents visibility on firewalls and IPS systems.

D.

An exposed API for the messaging platform is used to send large amounts of data.

E.

Messenger applications cannot be segmented with standard network controls

Buy Now
Questions 223

Which solution protects hybrid cloud deployment workloads with application visibility and segmentation?

Options:

A.

Nexus

B.

Stealthwatch

C.

Firepower

D.

Tetration

Buy Now
Questions 224

What is a characteristic of an EDR solution and not of an EPP solution?

Options:

A.

stops all ransomware attacks

B.

retrospective analysis

C.

decrypts SSL traffic for better visibility

D.

performs signature-based detection

Buy Now
Questions 225

A company discovered an attack propagating through their network via a file. A custom file policy was created in order to track this in the future and ensure no other endpoints execute the infected file. In addition, it was discovered during testing that the scans are not detecting the file as an indicator of compromise. What must be done in order to ensure that the created is functioning as it should?

Options:

A.

Create an IP block list for the website from which the file was downloaded

B.

Block the application that the file was using to open

C.

Upload the hash for the file into the policy

D.

Send the file to Cisco Threat Grid for dynamic analysis

Buy Now
Questions 226

A network administrator has configured TACACS on a network device using the key Cisc0467380030 tor authentication purposes. However, users are unable to authenticate. TACACS server is reachable, but authentication is tailing. Which configuration step must the administrator complete?

Options:

A.

Implement synchronized system clock on TACACS server that matches the network device.

B.

Install a compatible operating system version on the TACACS server.

C.

Configure the TACACS key on the server to match with the network device.

D.

Apply an access control list on TACACS server to allow communication with the network device.

Buy Now
Questions 227

A network administrator is setting up Cisco FMC to send logs to Cisco Security Analytics and Logging (SaaS). The network administrator is anticipating a high volume of logging events from the firewalls and wants lo limit the strain on firewall resources. Which method must the administrator use to send these logs to Cisco Security Analytics and Logging?

Options:

A.

SFTP using the FMCCLI

B.

syslog using the Secure Event Connector

C.

direct connection using SNMP traps

D.

HTTP POST using the Security Analytics FMC plugin

Buy Now
Questions 228

Which product allows Cisco FMC to push security intelligence observable to its sensors from other products?

Options:

A.

Encrypted Traffic Analytics

B.

Threat Intelligence Director

C.

Cognitive Threat Analytics

D.

Cisco Talos Intelligence

Buy Now
Questions 229

Refer to the exhibit.

350-701 Question 229

A network administrator configured a site-to-site VPN tunnel between two Cisco IOS routers, and hosts are unable to communicate between two sites of VPN. The network administrator runs the debug crypto isakmp sa command to track VPN status. What is the problem according to this command output?

Options:

A.

hashing algorithm mismatch

B.

encryption algorithm mismatch

C.

authentication key mismatch

D.

interesting traffic was not applied

Buy Now
Questions 230

Which ASA deployment mode can provide separation of management on a shared appliance?

Options:

A.

DMZ multiple zone mode

B.

transparent firewall mode

C.

multiple context mode

D.

routed mode

Buy Now
Questions 231

Which Talos reputation center allows for tracking the reputation of IP addresses for email and web traffic?

Options:

A.

IP and Domain Reputation Center

B.

File Reputation Center

C.

IP Slock List Center

D.

AMP Reputation Center

Buy Now
Questions 232

A company deploys an application that contains confidential data and has a hybrid hub-and-spoke topology. The hub resides in a public cloud environment, and the spoke resides on-premises. An engineer must secure the application to ensure that confidential data in transit between the hub-and-spoke servers is accessible only to authorized users. The engineer performs these configurations:

Segregation of duties

Role-based access control

Privileged access management

What must be implemented to protect the data in transit?

Options:

A.

MD5

B.

AES-256

C.

SHA-512

D.

TLS 1.3

Buy Now
Questions 233

Which type of DNS abuse exchanges data between two computers even when there is no direct connection?

Options:

A.

Malware installation

B.

Command-and-control communication

C.

Network footprinting

D.

Data exfiltration

Buy Now
Questions 234

A network engineer is enabling RADIUS CoA on a fleet of Cisco Catalyst switches so that Cisco ISE can quarantine compromised endpoints in real time. To uniquely target an active session for disconnect or reauthorization, Cisco ISE must include IETF attribute 31 to identify the endpoint. Which configuration action must be performed on Cisco ISE to meet the requirement?

Options:

A.

Configure the Calling-Station-ID attribute for CoA session identification.

B.

Apply the Message-Authenticator attribute for endpoint session lookup.

C.

Implement the Acct-Session-ID attribute for matching the active session.

D.

Use the NAS-Port-ID attribute for the CoA disconnect request.

Buy Now
Questions 235

Refer to the exhibit.

350-701 Question 235

A Cisco Secure Endpoint malware event shows that a file was convicted as malicious and that its remediation status is Quarantine Failed. Before escalating the incident, the analyst must determine what can be concluded from the available event data. What is occurring based on the logs?

Options:

A.

The event data does not establish whether the threat remains present or was remediated through another mechanism.

B.

The failed-quarantine status proves that the endpoint was unable to apply the configured remediation policy.

C.

The failed-quarantine status proves that the file remained accessible to the operating system after the remediation attempt.

D.

The failed-quarantine status proves that the threat continued executing after the remediation attempt.

Buy Now
Questions 236

Refer to the exhibit.

350-701 Question 236

What will occur when this device tries to connect to the port?

Options:

A.

802.1X will not work, but MAB will start and allow the device on the network.

B.

802.1X will not work and the device will not be allowed network access

C.

802 1X will work and the device will be allowed on the network

D.

802 1X and MAB will both be used and ISE can use policy to determine the access level

Buy Now
Questions 237

Which telemetry data captures variations seen within the flow, such as the packets TTL, IP/TCP flags, and payload length?

Options:

A.

interpacket variation

B.

software package variation

C.

flow insight variation

D.

process details variation

Buy Now
Questions 238

Drag and drop the suspicious patterns for the Cisco Tetration platform from the left onto the correct definitions on the right.
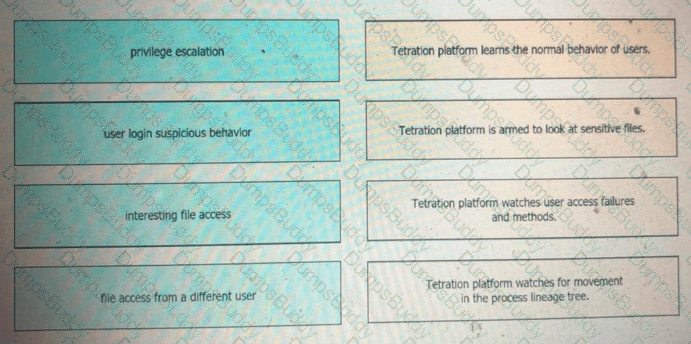
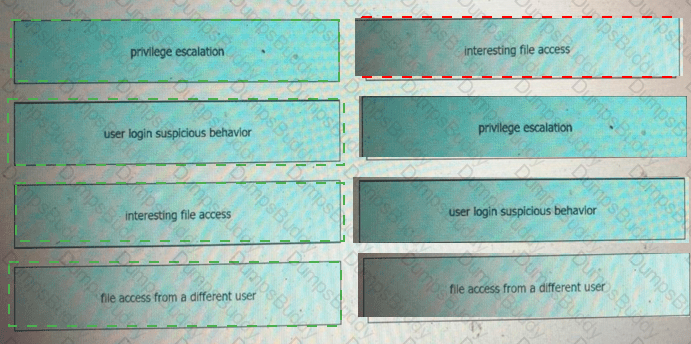
350-701 Question 238

Options:

Buy Now
Questions 239

Which cloud service model offers an environment for cloud consumers to develop and deploy applications

without needing to manage or maintain the underlying cloud infrastructure?

Options:

A.

PaaS

B.

XaaS

C.

IaaS

D.

SaaS

Buy Now
Questions 240

A university policy must allow open access to resources on the Internet for research, but internal workstations are exposed to malware. Which Cisco AMP feature allows the engineering team to determine whether a file is installed on a selected few workstations?

Options:

A.

file prevalence

B.

file discovery

C.

file conviction

D.

file manager

Buy Now
Exam Code: 350-701
Exam Name: Implementing and Operating Cisco Security Core Technologies (SCOR 350-701 v2.0)
Last Update: Oct 17, 2026
Questions: 801

PDF + Testing Engine

$144.99

Testing Engine

$109.99

PDF (Q&A)

$94.99