300-710 Securing Networks with Cisco Firepower (300-710 SNCF) v1.2 Questions and Answers
An organization has seen a lot of traffic congestion on their links going out to the internet There is a Cisco Firepower device that processes all of the traffic going to the internet prior to leaving the enterprise. How is the congestion alleviated so that legitimate business traffic reaches the destination?
An engineer is configuring URL filtering tor a Cisco Secure Firewall Threat Defense device in Cisco Secure Firewall Management Centre. Use ' s must receive a warning when they access
..wwww badaduitsito com with the option of continuing to the website if they choose to No other websites should he blocked. Which two actions must the engineer take to moot these requirements?
An engineer is configuring a Cisco Secure Firewall Threat Defense device to operate in transparent mode between two switch stacks. VLAN 10 is used for in-band management on both switch stacks. Which two actions are required on the device to inspect traffic between the switch stacks without interrupting network traffic? (Choose two.)
Which two remediation options are available when Cisco FMC is integrated with Cisco ISE? (Choose two.)
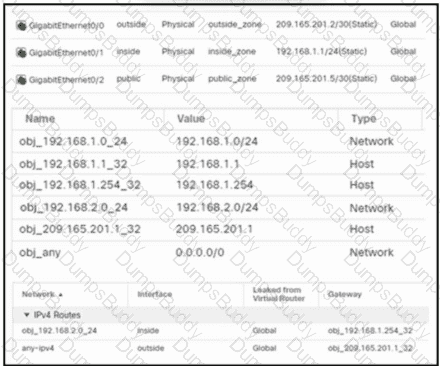
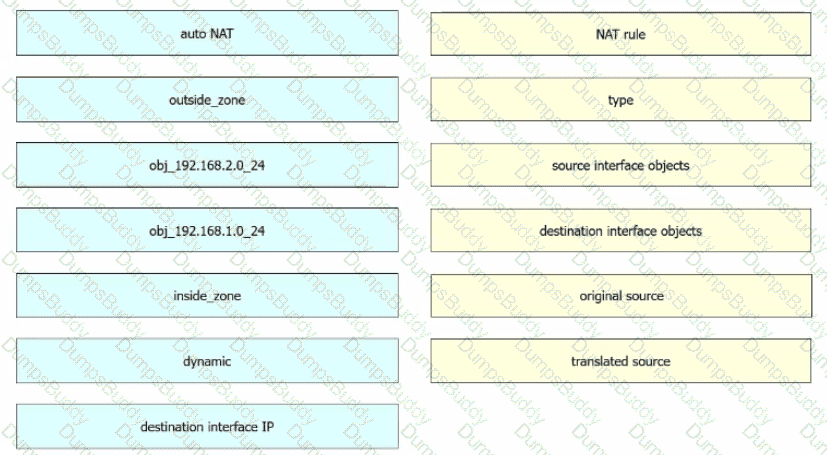
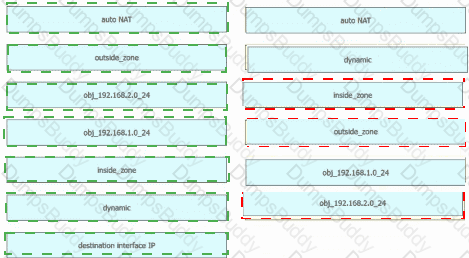
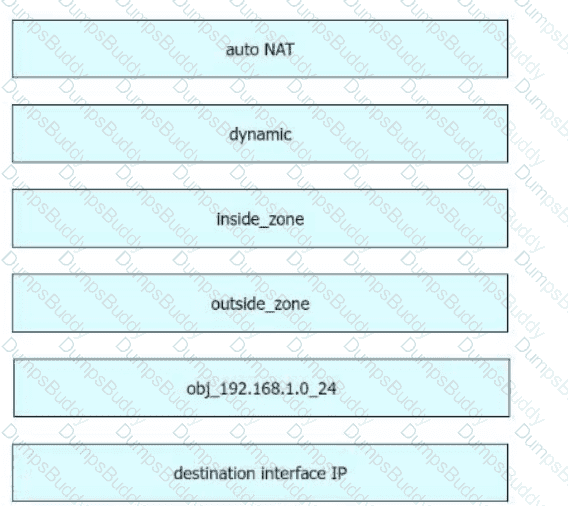
Refer to the exhibit. An engineer configures a NAT rule allowing clients to use the internet only if clients are located on the directly connected internal network. Dynamic auto PAT must be configured. Drag and drop the NAT rules from the left onto the corresponding targets on the right. Not all options are used.
 A screenshot of a computer AI-generated content may be incorrect.
An administrator must fix a network problem whereby traffic from the inside network to a webserver is not getting through an instance of Cisco Secure Firewall Threat Defense. Which command must the administrator use to capture packets to the webserver that are dropped by Secure Firewall Throat Defense and resold the issue?
Which two OSPF routing features are configured in Cisco FMC and propagated to Cisco FTD? (Choosetwo.)
Which protocol establishes network redundancy in a switched Firepower device deployment?
An engineer must configure a Cisco FMC dashboard in a child domain. Which action must be taken so that the dashboard is visible to the parent domain?
Which firewall design allows a firewall to forward traffic at layer 2 and layer 3 for the same subnet?
What is the result of specifying of QoS rule that has a rate limit that is greater than the maximum throughput of an interface?
Upon detecting a flagrant threat on an endpoint, which two technologies instruct Cisco Identity Services Engine to contain the infected endpoint either manually or automatically? (Choose two.)
A network administrator reviews the file report for the last month and notices that all file types, except exe. show a disposition of unknown. What is the cause of this issue?
Which Cisco Secure Firewall Threat Defense interface mode must be deployed when implementing an IPS that must receive and retransmit all traffic unless the traffic is explicitly dropped?
In a multi-tennent deployment where multiple domains are in use. which update should be applied outside of the Global Domain?
An engineer is configuring Cisco Security Devices by using Cisco Secure Firewall Management Center. Which configuration command must be run to compare the CA certificate bundle on the local system to the latest CA bundle from the Cisco server?
An engineer must permit SSH on the inside interface of a Cisco Secure Firewall Threat Defense device. SSH is currently permitted only on the management interface. Which type of policy
must the engineer configure?
What is an advantage of adding multiple inline interface pairs to the same inline interface set when deploying an asynchronous routing configuration?
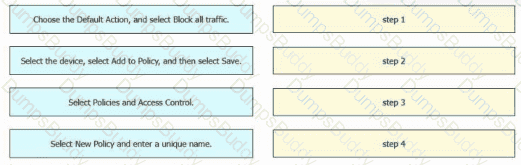
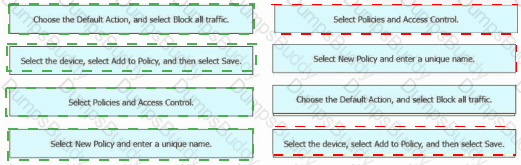
An engineer must create a basic access control policy in the Cisco Secure Firewall Management Center to block all traffic by default. Drag and drop the configuration actions from the left into sequence on the right.
A network administrator observes an attempted attack from a specific IP address in Cisco Secure Firewall Management Center. Which Cisco security tool can be used directly from the Secure Firewall Management Center web interface to obtain additional information about the IP address?
Which action should you take when Cisco Threat Response notifies you that AMP has identified a file as malware?
An engineer must configure an ERSPAN passive interface on a Cisco Secure IPS by using the Cisco Secure Firewall Management Center. These configurations have been performed already:
Configure the passive interface.
Configure the ERSPAN IP address.
Which two additional settings must be configured to complete the configuration? (Choose two.)
Which two dynamic routing protocols are supported in Firepower Threat Defense without using FlexConfig? (Choose two.)
A network administrator is configuring Snort inspection policies and is seeing failed deployment messages in Cisco FMC. What information should the administrator generate for Cisco TAC to help troubleshoot?
A security engineer is configuring a remote Cisco FTD that has limited resources and internet bandwidth. Which malware action and protection option should be configured to reduce the requirement for cloud lookups?
An engineer is configuring a file policy on a Cisco Secure Firewall Management Center appliance. Files with an Unknown disposition must be analyzed by Cisco Secure Malware Analytics. What must be configured on the Secure Firewall Management Center appliance?
A network administrator reviews me attack risk report and notices several Low-Impact attacks. What does this type of attack indicate?
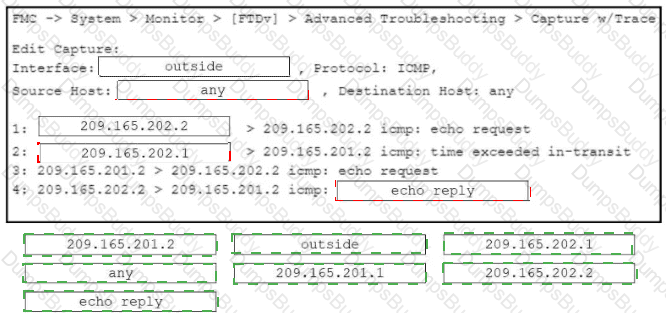
Refer to the exhibit.
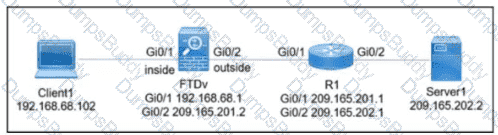
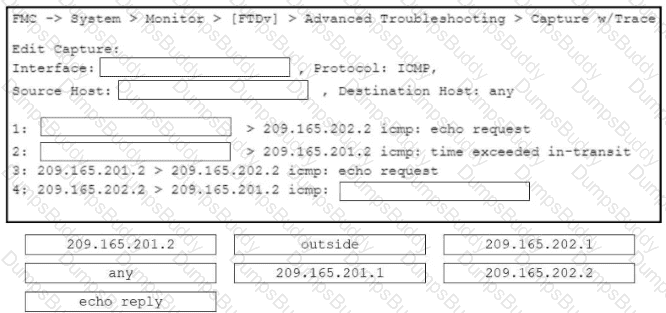
A user on a computer named Client1 is performing a traceroute to IP address 209.165.202.2. Drag and drop the appropriate values onto the fields in the Capture w/Trace configuration and captured-packet output. Not all options are used.
An engineer needs to configure remote storage on Cisco FMC. Configuration backups must be available from a secure location on the network for disaster recovery. Reports need to back up to a shared location that auditors can access with their Active Directory logins. Which strategy must the engineer use to meet these objectives?
An organization is installing a new Cisco FTD appliance in the network. An engineer is tasked with configuring access between two network segments within the same IP subnet. Which step is needed to accomplish this task?
Which two features of Cisco AMP for Endpoints allow for an uploaded file to be blocked? (Choose two.)
An engineer must configure high availability for the Cisco Firepower devices. The current network topology does not allow for two devices to pass traffic concurrently. How must the devices be implemented in this environment?
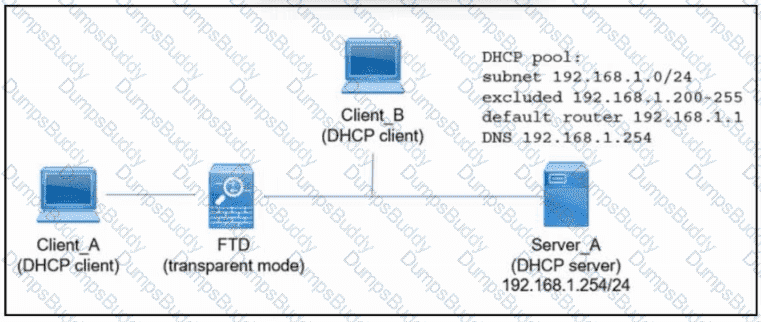
Refer to the exhibit. An engineer is deploying a new instance of Cisco Secure Firewall Threat Defense. Which action must the engineer take next so that Client_A and Client_B receive an IP address via DHCP from Server_A?
A consultant Is working on a project where the customer is upgrading from a single Cisco Firepower 2130 managed by FDM to a pair of Cisco Firepower 2130s managed oy FMC tor nigh availability. The customer wants the configures of the existing device being managed by FDM to be carried over to FMC and then replicated to the additional: device being added to create the high availability pair. Which action must the consultant take to meet this requirement?
A hospital network needs to upgrade their Cisco FMC managed devices and needs to ensure that a disaster recovery process is in place. What must be done in order to minimize downtime on the network?
Which two solutions are used to access and view aggregated log data from the firewalls using Cisco Security Analytics and Logging? (Choose two.)
When creating a report template, how can the results be limited to show only the activity of a specific subnet?
Refer to the exhibit.
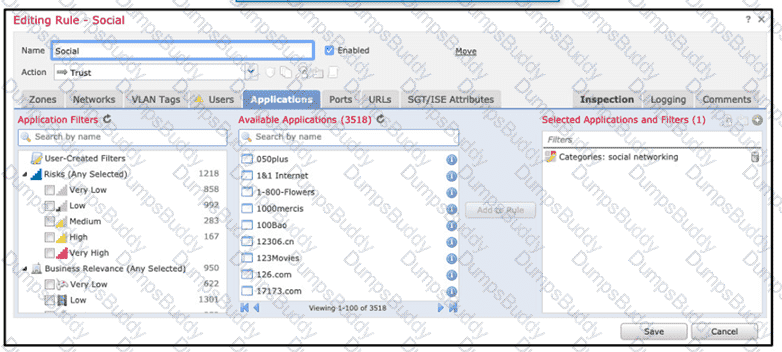
An organization has an access control rule with the intention of sending all social media traffic for inspection After using the rule for some time, the administrator notices that the traffic is not being inspected, but is being automatically allowed What must be done to address this issue?
Which two conditions are necessary for high availability to function between two Cisco FTD devices? (Choose two.)
An engineer is monitoring network traffic from their sales and product development departments, which are on two separate networks What must be configured in order to maintain data privacy for both departments?
Refer to the exhibit.
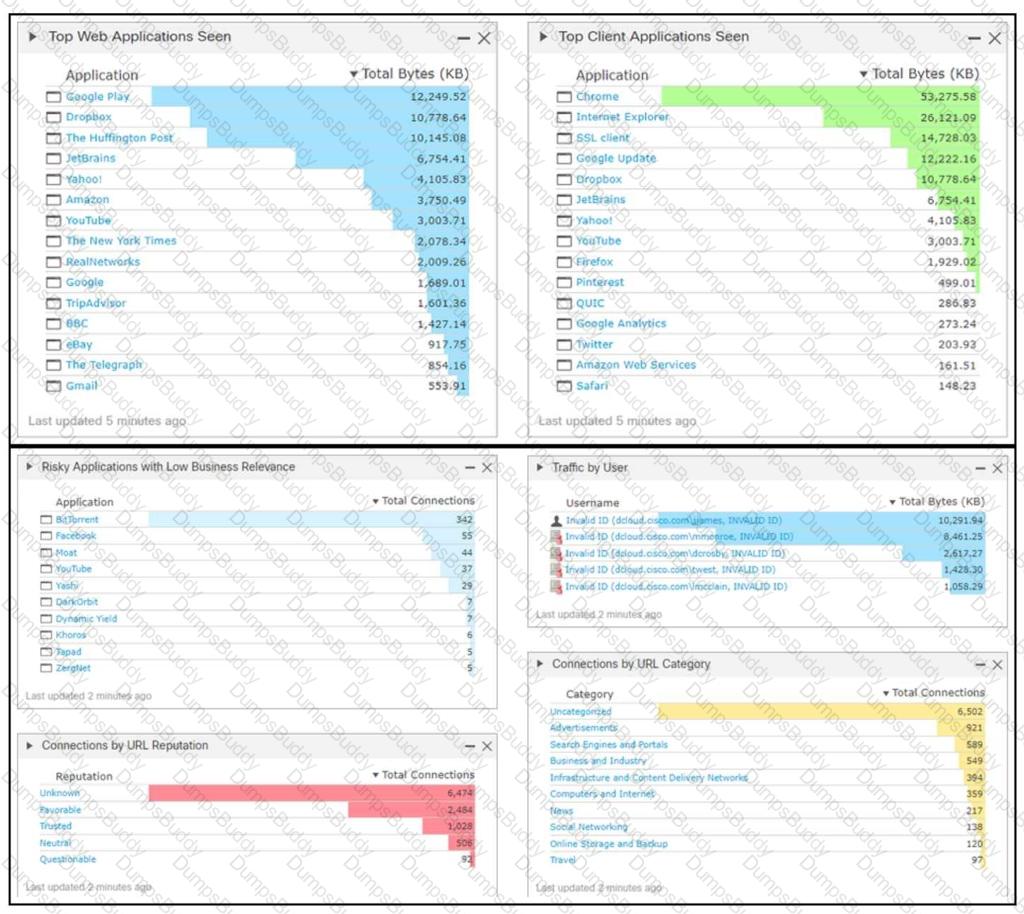
An engineer analyzes a Cisco Firepower Management Center dashboard. Which action must the engineer take to decrease the application usage risk?
A network engineer detects a connectivity issue between Cisco Secure Firewall Management Centre and Cisco Secure Firewall Threat Defense Initial troubleshooting indicates that heartbeats and events not being received. The engineer re-establishes the secure channels between both peers Which two commands must the engineer run to resolve the issue? (Choose two.)
A network engineer must configure an existing firewall to have a NAT configuration. The now configuration must support more than two interlaces per context. The firewall has previously boon operating transparent mode. The Cisco Secure Firewall Throat Defense (FTD) device has been deregistered from Cisco Secure Firewall Management Center (FMC). Which set of configuration actions must the network engineer take next to meet the requirements?
An engineer must deploy a high-availability pair that includes two Cisco Secure Firewall Threat Defense devices. The deployment must provide a mechanism that protects synchronization traffic between the members. Which action must the engineer take?
An engineer is tasked with deploying an internal perimeter firewall that will support multiple DMZs Each DMZ has a unique private IP subnet range. How is this requirement satisfied?
Encrypted Visibility Engine (EVE) is enabled under which lab on an access control policy in Cisco Secure Firewall Management Centre?
An engineer must implement Cisco Secure Firewall transparent mode due to a new server recently being added that must communicate with an existing server that is currently separated by the firewall. Which implementation action must be taken next by the engineer to accomplish the goal?
A security analyst is investigating a potential network compromise. The analyst must produce a report of the suspicious activity from Cisco Secure Firewall Management Center. Which two details must be included in the report to assist the investigation? (Choose two.)
Refer to the exhibit.
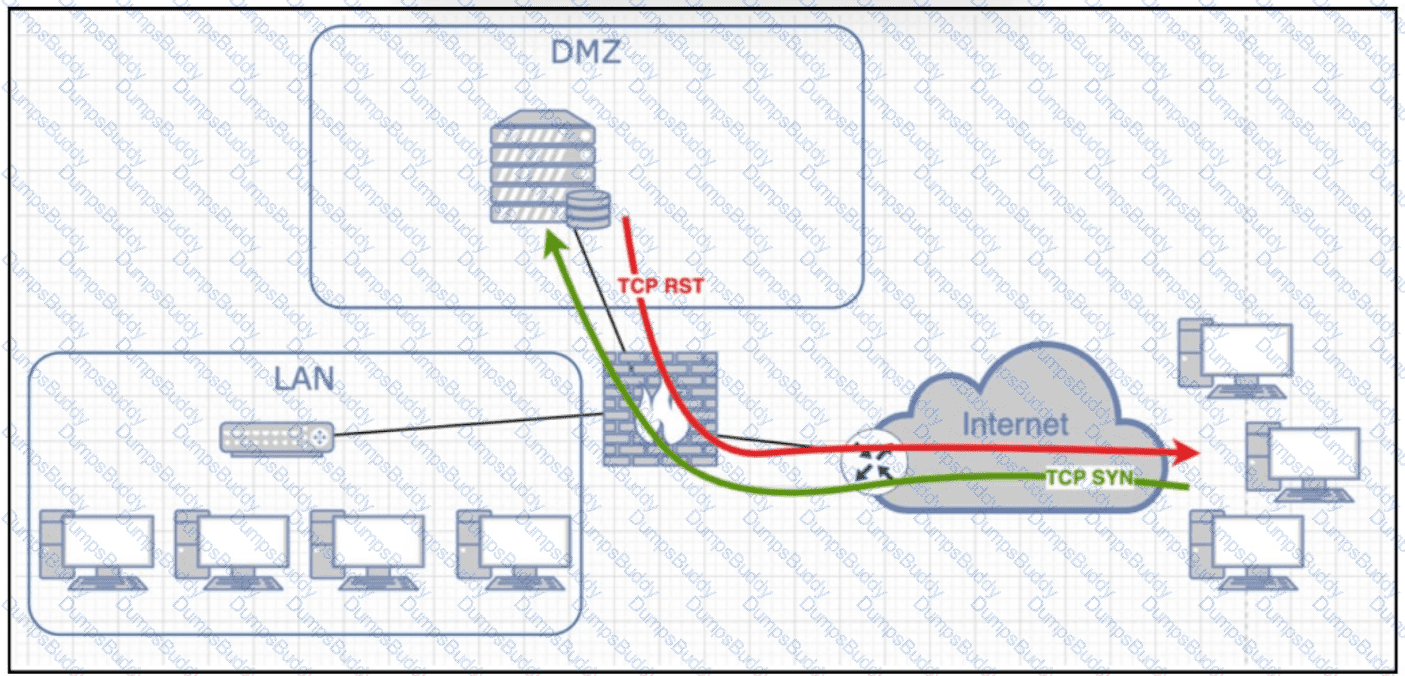
Following a critical incident, an engineer must determine why a server in the DMZ is sending TCP RST responses. Internet users can access the application but cannot view its main webpage. Where must the engineer capture the traffic to identify and resolve the issue?
An engineer is reviewing an existing custom server fingerprint on a Cisco Secure Firewall because the current information is inaccurate. Which action must the engineer take to improve the accuracy of the network discovery rules?
A company is in the process of deploying intrusion prevention with Cisco FTDs managed by a Cisco FMC. An engineer must configure policies to detect potential intrusions but not block the suspicious traffic. Which action accomplishes this task?
Which file format can standard reports from Cisco Secure Firewall Management Center be downloaded in?
An engineer is configuring a Cisco Secure Firewall Management Center appliance. The company requires the use of a TAXII server in Threat Intelligence Director and requires the Action to be set to Block. On which two object types can the engineer configure the Block action? (Choose two.)
Which Cisco FMC report gives the analyst information about the ports and protocols that are related to the configured sensitive network for analysis?
An engineer is configuring two new Cisco FTD devices to replace the existing high availability firewall pair in a highly secure environment. The information exchanged between the FTD devices over the failover link must be encrypted. Which protocol supports this on the Cisco FTD?
A network administrator is migrating from a Cisco ASA to a Cisco FTD.
EIGRP is configured on the Cisco ASA but it is not available in the Cisco FMC.
Which action must the administrator take to enable this feature on the Cisco FTD?
An engineer is troubleshooting a device that cannot connect to a web server. The connection is initiated from the Cisco FTD inside interface and attempting to reach 10.0.1.100 over the non-standard port of 9443 The host the engineer is attempting the connection from is at the IP address of 10.20.10.20. In order to determine what is happening to the packets on the network, the engineer decides to use the FTD packet capture tool Which capture configuration should be used to gather the information needed to troubleshoot this issue?
A)
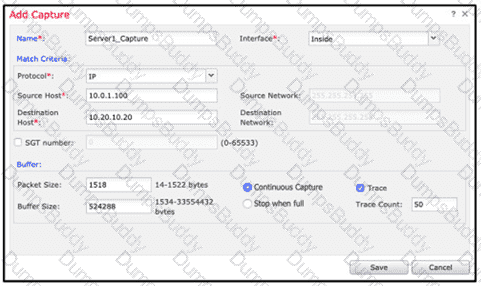
B)
C)
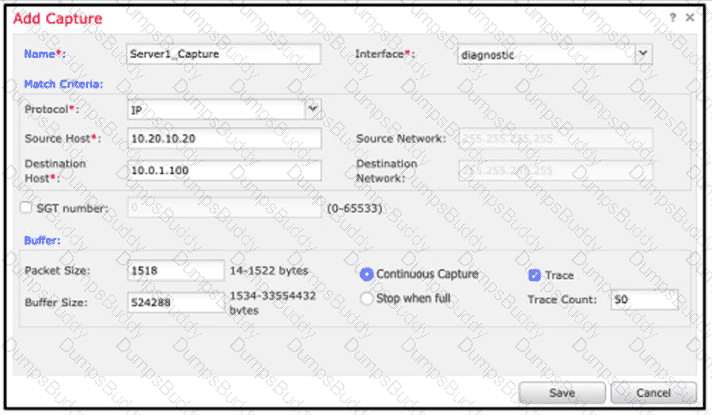
D)
An engineer is deploying a Cisco ASA Secure Firewall module. The engineer must be able to examine traffic without impacting the network, and the ASA has been deployed with a single context. Which ASA Secure Firewall module deployment mode must be implemented to meet the requirements?
A network administrator is trying to convert from LDAP to LDAPS for VPN user authentication on a Cisco FTD. Which action must be taken on the Cisco FTD objects to accomplish this task?
A network engineer must provide a high-level statistical summary of a Cisco Secure Firewall Threat Defense device. The organization is approaching its peak season, so network downtime must be minimized. Which type of report must the network engineer use?
Within an organization ' s high availability environment where both firewalls are passing traffic, traffic must be segmented based on which department it is destined for. Each department is situated on a different LAN. What must be configured to meet these requirements?
Refer to the exhibit.
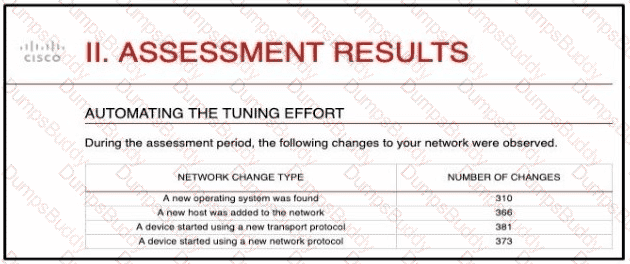
And engineer is analyzing the Attacks Risk Report and finds that there are over 300 instances of new operating systems being seen on the network How is the Firepower configuration updated to protect these new operating systems?
An engineer must deploy a high-availability that includes two Cisco Secure Firewall Threat Defense devices configured as cluster. The deployment must have a mechanism that protects synchronization between cluster members Which action must the engineer take to meet the requirements?
A security engineer is adding three Cisco FTD devices to a Cisco FMC. Two of the devices have successfully registered to the Cisco FMC. The device that is unable to register is located behind a router that translates all outbound traffic to the router ' s WAN IP address. Which two steps are required for this device to register to the Cisco FMC? (Choose two.)
When do you need the file-size command option during troubleshooting with packet capture?
A VPN administrator converted an instance of Cisco Secure Firewall Threat Defense, which is managed by Cisco Secure Firewall Management Center, from using LDAP to LDAPS for
remote access VPN authentication. Which certificate must be added to allow for remote users to authenticate over the VPN?
Which two types of objects are reusable and supported by Cisco FMC? (Choose two.)
An engineermustconfigure a Cisco FMC dashboard in a multidomain deployment Which action must the engineer take to edit a report template from an ancestor domain?
An administrator is configuring the interface of a Cisco Secure Firewall Threat Defense device in a passive IPS deployment. The device and interface have been identified. Which set of configuration steps of the administrator take next to complete the implementation?
An engineer must investigate a connectivity issue and decides to use the packet capture feature on Cisco FTD. The goal is to see the real packet going through the Cisco FTD device and see the Snort detection actions as a part of the output. After the capture-traffic command is issued, only the packets are displayed. Which action resolves this issue?
Refer to the exhibit.
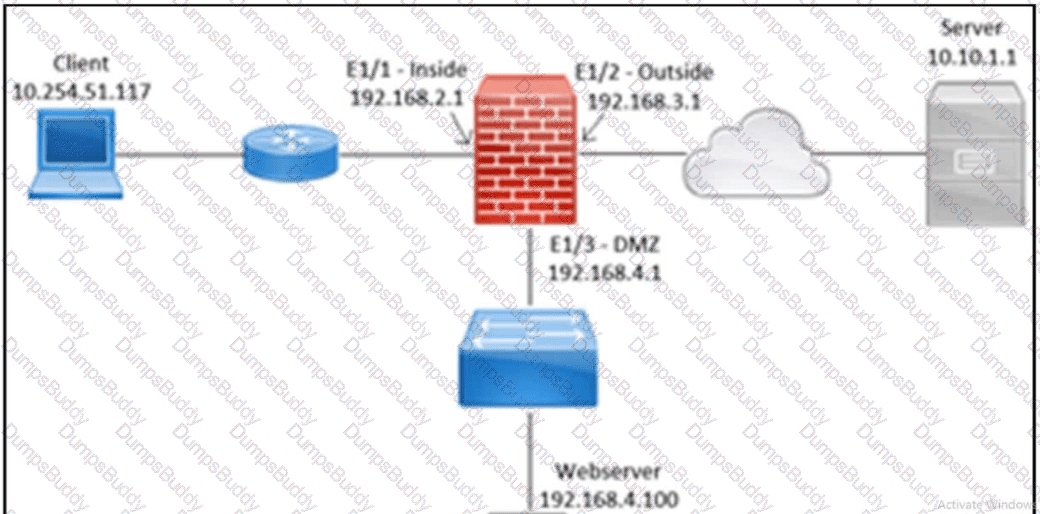
A client with IP address 10.254.51.117 connects through a Cisco Secure Firewall Threat Defense device toward a website at 10.10.1.1. The packet capture shows repeated TCP SYN packets from the client without completion of the three-way handshake. Which action must the engineer take to resolve the issue?
A VPN user is unable to conned lo web resources behind the Cisco FTD device terminating the connection. While troubleshooting, the network administrator determines that the DNS responses are not getting through the Cisco FTD What must be done to address this issue while still utilizing Snort IPS rules?
A software development company hosts the website http:dev.company.com for contractors to share code for projects they are working on with internal developers. The web server is on premises and is protected by a Cisco Secure Firewall Threat Defense appliance. The network administrator is worried about someone trying to transmit infected files to internal users via this site. Which type of policy must be able associated with an access control policy to enable Cisco Secure Firewall Malware Defense to detect and block malware?
Remote users who connect via Cisco AnyConnect to the corporate network behind a Cisco FTD device report that they get no audio when calling between remote users using their softphones. These same users can call internal users on the corporate network without any issues. What is the cause of this issue?
A network security engineer must replace a faulty Cisco FTD device in a high availability pair. Which action must be taken while replacing the faulty unit?
A network administrator is troubleshooting access to a website hosted behind a Cisco FTD device External clients cannot access the web server via HTTPS The IP address configured on the web server is 192 168 7.46 The administrator is running the command capture CAP interface outside match ip any 192.168.7.46 255.255.255.255 but cannot see any traffic in the capture Why is this occurring?
A network engineer is implementing high availability between two Cisco Secure Firewall Threat Defense devices. The engineer already checked the model, version, and number of interfaces Which two configurations must the engineer match next to meet the requirement? (Choose two.)
A network engineer wants to add a third-party threat feed into the Cisco FMC for enhanced threat detectionWhich action should be taken to accomplish this goal?
An engineer must configure the firewall to monitor traffic within a single subnet without increasing the hop count of that traffic. How would the engineer achieve this?
An engineer Is configuring a Cisco FTD device to place on the Finance VLAN to provide additional protection tor company financial data. The device must be deployed without requiring any changes on the end user workstations, which currently use DHCP lo obtain an IP address. How must the engineer deploy the device to meet this requirement?
An administrator is configuring a new report template off. of a saved search within Cisco Secure Firewall Management Centre. The goal is to use the malware analysis report template, but use a different type saved search as the basis. The report is not working. What must be considered when configuring this report template?
Which command is run at the CLI when logged in to an FTD unit, to determine whether the unit is managed locally or by a remote FMC server?
An engineer must deny ICMP traffic to the networks of separate departments that use Cisco Secure Firewall Management Center. The engineer must use the same object on the relevant device for each network. What must be configured in Secure Firewall Management Center?
An engineer must deploy a Cisco FTD device. Management wants to examine traffic without requiring network changes that will disrupt end users. Corporate security policy requires the separation of management traffic from data traffic and the use of SSH over Telnet for remote administration. How must the device be deployed to meet these requirements?
Which protocol is needed to exchange threat details in rapid threat containment on Cisco FMC?
An engineer wants to perform a packet capture on the Cisco FTD to confirm that the host using IP address 192 168.100.100 has the MAC address of 0042 7734.103 to help troubleshoot aconnectivity issue What is the correct tcpdump command syntax to ensure that the MAC address appears in the packet capture output?
An organization is implementing Cisco FTD using transparent mode in the network. Which rule in the default Access Control Policy ensures that this deployment does not create a loop in the network?
A network engineer must configure the cabling between a Cisco Secure Firewall Threat Defense appliance and a network so the Secure Firewall Threat Defense appliance performs inline to analyze and tune generated intrusion events before going live. Which Secure Firewall Threat Defense interface mode must the engineer use?
A network administrator discovers that a user connected to a file server and downloaded a malware file. The Cisc FMC generated an alert for the malware event, however the user still remained connected. Which Cisco APM file rule action within the Cisco FMC must be set to resolve this issue?
A security engineer must deploy a Cisco FTD appliance as a bump in the wire to detect intrusion events without disrupting the flow of network traffic. Which two features must be configured to accomplish the task? (Choose two.)
Refer to the exhibit.
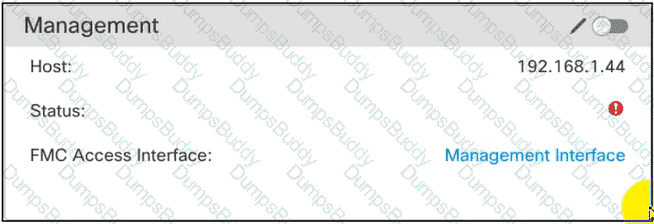
What is the effect of the existing Cisco FMC configuration?
A security engineer must create an access list object in Cisco Secure Firewall Management Center to allow traffic to IP address 10.236.131.1 but block traffic to IP address 10.236.131.0/24. Which access control entries must the engineer create?
A)
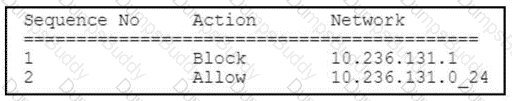
B)
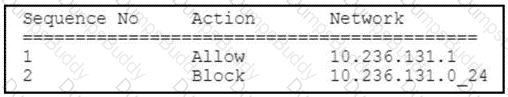
C)
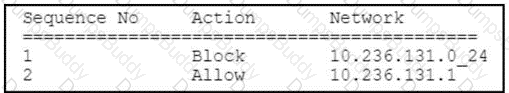
D)
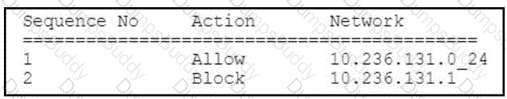
An organization is configuring a new Cisco Firepower High Availability deployment. Which actionmust be taken to ensure that failover is as seamless as possible to end users?
An engineer runs the command restore remote-manager-backup location 2.2.2.2 admin /Volume/home/admin FTD408566513.zip on a Cisco FMC. After connecting to the repository, the Cisco FTD device is unable to accept the backup file. What is the reason for this failure?
A network engineer is extending a user segment through an FTD device for traffic inspection without creating another IP subnet How is this accomplished on an FTD device in routed mode?
When packet capture is used on a Cisco Secure Firewall Threat Defense device and the packet flow is wailing on the malware query, which Snort verdict appears?
An administrator must use Cisco FMC to install a backup route within the Cisco FTD to route traffic in case of a routing failure with the primary route. Which action accomplishes this task?
An engineer is reviewing a ticket that requests to allow traffic for some devices that must connect to a server over 8699/udp. The request mentions only one IP address, 172.16.18.15, but the requestor asked for the engineer to open the port for all machines that have been trying to connect to it over the last week. Which action must the engineer take to troubleshoot this issue?
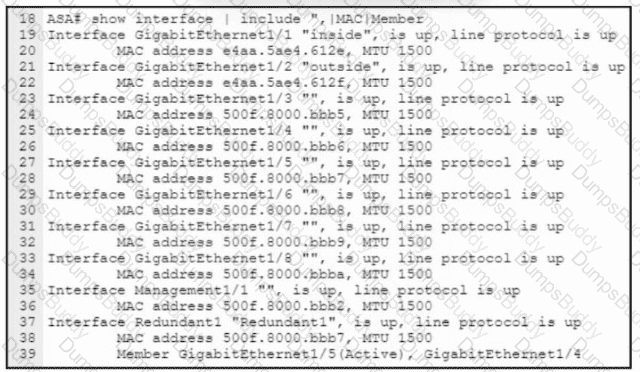
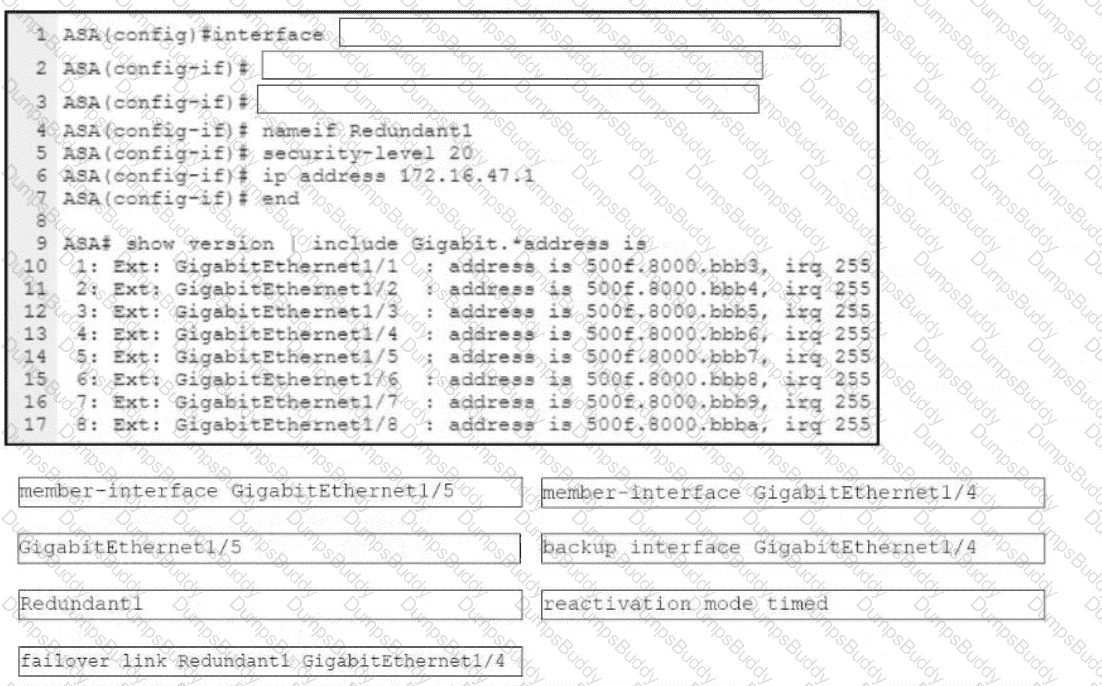
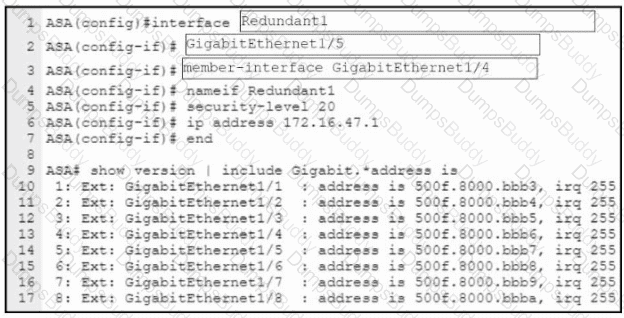
Refer to the exhibit. An engineer must configure a connection on a Cisco ASA Firewall with a Cisco Secure Firewall Services Module to ensure that the secondary interface takes over all the functions of the primary interface if the primary interface fails. Drag and drop the code snippets from the bottom onto the boxes in the CLI commands to configure the failover. Not all options are used.

 A screenshot of a computer AI-generated content may be incorrect.
An engineer is configuring two new Cisco Secure Firewall Threat Defense appliances as a high-availability pair. The high-availability pair must detect a failure on the failover link and trigger failover more quickly. Which two settings must the engineer decrease? (Choose two.)
Refer to the exhibit.
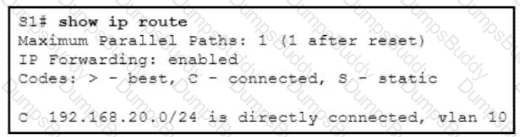
An engineer must configure a static route on the Cisco Catalyst switch to reach 192.168.10.0/24 through the 192.168.20.1 next hop. The route must use an administrative distance of 2. Which command meets the requirements?
After deploying a network-monitoring tool to manage and monitor networking devices in your organization, you realize that you need to manually upload an MIB for the Cisco FMC. In which folder should you upload the MIB file?
Network users experience issues when accessing a server on a different network segment. An engineer investigates the issue by performing packet capture on Cisco Secure Firewall Threat Defense. The engineer expects more data and suspects that not all the traffic was collected during a 15-minute can’t captured session. Which action must the engineer take to resolve the issue?
Which license type is required on Cisco ISE to integrate with Cisco FMC pxGrid?
An engineer is troubleshooting a file that is being blocked by a Cisco FTD device on the network.
The user is reporting that the file is not malicious.
Which action does the engineer take to identify the file and validate whether or not it is malicious?
A network administrator is seeing an unknown verdict for a file detected by Cisco FTD. Which malware policy configuration option must be selected in order to further analyse the file in the Talos cloud?
A network administrator configured a NAT policy that translates a public IP address to an internal web server IP address. An access policy has also been created that allows any source to reach the public IP address on port 80. The web server is still not reachable from the Internet on port 80. Which configuration change is needed?
A network security engineer must export packet captures from the Cisco FMC web browser while troubleshooting an issue. When navigating to the address https:// < FMC IP > /capture/CAPI/pcap/test.pcap. an error 403: Forbidden is given instead of the PCAP file. Which action must the engineer take to resolve this issue?
Which firewall design will allow It to forward traffic at layers 2 and 3 for the same subnet?
An engineer is configuring Cisco Secure Firewall Threat Defense managed by a Secure Firewall Management Center appliance. The company wants remote access VPN users to be reachable from the inside network. What must the engineer configure to meet the requirements?
What is a method used by Cisco Rapid Threat Containment to contain the threat in the network?
Which command is typed at the CLI on the primary Cisco FTD unit to temporarily stop running high- availability?
An engineer is troubleshooting an intermittent connectivity issue on a Cisco Secure Firewall Threat Defense appliance and must collect 24 hours ' worth of data. The engineer started a packet capture. Whenever it stopsprematurely during this time period. The engineer notices that the packet capture butter size is set to the default of 32 MB Which butter S170 is the maximum that the engineer must sot to able the packet capture to run successfully?
An engineer currently has a Cisco FTD device registered to the Cisco FMC and is assigned the address of 10 10.50.12. The organization is upgrading the addressing schemes and there is a requirement to convert the addresses to a format that provides an adequate amount of addresses on the network What should the engineer do to ensure that the new addressing takes effect and can be used for the Cisco FTD to Cisco FMC connection?
When a Cisco FTD device is configured in transparent firewall mode, on which two interface types can an IP address be configured? (Choose two.)
A network engineer is tasked with minimising traffic interruption during peak traffic limes. When the SNORT inspection engine is overwhelmed, what must be configured to alleviate this issue?
An engineer is configuring two new Cisco Secure Firewall Threat Defense devices to replace the existing firewalls. Network traffic must be analyzed for intrusion events without impacting the traffic. What must the engineer implement next to accomplish the goal?
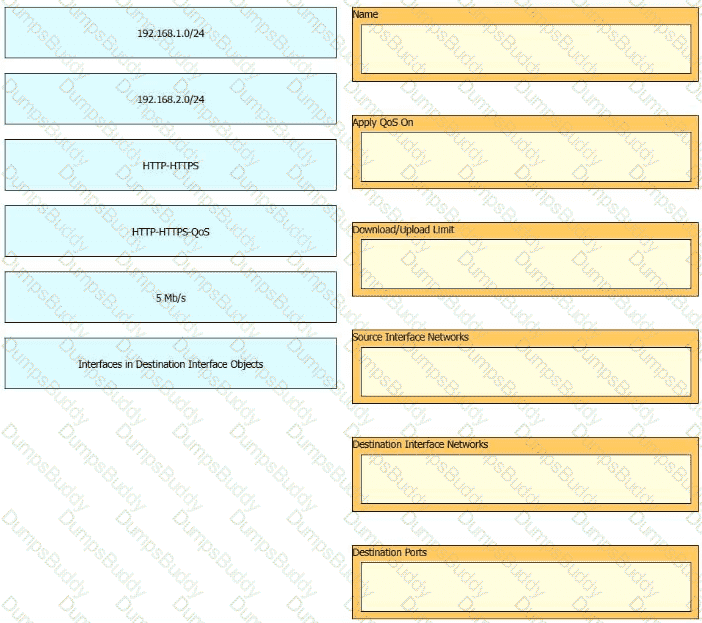
Refer to the exhibit.
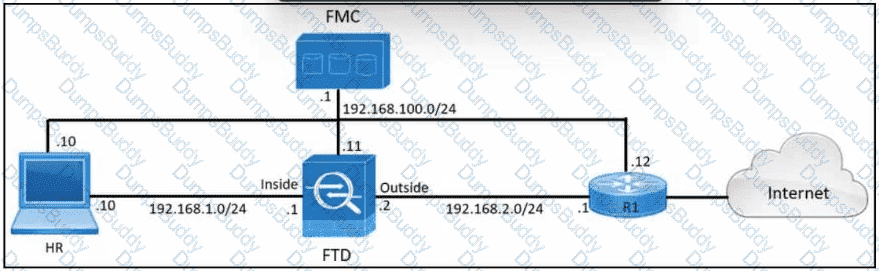
An engineer must create a QoS policy in Cisco Secure Firewall Management Center to limit HTTP and HTTPS traffic originating from users in the HR department. The download and upload limits for HTTP and HTTPS traffic must both be set to 5 Mb/s. Drag and drop the values onto the corresponding QoS rule settings.

PDF + Testing Engine
Testing Engine
PDF (Q&A)